
What should an IT asset management service report to business leaders?
An IT asset management service should give business leaders a clear view of asset costs, ownership, condition, utilisation, security risks and compliance status. It should turn this data into actionable insight, supporting decisions about budgets, renewals, replacements, risk reduction and future technology requirements.
An effective IT asset management report should translate technical records into business decisions. It should show what has changed, which issues require attention, what action is recommended, who owns that action and what the likely business consequence will be if it is delayed. The report should be concise enough for senior review while retaining enough evidence for IT, finance, procurement and compliance teams to act on it.
Start with an executive decision summary. Business leaders generally need the important exceptions before the detailed asset data. The opening section should identify:
- material changes since the previous report;
- assets or asset groups requiring a decision;
- risks that exceed the organisation’s agreed tolerance;
- upcoming renewals, replacements or contract dates;
- actions that need budget, approval or business ownership; and
- items that are overdue, blocked or dependent on another project.
Each issue should have a clear status, accountable owner, target date and recommended next step. This prevents the report from becoming a catalogue of technical information with no route to action.
Show the financial position in decision-ready terms. Leaders should be able to understand both current commitments and likely future expenditure. Depending on the organisation’s purchasing model, this may include acquisition costs, leasing arrangements, support contracts, warranties, subscriptions, renewal dates and expected replacement requirements. Costs should be grouped by department, site, service or asset category where that helps reveal concentration and prioritisation.
The report should distinguish committed expenditure from forecast requirements. It should also explain the reason for each significant recommendation, such as an approaching end-of-support date, repeated operational failure, a change in business need or a requirement to standardise equipment. This gives finance and management a basis for comparing planned investment with the consequences of deferring it.
Explain operational impact rather than listing technical faults. A report is more useful when it connects an asset to the service, team or process that depends on it. Relevant information may include recurring incidents, capacity constraints, performance concerns, critical dependencies and single points of failure. For example, a device with repeated faults may be more urgent to replace if it supports a key operational process than if an equivalent device is held as spare equipment.
Business leaders should also be able to see whether assets are appropriately allocated to current requirements. Surplus, duplicated or unsuitable equipment can indicate an opportunity to redeploy resources, while a shortage of suitable equipment may affect recruitment, expansion or site changes. These conclusions should be based on reliable records and operational evidence rather than assumptions.
Report risk in terms of exposure and treatment. Technical risk should be described in a way that makes its business significance clear. Useful examples include:
- equipment that is no longer supported or cannot receive required updates;
- assets with unresolved security configuration issues;
- devices whose ownership, location or user cannot be verified;
- important systems with inadequate resilience or an unrecorded dependency;
- equipment approaching a known replacement or warranty deadline; and
- gaps between the organisation’s policy requirements and the assets currently recorded.
For each risk, the report should record its likelihood or severity using the organisation’s established method, the affected business area, the proposed treatment and the date by which a decision is needed. It should avoid presenting a long unranked list, since senior leaders need to distinguish urgent exposure from lower-priority housekeeping.
Include compliance and audit evidence. Leaders may need assurance that the organisation can account for its technology and demonstrate appropriate control. A useful report can identify missing records, incomplete ownership information, unapproved assets, gaps in disposal evidence and exceptions to internal policy. It should link conclusions to available evidence, such as approval records, assignment information, disposal documentation or review results, without claiming compliance solely because an asset appears in the register.
Show lifecycle decisions and dependencies. Asset reporting should make it possible to plan beyond the immediate issue. A lifecycle view can group assets into stages such as planned, deployed, under review, due for replacement, retained as a spare or awaiting disposal. It should identify dependencies that may affect timing, including procurement, user migration, application compatibility, data handling, site work or wider infrastructure changes.
Measure data quality as well as asset status. Leaders need to know how much confidence to place in the report. The service should identify records with missing serial numbers, unclear ownership, conflicting locations, outdated assignments or assets that have not been reconciled with other available records. Data-quality exceptions should have an owner and corrective action, because poor records can lead to incorrect budgets, weak audit evidence and poorly timed replacements.
Use consistent reporting and clear follow-up. Reports are most valuable when their structure, definitions and status labels remain consistent over time. Each edition should show previous actions, completed work, outstanding decisions and newly identified issues. Trend information can then reveal whether the organisation is reducing its backlog, improving record accuracy, controlling lifecycle exposure or accumulating unresolved exceptions.
The final report should separate facts, interpretation and recommendations. It should include enough detail for technical teams to validate the findings, but present the main conclusions in plain business language. In practice, the strongest report is not the longest one; it is the one that enables leaders to approve, defer, investigate or assign a decision with a clear understanding of the evidence and consequences.
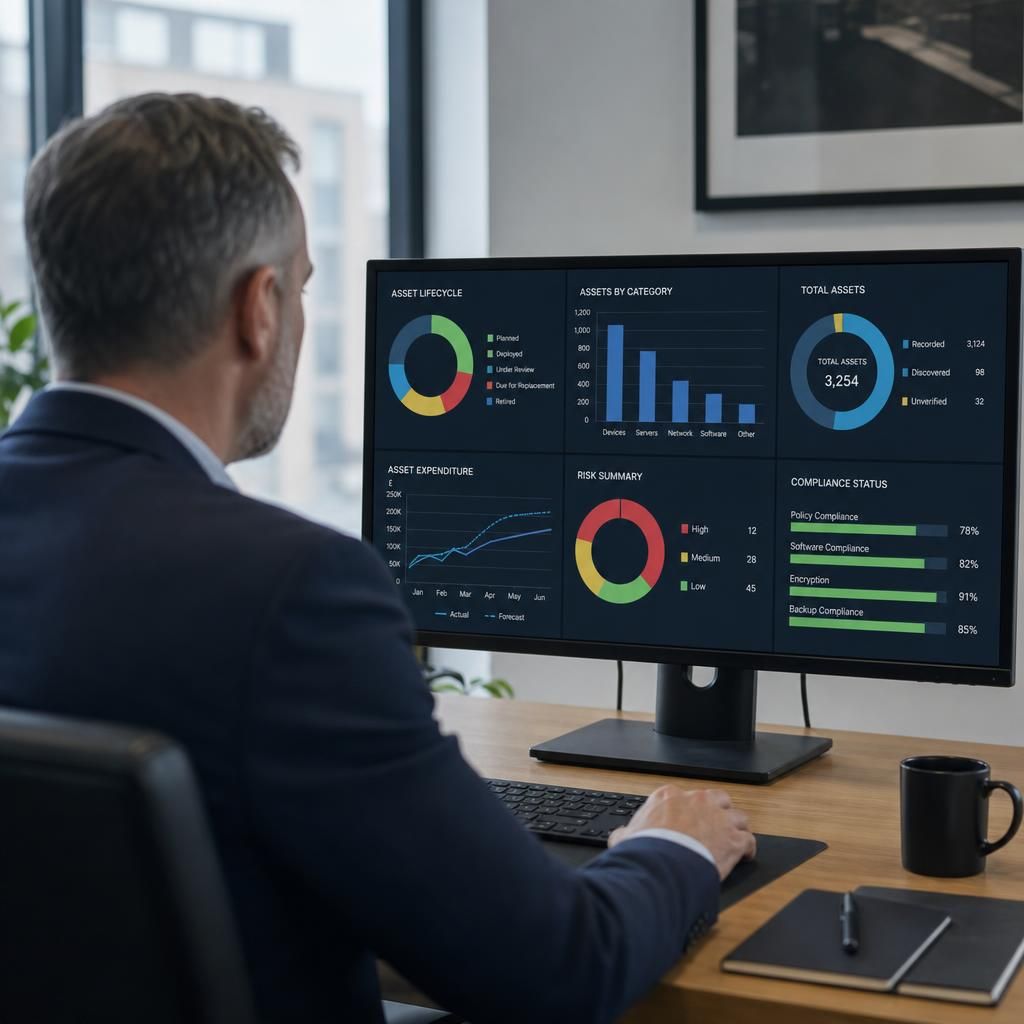
Business leaders should see clearly defined measures rather than unexplained figures. Every metric in an IT asset management report should state what is being counted, which assets or locations are included, the reporting period and any known limitations in the underlying data.
- Scope: distinguish the full asset population from assets currently recorded, discovered or verified.
- Meaning: explain whether a figure represents a count, a rate, a cost, a forecast or an exception total.
- Context: compare results with the previous reporting period or an agreed threshold where that comparison is valid.
- Interpretation: identify whether a change reflects a genuine business trend, a data reconciliation exercise or a change in reporting criteria.
This prevents a dashboard from giving a misleading impression through isolated numbers. A falling exception count, for example, may indicate improved control, fewer assets being assessed or incomplete data. Brief definitions and explanatory notes allow leaders to interpret the report correctly before approving action.