
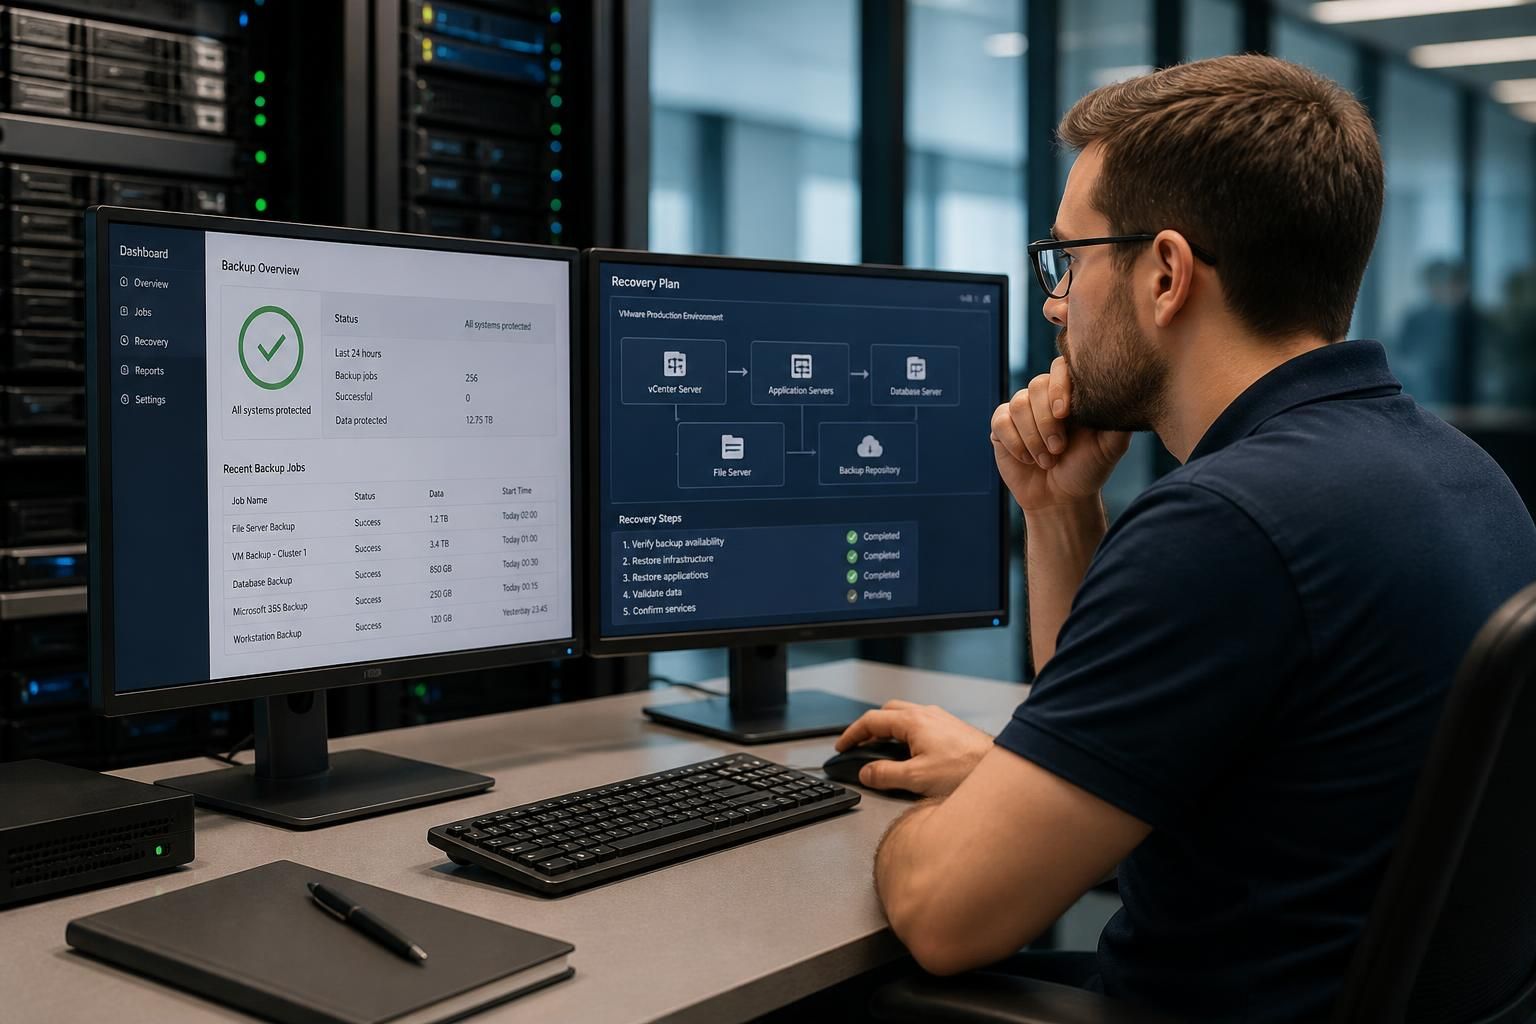
How often should managed backup recovery tests be performed?
Managed backup recovery tests should be performed at least annually, with more frequent testing for critical systems or data. Tests should also be repeated after significant infrastructure, application or backup-policy changes to confirm that recovery procedures, restore points and dependencies still work as expected.
Managed backup recovery tests should follow a documented, risk-based schedule rather than relying on successful backup notifications. The appropriate interval depends on how quickly the organisation must recover, how much data changes, the complexity of the systems involved, and the consequences of an unsuccessful restore.
A completed backup job confirms that data was copied to the backup destination; it does not prove that the data can be restored into a usable system. Recovery testing should therefore check the complete process, including access to the backup repository, decryption keys, restore permissions, system dependencies and the ability of staff to follow the documented procedure.
A practical testing programme normally combines several types of test:
- File-level restores: Select individual files from different backup dates and confirm that they open correctly and retain their expected contents.
- Application restores: Recover business-critical applications and their associated databases, then verify that records, configurations and integrations work together.
- System-level restores: Rebuild a server, workstation or virtual machine to establish whether the organisation can recover an operational environment rather than isolated data.
- Scenario-based exercises: Work through a realistic incident, such as ransomware, hardware failure or accidental deletion, including the decisions and responsibilities that arise during recovery.
- Alternative-location recovery: Where the recovery design depends on separate infrastructure or a different location, test that environment and confirm that required network, identity and security services are available.
Tests should not always use the same file or recovery point. Rotating the data selected for testing helps identify problems affecting particular systems, dates or backup sets. The sample should include data with different retention periods and any systems that have unusual dependencies or specialised recovery requirements.
Each test needs clear pass criteria. These may include whether the restored data is complete, whether applications start correctly, whether users can authenticate, whether permissions are preserved and whether the recovery process meets the organisation’s documented recovery objectives. A technically successful restore may still be unacceptable if it leaves a key service unusable or exposes data to the wrong users.
Testing should produce an auditable record containing the date, systems and recovery points tested, the people involved, the duration, any errors found and the corrective actions assigned. Failed tests should result in a tracked improvement rather than simply being marked as complete. Repeating the test after remediation confirms that the underlying issue has actually been resolved.
The schedule should be reviewed whenever the organisation’s risk profile changes. New applications, altered dependencies, increased data volumes, revised retention rules and changes to recovery objectives can all make an existing test plan inadequate. It is also sensible to vary the scope over time so that both routine restores and complete disaster-recovery procedures receive attention.
A managed backup service can help maintain the test calendar, select appropriate recovery scenarios, document results and escalate weaknesses for review. S2 Technology Group can advise businesses around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas on how recovery testing fits within a wider managed backup and IT continuity process.
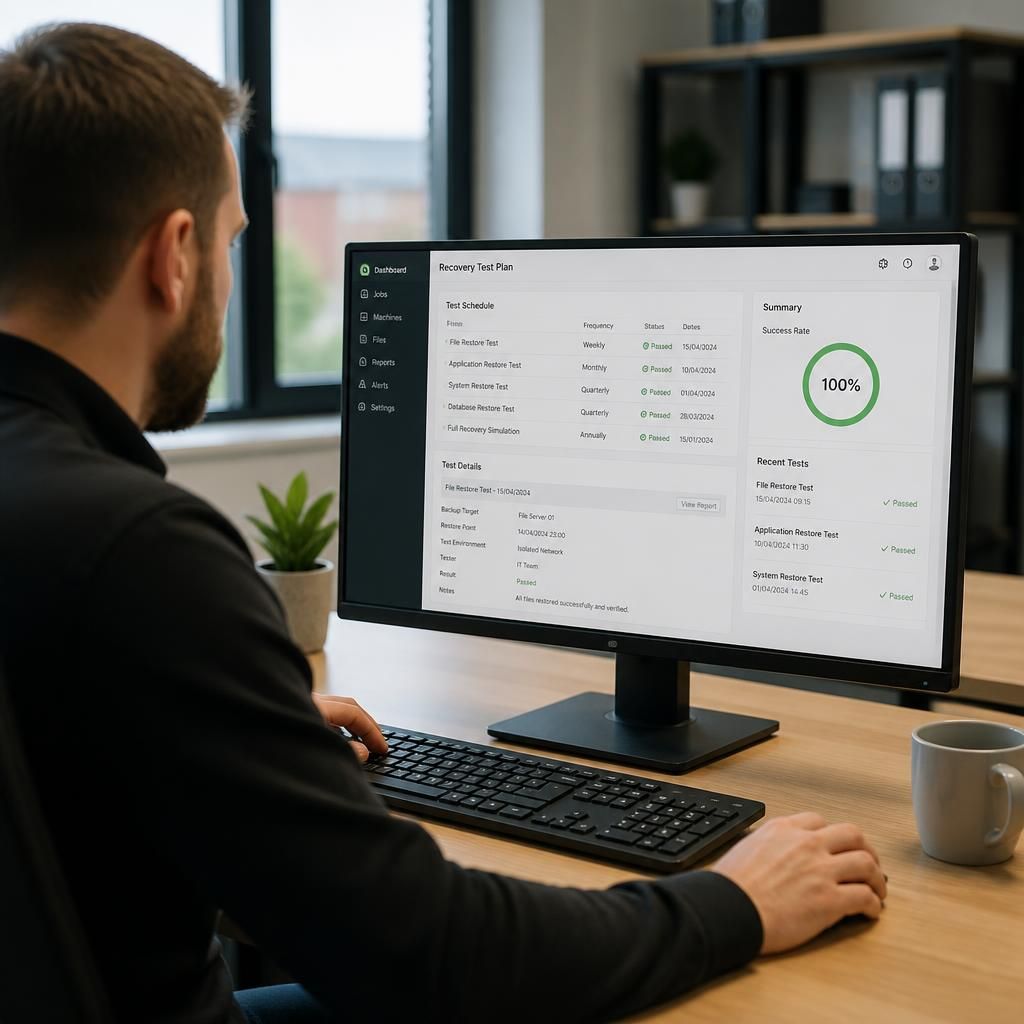
Managed backup recovery tests should be carried out in a controlled environment wherever possible, rather than restoring test data directly over live systems. This allows the organisation to verify that files, applications and configurations are usable without risking production data or disrupting business operations.
The test environment should be separated from the operational network and protected with appropriate access controls. Use temporary credentials where practical, restrict access to sensitive restored data and check restored files for signs of corruption or malicious content before they are connected to live services. Once the exercise is complete, remove temporary data, accounts and access permissions so the recovery test does not create a new security or data-protection risk.
This approach makes the result more reliable: it tests whether the organisation can recover usable data while also confirming that the recovery process itself is safe to operate.