Where is offsite backup data physically stored?
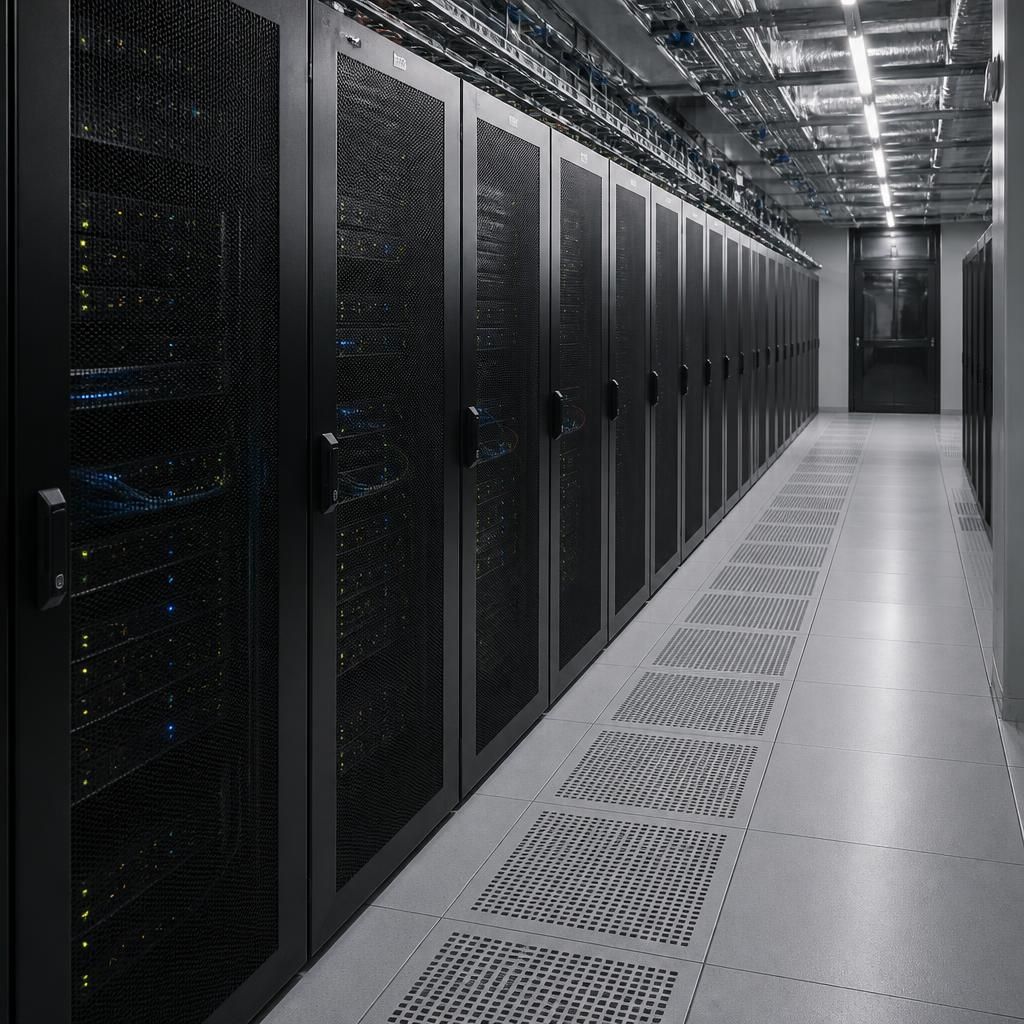
Offsite backup data is physically stored in secure data centres separate from the organisation’s primary premises, with the exact location depending on the backup provider and service agreement. Businesses should confirm the data-centre locations, applicable jurisdiction, resilience arrangements and encryption controls before selecting a solution.
Offsite backup data is usually held on storage systems within professionally managed data centres, rather than on equipment at the organisation’s main premises. Depending on the service design, the protected data may exist in one or more facilities, on dedicated hardware, shared infrastructure or cloud storage. The physical arrangement should be documented in the backup service agreement and examined alongside the organisation’s recovery, security and data protection requirements.
A typical offsite backup arrangement can include several physical components:
- Backup storage: the main repository containing backup files, snapshots or backup images.
- Replication storage: a second repository to which backup data is copied for additional resilience.
- Temporary processing systems: infrastructure used to verify, index, deduplicate or restore data.
- Local cache or staging storage: equipment at the business premises or in a nearby facility that holds recent backup data before it is transferred elsewhere.
These components do not always sit in the same building. A provider may store a primary copy in one data centre and replicate it to another facility in a different location. However, “offsite” does not automatically mean that copies are in different regions or countries. Two facilities can be geographically separate but still exposed to the same power network, flood zone, telecommunications failure or other local incident. The relevant question is therefore not just whether the data has left the office, but whether the storage locations provide meaningful separation from the risks being managed.
The physical location also determines which legal and contractual frameworks may apply. Data held in the UK is subject to a different jurisdictional context from data transferred to another country. Organisations should establish where the production copy, replicated copy, temporary restore data and system metadata are held. Metadata can include file names, user identities, device details and retention information, so it should not be overlooked when assessing data residency.
Physical storage location is only one part of the security model. Data should be encrypted while it is transferred to the backup repository and while it is stored there. Access to the underlying systems should be restricted, authenticated and logged. Data-centre controls may include controlled entry, visitor procedures, surveillance, fire detection, environmental monitoring, power redundancy and resilient network connections. These controls reduce the risk of physical damage or unauthorised access, but they do not replace sound backup configuration and access management.
Businesses should also distinguish between the location of the storage hardware and the location of the people or systems that can administer it. A backup may be physically stored in the UK while administrative access is provided from another country. The service documentation should explain where support and privileged administration take place, how access is authorised, and whether the provider uses subcontractors or additional hosting platforms.
Before approving an offsite backup service, ask the provider to confirm:
- the country or region in which each backup copy is stored;
- whether copies are held in separate facilities and whether those facilities have independent infrastructure;
- the location of restore, staging and temporary processing systems;
- how data transfers between sites are protected;
- which jurisdiction governs the stored data and the service contract;
- how long deleted or expired backup data remains on physical media;
- how storage media are sanitised or destroyed when equipment is retired; and
- which parties can access the infrastructure and under what approval process.
Some providers use removable media or vaulting as part of an offsite strategy. In that model, backup media are transported to a controlled storage facility rather than remaining on continuously connected systems. This can reduce exposure to certain online attacks, but the organisation should still verify chain-of-custody procedures, environmental protection, encryption and how quickly the media can be retrieved for restoration.
For a small or medium-sized organisation, the practical assessment is whether the storage design matches the consequences of data loss. A business handling sensitive client information may require UK-only storage, documented retention controls and clear evidence of access restrictions. A multi-site organisation may place greater emphasis on independent locations and network routes. S2 Technology Group can help businesses around Stourbridge, Kinver, Wordsley, Kingswinford, Kidderminster, Halesowen, Dudley and neighbouring areas assess these requirements as part of a wider managed backup and IT strategy.
The written service specification should state the physical storage locations or permitted regions, the number and separation of copies, the applicable data-handling terms and the controls used to protect them. Without that information, “offsite backup” describes a broad arrangement rather than proving where the data is held or how well the storage withstands a site-level incident.
Offsite backup data is often stored as encrypted data blocks across a storage cluster, rather than as one complete file on a single server. The backup platform may use replication or erasure coding so that the information remains available if an individual disk or storage node fails. This means the relevant question is usually which data-centre region and facilities contain the storage cluster, not which specific server holds a particular file.
Organisations should check whether the provider keeps these data fragments within the agreed country or region, including any secondary storage used for resilience. It is also useful to confirm whether deduplication or compression changes where data is processed, and whether restore operations temporarily reconstruct files on separate infrastructure. These details help establish whether the physical storage design matches internal data-residency and recovery requirements.