
How should a firewall inspect encrypted traffic without weakening network security?
A firewall can inspect encrypted traffic by terminating the TLS session at a controlled inspection point, analysing the decrypted content for threats, and establishing a separate, securely validated connection to the destination. Security is preserved through strict certificate validation, protected inspection keys, least-privilege access, encrypted logging, and carefully defined exclusions for sensitive traffic such as banking or healthcare sessions.
Encrypted traffic inspection is secure when it is treated as a controlled security process rather than as unrestricted decryption. The firewall should inspect only traffic that has a defined security purpose, preserve the identity and integrity of the original connection, restrict access to inspection functions, and fail in a controlled way if inspection cannot be performed.
How the inspection path works
For outbound web traffic, the firewall commonly operates as an intermediary between the internal client and the external service. It presents the client with an inspection certificate, examines the permitted content, applies security controls, and then creates the external session. The client must trust the organisation’s inspection certificate through managed device configuration; otherwise, browsers and applications should report that the connection cannot be verified.
This arrangement creates two cryptographic sessions rather than allowing the firewall to read a stream invisibly. The inspection device must validate the remote service, apply the organisation’s certificate policy, and maintain a clear relationship between the internal request and the external connection. Administrative records should identify which policy handled the traffic without storing sensitive payloads unnecessarily.
Inbound inspection follows a different design. Where a business publishes an application, encrypted sessions can be inspected at a gateway before permitted requests are passed to the application environment. The gateway must protect the original client information, apply the same security policy to every relevant access path, and avoid becoming a single point of failure through which unvalidated traffic is allowed to pass.
Use the narrowest practical inspection scope
Decrypting every connection is not automatically the most secure choice. Inspection policy should be based on risk, application behaviour and the sensitivity of the data involved. Web browsing, file transfers and unknown or newly categorised destinations may justify deeper examination, while highly sensitive services may require a different control or a documented exclusion.
Policy should define which users, networks, destinations, protocols and applications are included. It should also state what happens when traffic cannot be categorised, when a service uses an unsupported protocol, or when an application rejects interception. A broad default rule with informal exceptions is difficult to review and can create both privacy and security gaps.
Protect the inspection infrastructure
The inspection function is a high-value security component because it can process confidential content and influence the connections that users trust. It should therefore be isolated from ordinary administration, protected by strong administrative authentication, and limited to authorised personnel. Configuration changes should be attributable to an individual account and subject to review.
Inspection certificates and related private material should be stored in protected systems with controlled export. Copies should not be placed in general file shares, scripts or unmanaged devices. There should be a documented process for certificate renewal, revocation and replacement, including removal of old trust settings from managed endpoints.
The firewall itself should be kept on a supported software version and monitored for capacity. Encrypted inspection consumes more processing resources than simply allowing encrypted sessions through. Resource pressure can cause dropped connections, delays, inconsistent policy enforcement or an unsafe decision to bypass inspection. Capacity planning should consider peak concurrent sessions, connection establishment rates, traffic types and future growth rather than relying only on average throughput.
Preserve privacy and data governance
Inspection can expose credentials, personal information, commercial documents and communications that would otherwise remain encrypted in transit. A business should document the purpose of inspection, identify who may access inspection results, and retain only the information needed for security operations. Payload capture should be disabled or tightly controlled unless there is a specific, justified requirement.
Users should be informed through appropriate policies, particularly where monitoring may involve personal use or regulated information. Access to security records should be reviewed, and exported material should be protected during storage and transfer. The inspection policy should also account for data protection obligations and contractual restrictions affecting client, employee or supplier information.
Handle applications that do not tolerate interception
Some applications use certificate pinning, mutual authentication, custom encryption or encrypted protocols that do not behave like ordinary web traffic. Attempting to force these sessions through generic inspection can break the application or encourage unsafe workarounds. The correct response may be a narrowly defined bypass combined with other controls, such as endpoint protection, application allow-listing, destination restrictions and anomaly monitoring.
Modern protocols can also change how traffic is carried. For example, applications may use encrypted UDP-based transport rather than conventional web sessions. If the firewall cannot apply its intended controls to that traffic, the policy should explicitly decide whether to block it, permit it under a reduced inspection model, or route it through a supported inspection method. Silent fallback is difficult to govern.
Define safe failure behaviour
A secure design specifies what happens when the inspection service is unavailable, a certificate cannot be validated, a policy service cannot be reached, or the firewall runs out of inspection capacity. For high-risk destinations, allowing traffic to continue without the required checks may be inappropriate. For essential business applications, a controlled alternative may be necessary to avoid operational disruption.
These decisions should be made per traffic class rather than through one global fail-open or fail-closed setting. The resulting rules need testing with representative applications, including software updates, cloud services, voice and video traffic, remote access tools and business-critical systems.
Test for security and usability
Testing should confirm that the firewall detects malicious content and policy violations without altering legitimate files, breaking authentication or generating misleading alerts. Test cases should cover different user groups, device types, network paths and application categories. Administrators should verify that excluded traffic is genuinely excluded, included traffic is genuinely inspected, and policy changes take effect only where intended.
Performance testing should measure connection establishment, user-facing latency, resource consumption and error rates under realistic load. Security testing should check for routes that avoid inspection, such as alternative gateways, unauthorised DNS services, unsupported protocols or unmanaged devices. Results should be recorded so that later changes can be compared against an established baseline.
Encrypted traffic inspection strengthens a network when it is selective, technically controlled and regularly reviewed. It weakens security when it becomes a blanket decryption mechanism with excessive access, poor certificate management, unprotected records or untested bypasses. A documented inspection policy, supported by endpoint configuration, firewall monitoring and periodic technical review, provides a more defensible balance between threat detection, privacy and reliable business connectivity.
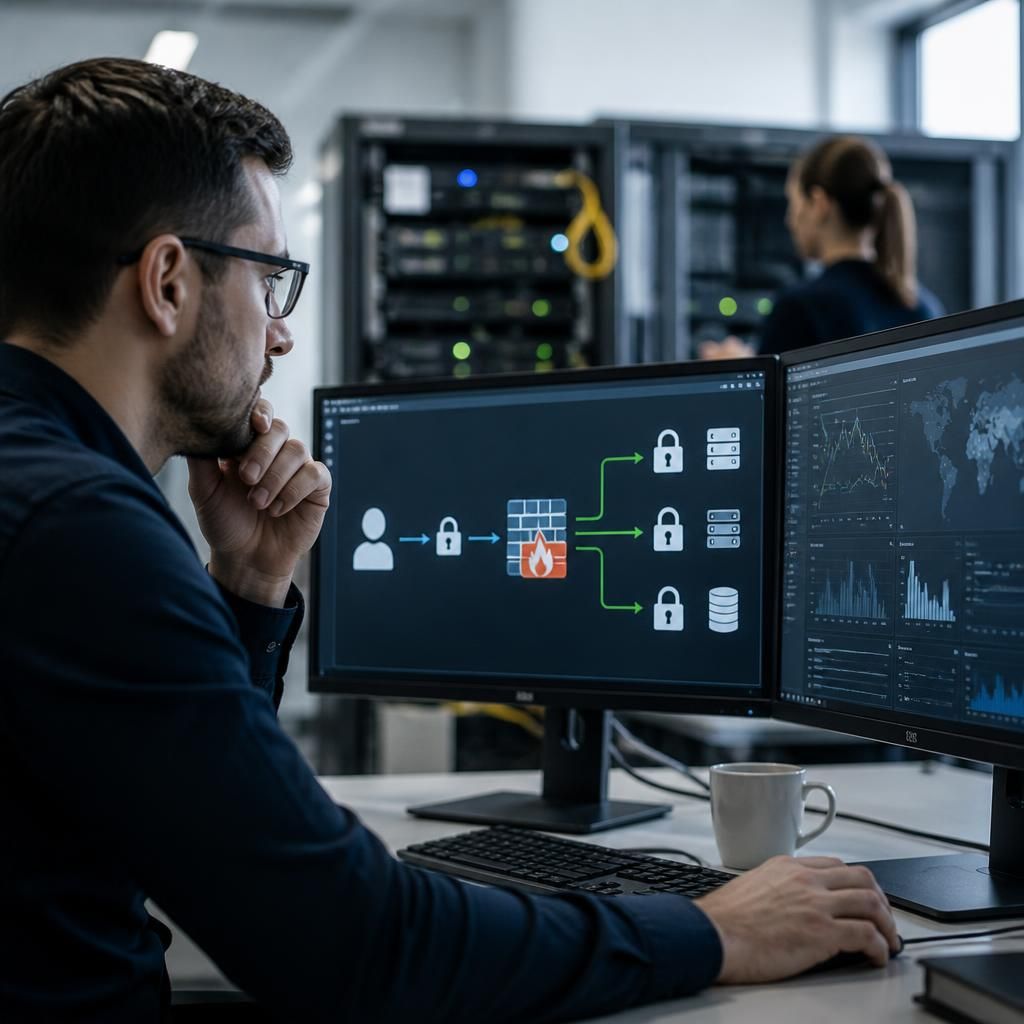
Mutual TLS requires special handling because both the user’s device and the server authenticate themselves with certificates. A conventional firewall proxy cannot simply decrypt and recreate this session: the client’s private key should remain under the control of the authorised device or application, not be copied to the inspection system.
Where mutual TLS is essential, the security design may need a supported pass-through method, endpoint-based inspection or a deliberately engineered gateway that preserves certificate identity. Any exception should identify the affected application, define the alternative controls applied to it, and be tested after certificate renewal or application changes. This prevents encrypted traffic inspection from weakening the authentication that the application relies on.