How is Microsoft 365 backup tested before a real recovery is needed?
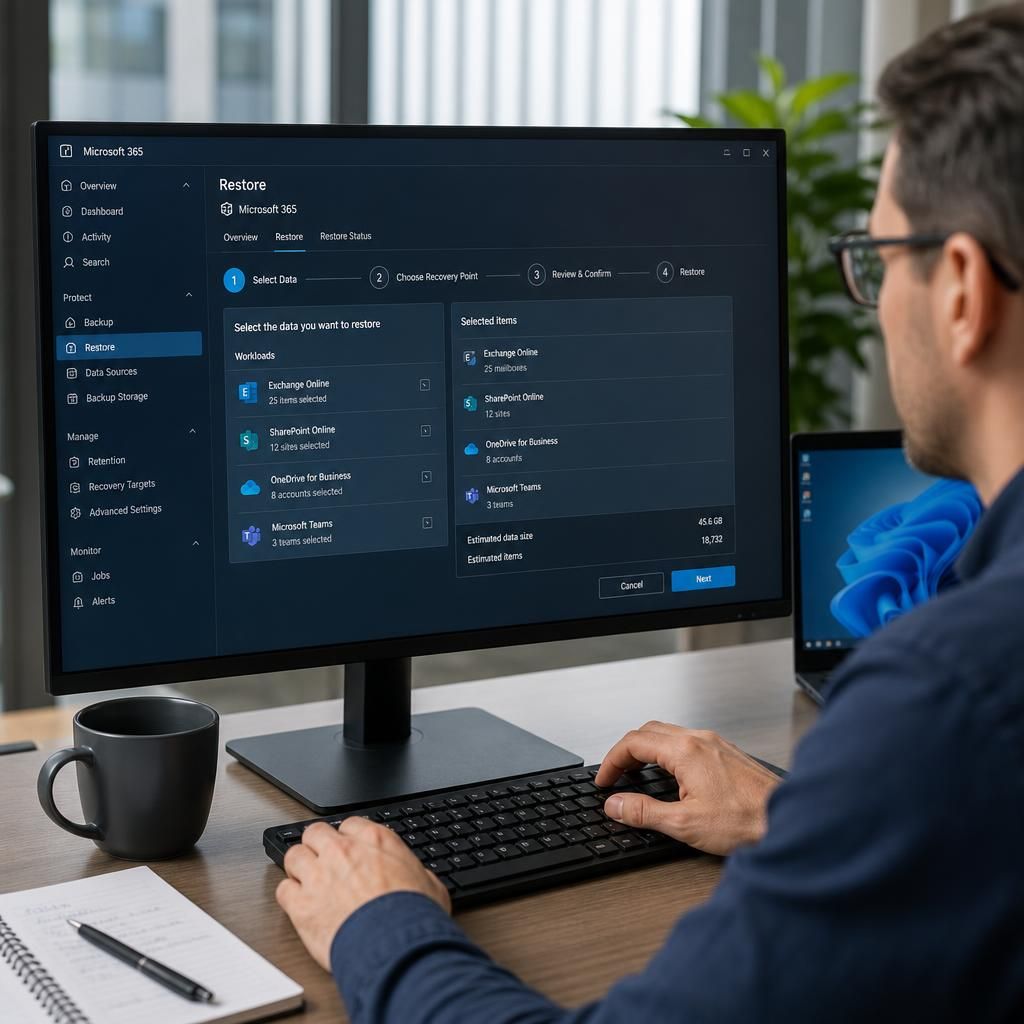
Microsoft 365 backup is tested through controlled recovery exercises that confirm data can be restored accurately, with the right permissions and usable versions. Testing should cover representative files, emails, SharePoint content and other protected data, while recording the outcome and resolving any failures before a real incident occurs.
Microsoft 365 backup is tested by carrying out planned, documented recovery exercises in a controlled environment, rather than assuming that a completed backup job can automatically be restored. The test checks whether selected data can be located, recovered to an appropriate destination and used correctly without altering live information.
A reliable test begins with a written recovery plan. This should identify the data being tested, its original location, the required recovery point, the people authorised to approve the exercise and the evidence that must be collected. The plan should reflect realistic business scenarios, such as an accidentally deleted document, a damaged mailbox, a missing SharePoint folder or the need to recover information from an earlier point in time.
The recovery is normally performed away from the live content where possible. Restoring into a separate location, test account or isolated site reduces the risk of overwriting current information and allows the recovered material to be inspected safely. Access to that test area should be limited to authorised personnel, particularly where the data contains personal, financial or commercially sensitive information.
Testing should examine more than whether files appear after a restore. Useful checks include:
- Whether the intended backup point can be found and selected.
- Whether the restored content opens correctly and is complete.
- Whether folder structures, file names, versions and relevant metadata remain usable.
- Whether mailbox folders, messages and attachments are present where expected.
- Whether SharePoint libraries, documents and permissions behave as intended.
- Whether restored users, groups or access rights match the recovery requirement without granting excessive access.
- Whether the recovered data can be returned to its operational location safely if that is required.
Different recovery methods should be tested separately. An individual-item recovery confirms that a single email, document or folder can be found without restoring an entire workload. A larger recovery exercise tests how the process performs when a substantial volume of information or several related locations are involved. Point-in-time testing is also important because the newest available copy may not be suitable if unwanted changes or malicious activity have already been included in it.
Validation should include the people who use the recovered information, not only the person operating the backup console. For example, a mailbox owner can confirm that messages and attachments are understandable, while a SharePoint administrator can check that documents, version history and site structure support normal work. Technical completion and practical usability are separate tests.
The process should also verify the surrounding controls. The tester should confirm that the correct administrator permissions are available, that authentication requirements do not prevent recovery, and that audit records identify who performed each action. If recovery depends on a separate destination, account or storage location, those dependencies should be checked before an incident makes them difficult to resolve.
Every exercise should produce a record showing the backup point used, the data selected, the destination, the checks completed, any limitations and the corrective action assigned. A failed or incomplete test is useful evidence: it may reveal missing permissions, unsuitable retention settings, unclear responsibilities, an inaccessible destination or data that cannot be recovered in the required form. The issue should be corrected and the relevant part of the exercise repeated, rather than simply marked as an exception.
Testing is most meaningful when it is repeated according to the organisation’s risk and recovery requirements, and when it is revisited after significant changes to Microsoft 365, backup configuration, permissions or business processes. Regular evidence-based testing gives an organisation a more reliable understanding of what its backup service can recover and what further preparation is needed before a genuine data loss event.
A Microsoft 365 backup test should measure how the recovery process performs against the organisation’s recovery objectives, not only whether the data is technically restored. Record the time required to identify the correct recovery point, authorise the operation, recover the data and make it available to the people who need it. This helps compare the tested process with the business’s recovery time objective without relying on assumptions.
The exercise should also identify practical constraints, such as administrator workload, destination capacity, network or authentication dependencies and the order in which workloads must be recovered. Testing a prioritised sequence—for example, critical mailboxes before less essential content—shows whether the organisation can restore the most important services first. Any delay, manual step or dependency that affects this sequence should be documented and addressed before the recovery plan is relied upon.