
How is Microsoft 365 Backup tested before a real recovery is needed?
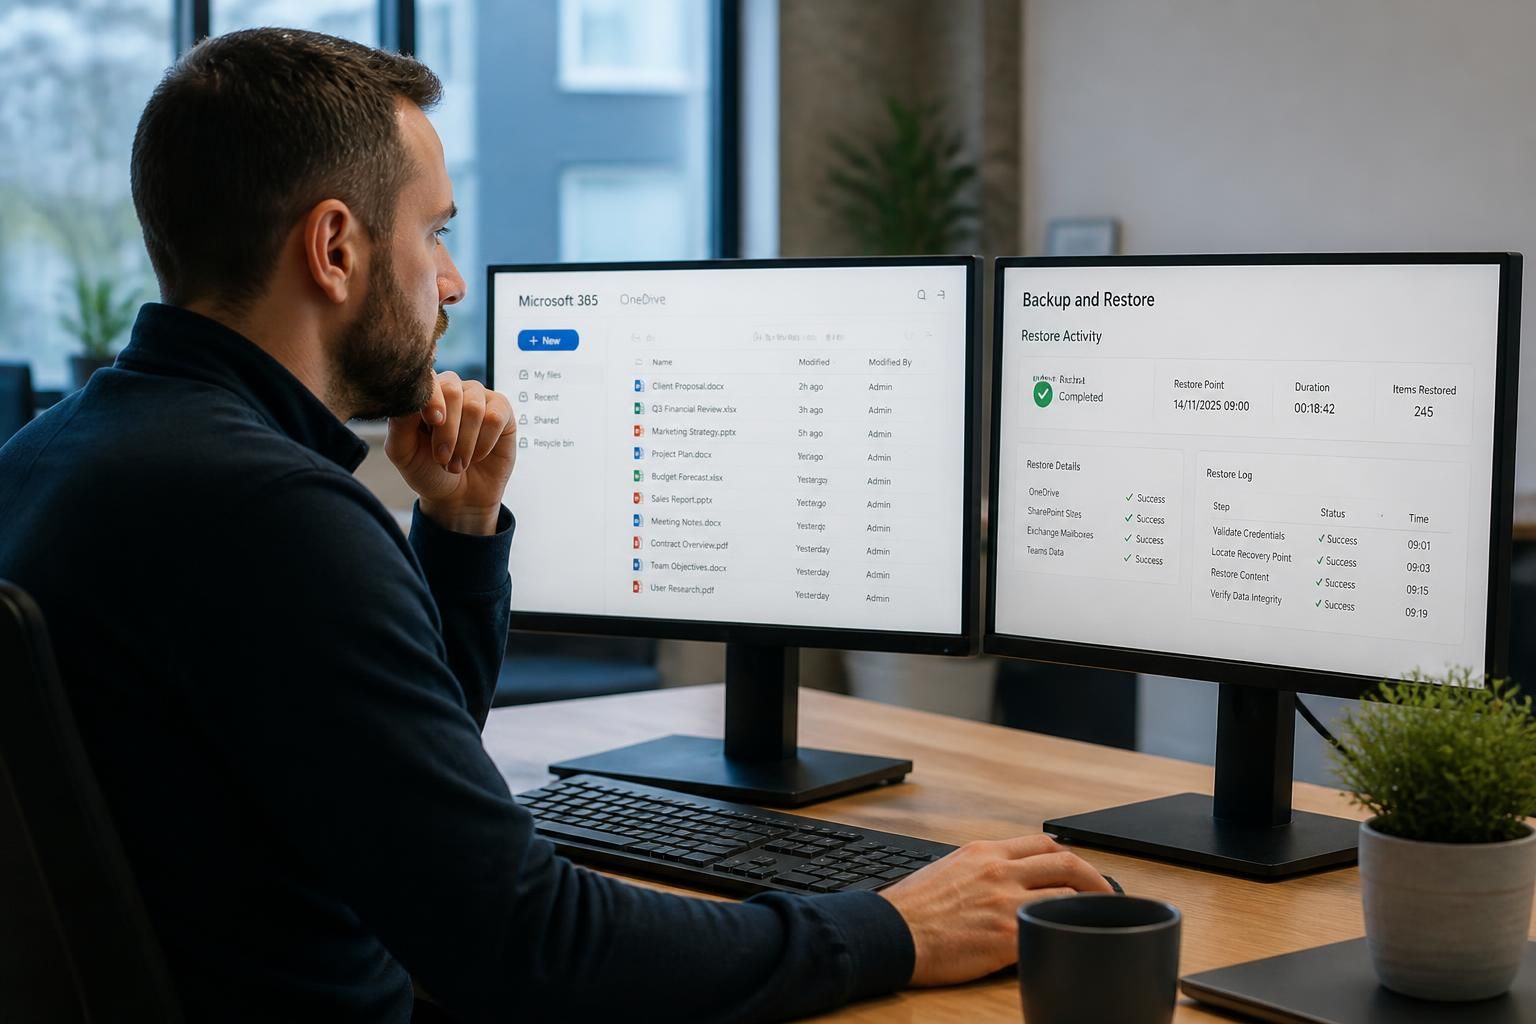
Microsoft 365 Backup is tested through planned recovery drills that restore selected data into a controlled test environment without affecting live users or the production tenant. Each drill checks that the restored content is complete, usable and correctly dated, with the results documented and any issues addressed before a real recovery is needed.
Microsoft 365 Backup should be tested through a documented programme that combines backup-health checks, controlled restoration exercises and evidence-based review. Testing should confirm not only that recovery can be started, but also that the correct recovery point, content, structure, permissions and business context are preserved.
A useful test programme begins by defining recovery scenarios that reflect the organisation’s actual risks. These may include accidental deletion, corruption, a compromised account, a ransomware incident or the loss of selected content from a particular user or team. Each scenario should identify what needs to be recovered, who is authorised to request it, which recovery point is appropriate and how the restored information will be assessed.
- Backup coverage: confirm that the intended users, groups, sites, mailboxes and other protected data sources are included in the backup scope.
- Recovery-point selection: verify that administrators can identify a suitable point before the suspected deletion, corruption or compromise.
- Content integrity: compare restored files, messages, folders and relevant metadata with the original source where appropriate.
- Permissions and ownership: check that access rights, sharing arrangements and ownership information are either preserved correctly or deliberately reconfigured for the recovery scenario.
- Usability: confirm that recovered content can be opened, searched, downloaded or returned to its intended working location without introducing avoidable access or compatibility problems.
- Audit evidence: record who performed the test, what was selected, which recovery point was used, what was recovered and whether any exceptions were found.
Tests should use representative samples rather than only trivial files. A sample might include documents with nested folders, commonly used file types, messages with attachments, calendar information and data owned or shared by different users. The exact sample should reflect the organisation’s Microsoft 365 configuration and the information it considers important.
Testing should also examine the administrative process around recovery. The person carrying out the exercise should verify that permissions allow the operation without granting broader access than necessary. The test should confirm that the recovered data is placed in an appropriate location, remains separated from live working data during validation and is removed or secured afterwards in line with the organisation’s information-handling rules.
Automated status information is useful, but it is not a substitute for restoration testing. A system may report that backup operations are completing while a recovery issue remains undiscovered, such as an unexpected folder structure, missing metadata, unsuitable permissions or difficulty locating the required point in time. Manual checks expose these practical problems before they affect a real incident.
Each exercise should end with a review of the evidence. Any missing content, access failure, unclear responsibility or procedural weakness should be recorded as a corrective action. The backup configuration, recovery instructions and permissions should then be updated where necessary, followed by a further test of the affected area. Keeping these records provides an auditable history and helps demonstrate that recovery arrangements are being actively maintained rather than assumed to work.
Testing should be repeated when there is a material change to the Microsoft 365 environment, backup configuration, retention policy, administrator permissions or recovery procedure. It is also sensible to revisit the test scenarios when the organisation introduces new workloads, changes its data ownership model or identifies a new threat. This keeps the recovery process aligned with the data the business actually relies on.
S2 Technology Group can help small and medium-sized organisations assess their Microsoft 365 backup arrangements, define practical recovery scenarios and review the technical and administrative results. The objective is to give the organisation documented evidence that its backup can support an informed recovery decision when it is needed.
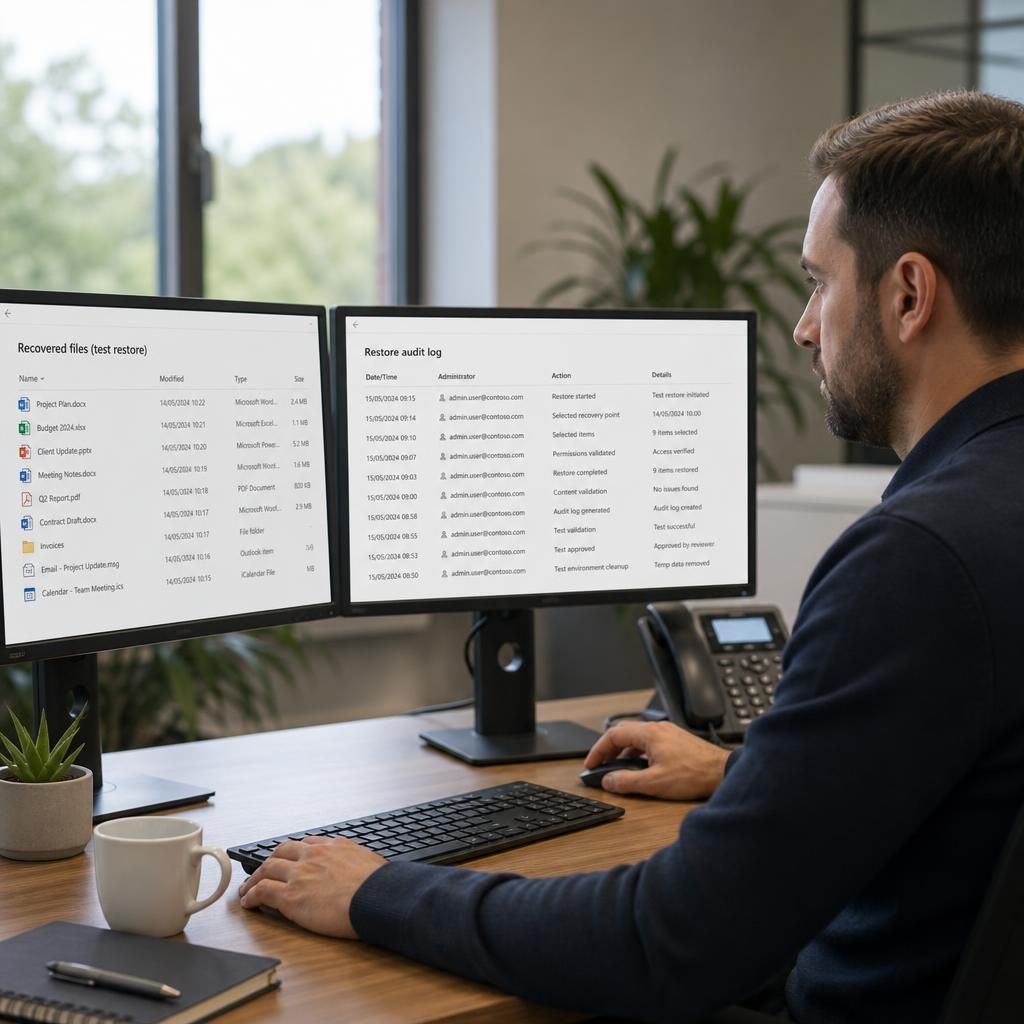
Microsoft 365 Backup testing should also verify that the recovery procedure can be followed consistently by an appropriately authorised administrator, rather than relying on the person who originally configured it. A reviewer can work through the documented instructions using a test scenario, confirming that the required access, recovery steps, approval points and validation checks are clear.
This type of exercise can reveal practical weaknesses that a technical restore alone may not show, such as undocumented dependencies, unclear terminology, missing escalation instructions or uncertainty about when recovered data is ready for business use. The procedure should be updated where necessary so that recovery remains repeatable and does not depend on individual knowledge.