Is the IT security consultant independent of specific technology vendors?
An IT security consultant is independent of specific technology vendors when recommendations are based on your organisation’s security requirements, risks and existing environment rather than a preferred supplier’s products. To assess independence, ask whether the consultant compares suitable options, explains limitations and discloses any commercial relationships with vendors.
Yes, an IT security consultant can be independent of specific technology vendors, but independence is demonstrated through the way advice is produced rather than simply claimed. An independent consultant begins with your risks, obligations, business processes and existing systems, then evaluates suitable approaches against defined requirements. The recommendation should remain defensible even if the consultant has no commercial relationship with the supplier selected.
Vendor independence does not mean avoiding all commercial technology. Most security controls require software, hardware or cloud services from a supplier. The important distinction is whether the consultant is selecting technology because it fits the documented need, or steering the business towards a product that supports the consultant’s commercial interests, preferred technical habits or existing partnership arrangements.
A sound assessment of independence should examine several areas:
- Commercial relationships: ask whether the consultant receives referral fees, reseller margins, commission, rebates or other benefits from recommended suppliers. These arrangements are not automatically inappropriate, but they should be disclosed before recommendations are made.
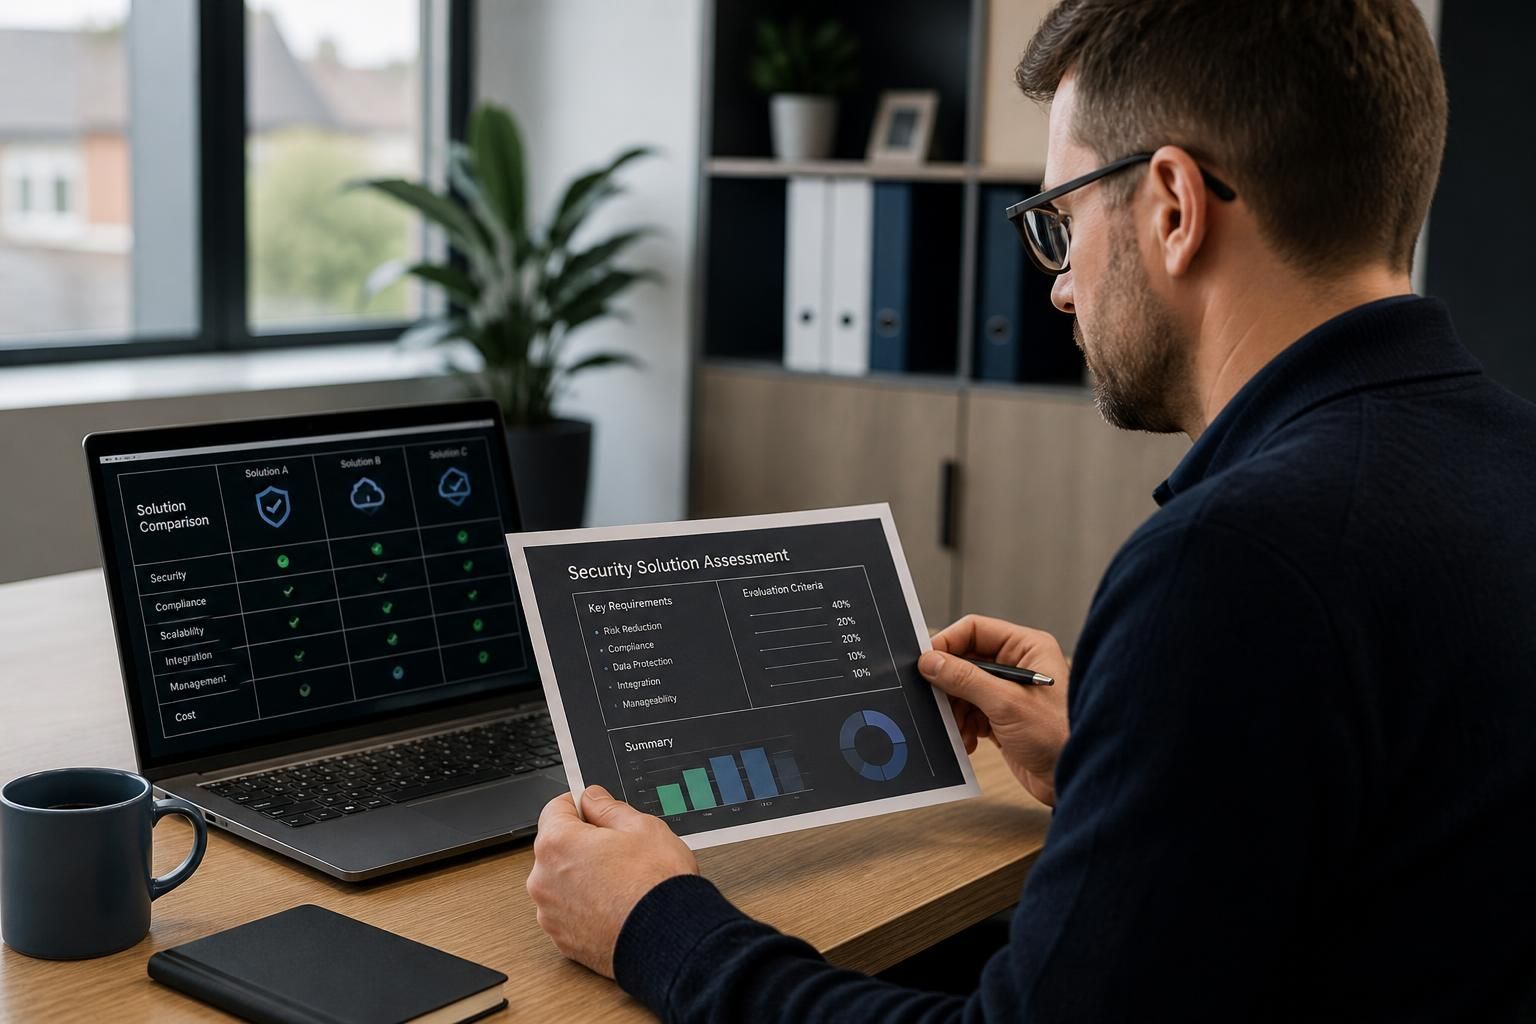
- Selection criteria: check that proposed solutions are measured against requirements such as risk reduction, compatibility, manageability, data handling, resilience and total cost of ownership.
- Alternatives: expect the consultant to explain which reasonable options were considered and why they were rejected. A recommendation that presents only one unexplained product is harder to evaluate objectively.
- Evidence: ask for the assumptions, findings and technical reasoning behind the advice. This makes it possible to distinguish a risk-based recommendation from a sales proposal.
- Ownership of decisions: the business should retain control over the final choice, with a clear explanation of the consequences of selecting or rejecting each option.
Independence is particularly important where a recommendation could create long-term dependency. Security platforms may involve recurring licences, proprietary data formats, specialist administration skills or integrations with other systems. A consultant should explain the practical effect of adopting a solution, including how data can be exported, how the service could be replaced, what migration would involve and whether the organisation would need additional expertise to operate it.
However, avoiding vendor lock-in should not become the only objective. A technically open solution may be harder to manage, poorly integrated with the organisation’s current environment or unsuitable for its risk profile. Conversely, standardising on a well-integrated platform may be sensible if the operational advantages are clear. Independent advice weighs these trade-offs instead of treating a particular procurement model as automatically correct.
The review should also separate product capability from implementation quality. A tool may offer strong security features but still fail to reduce risk if it is incorrectly configured, poorly monitored or not incorporated into incident procedures. The consultant should therefore consider how controls will be deployed, maintained, tested and reviewed, as well as whether the internal team has the skills and capacity to manage them.
Before appointing a consultant, a business can request a written statement covering:
- current supplier partnerships, referral arrangements and resale activities;
- how conflicts of interest are identified and managed;
- the method used to compare products or service models;
- whether recommendations are limited to the consultant’s supported technologies;
- who owns the assessment, designs and other work produced; and
- how advice will remain objective if the consultant is later asked to supply or manage the recommended solution.
It is also useful to ask for recommendations in two stages. The first should describe the required security outcomes, control priorities and technical capabilities without naming a product. The second can map those requirements to suitable solutions. This structure makes it easier to see whether the technology follows the need, rather than the need being adapted to fit a predetermined product.
An independent IT security consultancy may still recommend a technology from an established partner or work with a business to implement the selected solution. Independence is not incompatible with practical delivery. The essential safeguards are transparent relationships, documented reasoning, meaningful comparison and advice that takes account of the organisation’s wider environment rather than one supplier’s catalogue.
Vendor independence also means being willing to question technology that the business already uses. An objective IT security consultant should be able to conclude that an existing control is adequate, needs reconfiguration, duplicates another control or no longer suits the organisation’s risk profile. Independence is therefore relevant when reviewing incumbent suppliers as well as when considering new products.
Ask how the consultant will handle recommendations that affect existing contracts, renewal decisions or established internal processes. The advice should distinguish a genuine security requirement from a preference for replacing or retaining a particular system. This helps ensure that procurement and security decisions are based on operational evidence, contractual considerations and risk, rather than on a supplier relationship.