
Does small business backup cover cloud applications as well as local devices?
Small business backup can cover both cloud applications and local devices, but only when the backup plan is configured to protect each data source. Local files, servers and devices need device-level backup, while cloud applications may require a separate application-aware backup to retain data beyond the provider’s standard protection.
Small business backup should cover both cloud applications and local devices, but coverage is not automatic. A complete plan identifies where business data is created, stored and processed, then applies a suitable backup method to each location. This may include files on workstations, data held on servers, email, shared documents, customer records, accounting information, application databases and configuration data.
Cloud applications need particular attention because access to an application is not the same as ownership of an independent backup. A provider may protect its underlying infrastructure, but that protection is generally designed to keep the service operating rather than to give your business a recoverable copy of every file, message or record. Data can still be affected by accidental deletion, incorrect changes, compromised accounts, malicious activity, retention limits or the removal of a user account.
What should be included in cloud application backup?
- Business content: documents, spreadsheets, presentations, email, calendars, contacts and other information created or stored in the application.
- Application data: records held in line-of-business, finance, customer management, project management or other hosted systems.
- Versions and deleted items: earlier versions and recoverable deleted data can be important when a change is discovered later rather than immediately.
- Structure and metadata: folder arrangements, ownership, timestamps, labels and other information that gives files their meaning.
- Permissions and configuration: access settings, groups, workflows and configuration where the backup product can capture them. These may otherwise need to be documented and rebuilt separately.
The exact scope depends on the application and the backup method. Some services support detailed, application-aware recovery, while others may offer only export tools or limited retention. Before choosing a solution, confirm whether it can restore individual items, complete folders, application records and the relationships between them. A backup that copies files but cannot restore essential application data may not provide a practical recovery route.
Local devices require a different assessment. Desktop computers and laptops may contain locally saved documents, downloaded email, browser-based work files, specialist software data and configuration information. Servers may hold shared files, databases, line-of-business applications and system settings. These sources should be identified through an asset and data inventory rather than assuming that all important information sits in one shared location.
Device protection can involve file-level or image-based backup. File-level backup is useful when the priority is recovering selected documents and folders. Image-based backup can support a broader restoration of an operating system, applications, settings and data after hardware failure or serious corruption. The right approach depends on the role of the device and how quickly the business needs to resume its normal processes.
Synchronisation does not replace backup. Synchronised data mirrors changes between locations, so an accidental deletion or encrypted file may be replicated rather than safely preserved. Backup creates recovery points that can be kept separately and restored from an earlier state. Cloud applications may provide version history or recycle bins, but these features should be treated as useful recovery facilities within their stated limits, not as the entire backup strategy.
A suitable plan should also consider how an incident would be recovered. Important questions include:
- Can a single deleted email, file or record be restored without recovering the entire system?
- Can a complete server or device be rebuilt if its storage fails?
- How are cloud application accounts, permissions and authentication handled during recovery?
- Where are backup copies held, and are they sufficiently separated from the systems they protect?
- How long are recovery points retained, and does that period match the organisation’s operational and compliance needs?
- Can data be recovered in a usable format if the original application is unavailable?
- Are recovery procedures documented for the people responsible for carrying them out?
Security controls matter for both local and cloud backup. Backup accounts should have strong authentication, limited administrative access and clear separation of duties where appropriate. Backup data should be protected in transit and at rest, and retention settings should prevent important recovery points from being removed too easily. Monitoring should identify failed jobs, unusual deletion activity, capacity problems and authentication issues rather than merely confirming that a backup process ran.
Testing is the practical way to establish whether the backup covers what the business believes it covers. Tests should include individual file or email recovery as well as larger restores for critical systems. The result should be checked for completeness, permissions, usability and dependencies such as authentication, databases or connected applications. A successful job report alone does not prove that the restored data is complete or that staff can use it.
For a small business, the most reliable approach is to document each important data source, its owner, its backup method, its retention requirement and its recovery procedure. This produces a joined-up plan for cloud applications, local devices and the systems that connect them, rather than leaving protection dependent on assumptions about what a service provider or individual user is already covering.
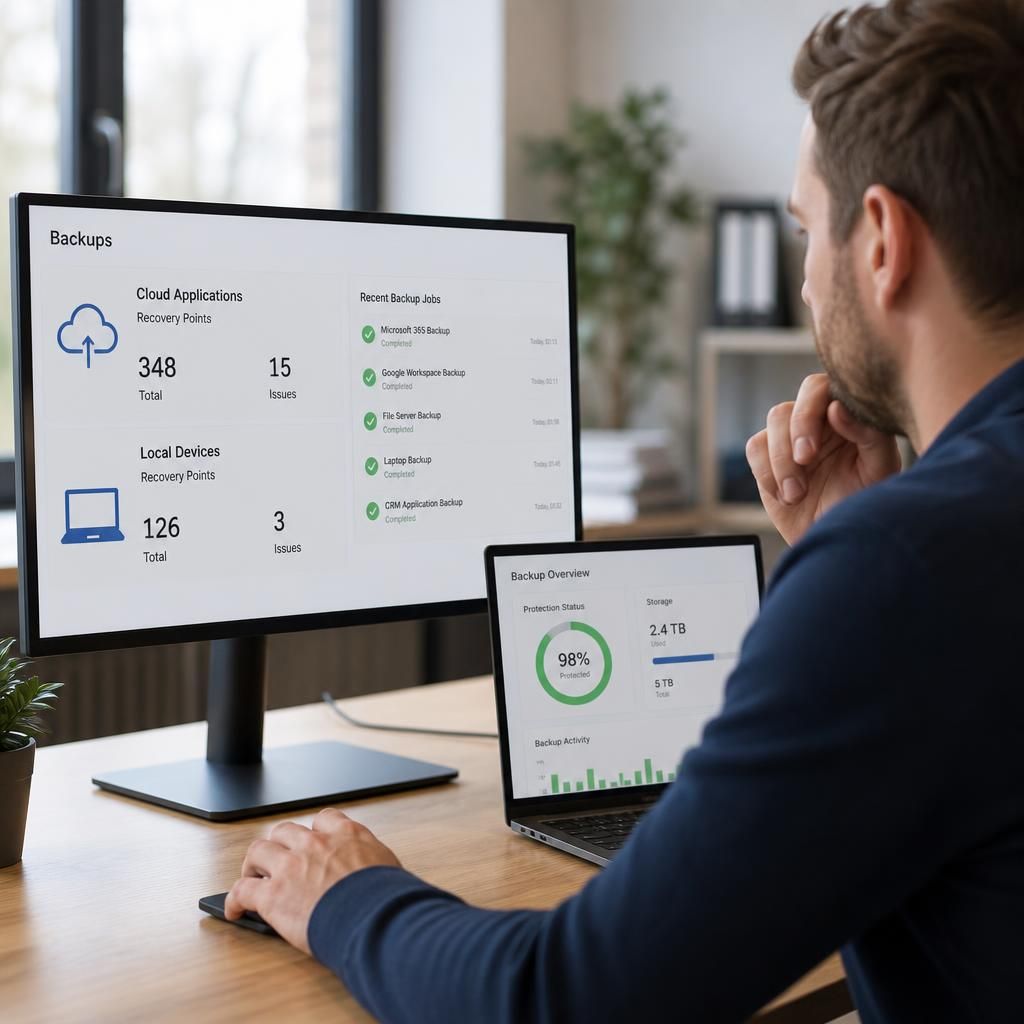
A cloud application backup should account for the access and dependencies needed to use the restored data. A recovered mailbox, customer record or shared document is not useful if administrators cannot regain access, user permissions are missing or connected services no longer work.
Document the application’s administrative accounts, authentication arrangements, user roles, domain settings and important integrations alongside the backup plan. During recovery, restore administrative access first, then rebuild permissions and connections before checking that the recovered information can be used in the normal business process. This makes the difference between having a copy of cloud data and having a workable recovery route.