
How should third-party access be governed in identity security?
Third-party access should be governed through documented approvals, named internal owners, least-privilege permissions, strong authentication and time-limited access. Organisations should record and monitor supplier activity, review permissions regularly, and revoke access promptly when the engagement or business need ends.
Third-party access governance is the set of policies, controls and accountability arrangements used to manage access by suppliers, contractors, consultants and other external organisations. Effective governance covers the entire relationship, from assessing the supplier and defining the permitted work to supervising access, handling changes and closing the relationship safely.
Start with a complete third-party access register. An organisation should know which external parties can access its systems, what business service each party supports, which information is involved, how access is provided and who is responsible for the relationship. The register should include direct users, supplier-managed accounts, remote support tools, application integrations, APIs and connections inherited through a parent or subcontracted provider. Without this inventory, dormant or overlooked access can remain outside normal identity controls.
Assess the supplier before access is created. The assessment should reflect the sensitivity of the systems and information involved. Relevant considerations may include the supplier’s security practices, use of subcontractors, data locations, incident management arrangements, regulatory obligations and dependence on privileged administration. A supplier connecting to a public information portal presents a different risk from one managing core infrastructure or accessing personal, financial or commercially sensitive data.
The outcome should determine the safeguards required rather than applying identical controls to every supplier. Higher-risk relationships may require stronger contractual commitments, additional technical isolation, more detailed activity records and greater scrutiny of changes. Risk assessments should also be revisited when the supplier’s role, systems, ownership, location or data access changes.
Define the permitted activity precisely. A third party should only be able to perform the tasks necessary for its agreed service. Governance documentation should state which environments may be accessed, which actions are allowed, what information may be viewed or transferred, and whether access is permitted directly or only through an approved support route. Separating development, test and production environments can reduce the consequences of an error or compromised supplier account.
Where administration is required, organisations should distinguish between viewing information, making configuration changes, creating accounts, exporting data and carrying out destructive actions. These permissions should be assigned through managed roles where possible, rather than through broad, shared or permanent administrator access. Individual identities also make actions attributable to a specific person and supplier.
Put the obligations into the contract. Security requirements should not rely solely on informal expectations. Supplier agreements should address:
- the systems, services and information covered by the engagement;
- the security standards and internal policies the supplier must follow;
- responsibility for managing the supplier’s personnel and subcontractors;
- requirements for reporting suspected security incidents and unauthorised access;
- restrictions on copying, storing or disclosing business information;
- requirements to preserve relevant logs and cooperate with investigations;
- rights to assess assurance evidence where appropriate; and
- secure return or disposal of information when the relationship ends.
Contracts should also address fourth-party access. A supplier may rely on another organisation for hosting, support or specialist services, creating an indirect route into the business. The organisation should understand those dependencies and establish whether subcontractors must meet equivalent security requirements.
Use a controlled access path. External users should connect through identity services and remote access arrangements that the organisation can administer and inspect. Direct exposure of management interfaces to the internet should be avoided where a controlled alternative is available. Network segmentation, device checks and restrictions on which systems can communicate with one another can limit the reach of a compromised supplier account.
Privileged work benefits from additional separation. For example, an external engineer might use one identity for ordinary collaboration and a separately controlled identity for approved administration. Administrative sessions can be routed through a monitored access mechanism that records commands or session activity, subject to legal, contractual and privacy requirements. Credentials should never be shared between supplier personnel, even when they work for the same organisation.
Make changes subject to governance. Supplier access often becomes risky when the original service expands informally. Requests to reach a new application, change the type of information handled, add a subcontractor or introduce an integration should trigger a documented change assessment. The assessment should consider business justification, affected data, technical dependencies and whether existing controls remain suitable.
Identity governance should also account for personnel changes within the supplier. The supplier should notify the organisation when an authorised individual leaves, changes role or no longer needs access. Where access is linked to a supplier-managed identity source, the organisation should establish how updates are synchronised and how failures are detected.
Monitor for misuse and investigate exceptions. Logs should provide enough context to identify the external user, supplier, system, action and time involved. Monitoring should focus on activity that differs from the agreed service, such as access to an unrelated system, unusual data extraction, repeated failed authentication, changes to security settings or administration outside an approved work item.
Exception handling is important because legitimate maintenance may sometimes require a control to be bypassed. Each exception should have a recorded reason, named authorisation, defined scope, compensating safeguards and an end point. Repeated exceptions may indicate that the access model or supplier contract needs redesign rather than continued reliance on temporary workarounds.
Test the arrangements, not just the paperwork. Governance evidence can include access records, supplier assessments, contract clauses, approval trails, authentication records, session logs, incident reports and closure confirmations. Reviewing this evidence helps establish whether the documented process matches actual access. Testing should sample different supplier types and include technically complex arrangements such as service accounts, federated identities and application-to-application connections.
When an engagement ends, closure should cover more than disabling a named user. The organisation should remove supplier groups, certificates, API keys, remote support agents, firewall rules, integration permissions and locally stored credentials associated with the service. It should also confirm the return or secure disposal of business information and retain appropriate evidence of the closure.
Third-party access governance is therefore a shared operating process involving procurement, legal, information security, IT and the internal service owner. S2 Technology Group can help organisations review identity and access arrangements, document supplier controls and align technical measures with the risks created by external access.
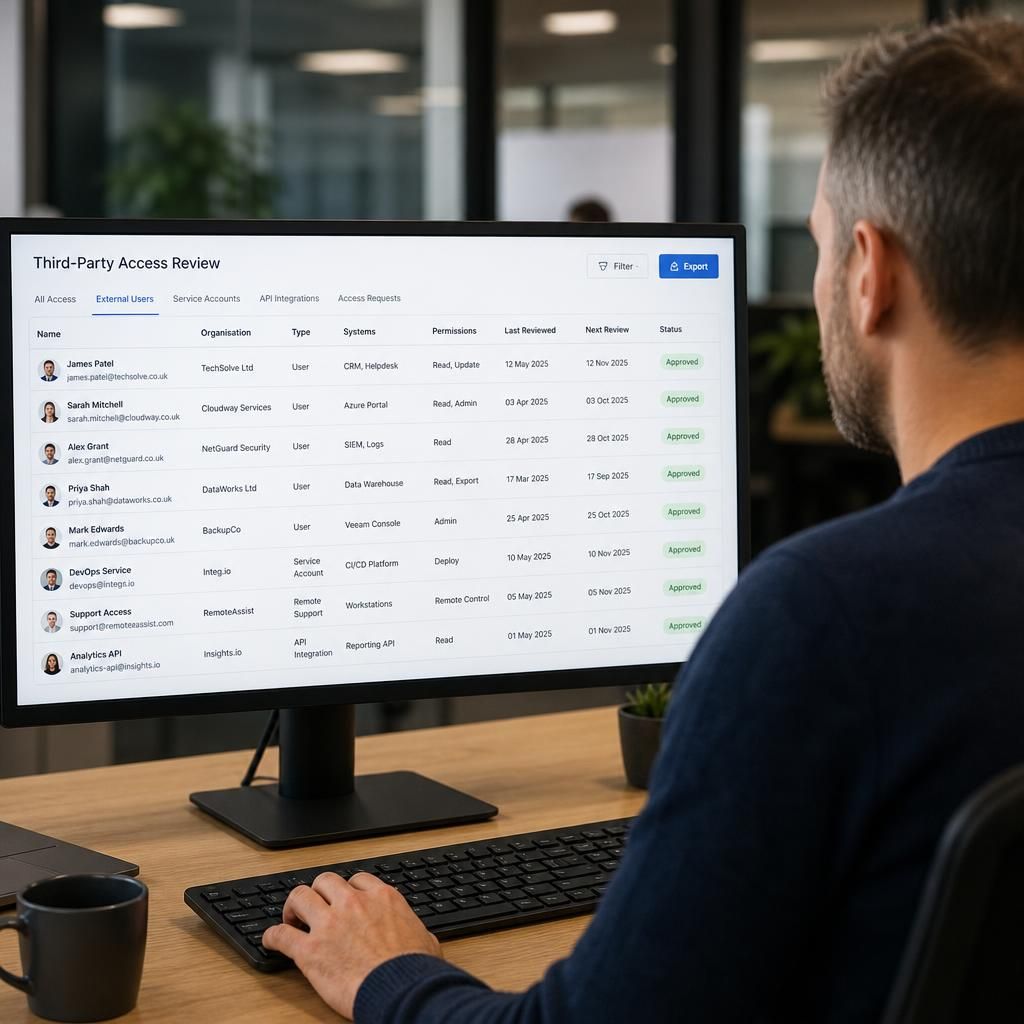
Third-party access governance must cover non-human identities as well as supplier personnel. API connections, integration accounts and automated service identities can access business data without a person signing in, so they require the same ownership, approval and review discipline as user accounts.
Each integration should have a named internal owner, a documented business purpose and permissions limited to the specific data and actions it needs. Where possible, interactive sign-in should be disabled, credentials should be stored using an approved secrets-management method, and authentication keys should be rotated under a defined process rather than left unchanged indefinitely.
- Record which supplier, application or service operates the identity.
- Restrict permissions to the required systems, functions and data.
- Separate credentials for development, testing and production.
- Monitor calls, authentication failures and unusual data volumes.
- Reassess the connection when the supplier, application or data flow changes.
This approach prevents an overlooked integration from becoming an unaccountable route into identity systems and ensures that third-party access remains attributable, limited and subject to business ownership.