
What does a managed firewall contribute to business cyber security?
A managed firewall monitors and controls traffic between a business network and external networks, applying defined security rules to block unauthorised or suspicious connections. It contributes to cyber security by reducing exposure to network-based threats, providing visibility of traffic activity and ensuring firewall policies are maintained as the business changes.
A managed firewall is a centrally administered security control that enforces how data can enter, leave and move between a business’s networks. Its contribution to cyber security extends beyond installing a firewall appliance: it includes designing appropriate rules, controlling access between network zones, reviewing configuration changes and maintaining the control as systems, users and business requirements develop.
It reduces the attack surface. Internet-facing services, remote access points and exposed network ports can provide routes into business systems. A firewall restricts these routes to traffic that has a defined business purpose. Unnecessary services can be disabled, while approved connections can be limited by source, destination, protocol, port or user context where the technology supports it. This makes it harder for opportunistic scans, automated attacks and unauthorised connection attempts to reach internal resources.
A managed firewall can also apply different controls to different parts of the environment. Network segmentation separates areas such as office devices, servers, guest Wi-Fi, voice systems, operational technology and administrative interfaces. If one device or zone is compromised, segmentation can restrict the attacker’s ability to move laterally to more sensitive systems. The design should reflect how the organisation actually works rather than treating every internal device as equally trusted.
It controls outbound traffic as well as inbound traffic. Preventing unauthorised connections leaving the network can help limit malware communicating with command-and-control infrastructure, transferring data to an unapproved destination or misusing a compromised account. Egress controls are most effective when they are based on an understanding of required applications and services, with exceptions documented and reviewed rather than added permanently for convenience.
For organisations with remote workers or multiple sites, firewall policies can govern secure connections between users, offices, data centres and cloud environments. A virtual private network may encrypt traffic across an untrusted connection, but it does not make the user or device trustworthy by itself. Strong authentication, appropriate device security and access limited to the resources required for a person’s role remain necessary. The firewall is one part of that access design, not a replacement for identity and endpoint controls.
Management is important because firewall effectiveness depends on its configuration over time. A managed service should include a documented process for requesting, approving, implementing and recording rule changes. Rules that were created for a temporary project, former employee, retired application or replaced supplier can otherwise remain active and create unnecessary exposure. Periodic review should identify rules that are overly broad, duplicated, unused or inconsistent with current business requirements.
Good administration also considers the order in which rules are evaluated, the use of default-deny principles where appropriate, administrative privileges and the separation of firewall management from ordinary user access. Configuration backups and controlled updates help preserve a known, recoverable security position if the device fails or a change has an unintended effect.
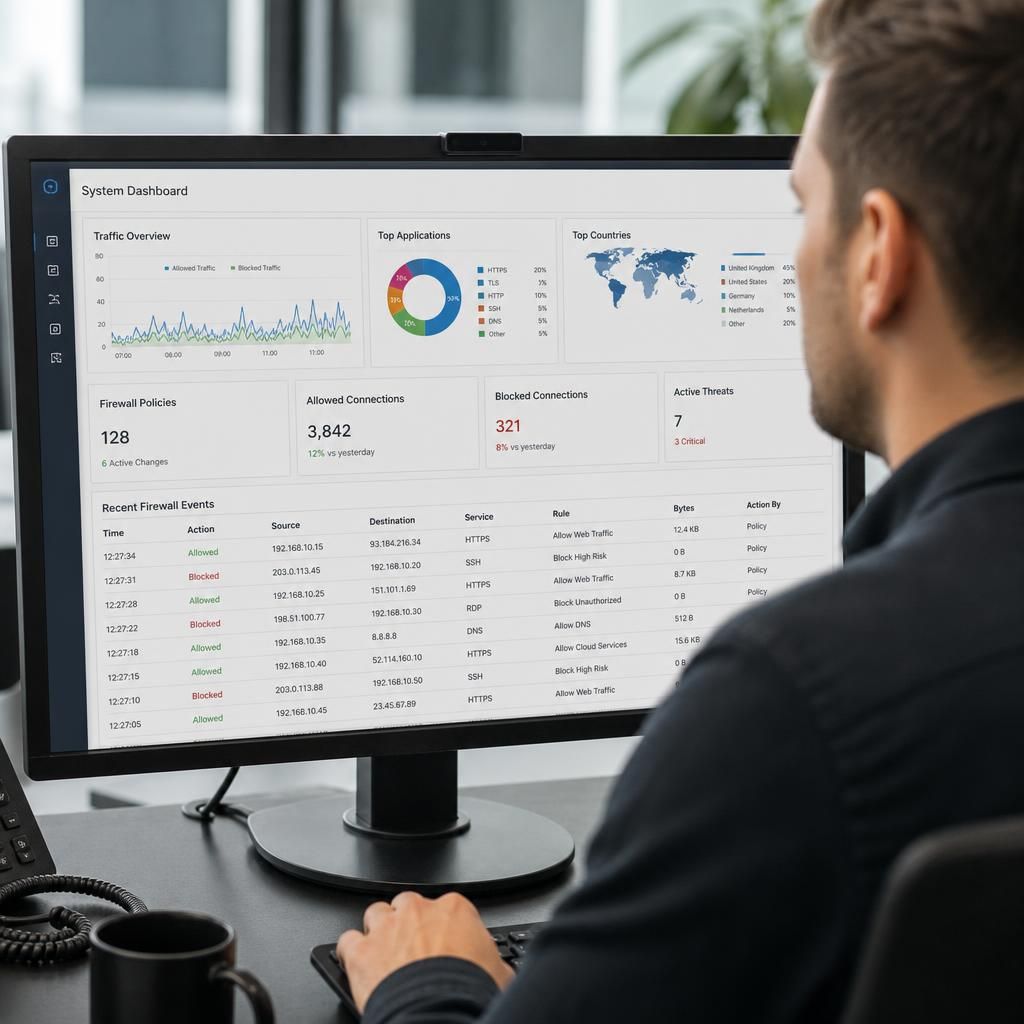
Firewall records can support investigation and governance by showing connection attempts, blocked activity, policy changes and administrative actions. These records need sensible retention, access restrictions and time synchronisation to remain useful. They should be considered alongside endpoint, identity, server and cloud records rather than treated as a complete account of everything happening in the organisation.
A managed firewall does not detect every form of cyber threat. It may not identify an authorised user misusing access, a malicious file delivered through an approved service, an attack against an application that appears legitimate, or a device already compromised inside the network. Encrypted traffic can also reduce the visibility available to traditional inspection unless suitable, proportionate controls are designed. Effective cyber security therefore combines firewall management with endpoint protection, identity and access security, secure configuration, patching, staff awareness and incident response planning.
When assessing a managed firewall service, a business should ask:
- Which network zones, sites, cloud connections and remote access routes are covered?
- How are new rules requested, authorised, tested and recorded?
- How are obsolete, broad or unused rules identified and removed?
- Which events are logged, who can access the records and how long are they retained?
- How are firmware, software and security configuration updates managed?
- How does the firewall integrate with identity, endpoint, vulnerability and incident response controls?
- What evidence is provided to show that the configuration remains aligned with the organisation’s risks?
The practical value of a managed firewall is therefore its combination of technical enforcement and disciplined administration. It can limit unnecessary network exposure, contain movement between systems, control remote and outbound connections, and provide evidence for investigation. It should be treated as a foundational layer within a broader cyber security strategy, with its rules and operation linked to the organisation’s risk assessment and changing technology environment.
A managed firewall can help balance security inspection with operational requirements. Not every connection should be inspected in the same way. Encrypted traffic inspection, for example, may require suitable certificate management, processing capacity and clear decisions about sensitive information. A properly managed approach identifies where deeper inspection is justified and where it could create privacy, compatibility or performance issues.
This prevents security controls from being applied without regard to how the business operates. Inspection policies can be documented, tested and reviewed when applications or network services change, helping the firewall provide useful protection without introducing avoidable disruption.