
How is user access controlled when staff roles change?
User access is controlled by linking permissions to each staff member’s role, then reviewing and adjusting those permissions when responsibilities change. Access that is no longer required should be removed promptly, while leavers should be securely offboarded by disabling accounts, revoking sessions and recovering organisational devices where applicable.
User access is controlled through a documented identity and access management process that connects each person’s permissions to an approved job function. When a staff member changes role, the organisation compares their new responsibilities with their existing access, authorises the required changes, and records what was altered and why. This prevents permissions from accumulating simply because an employee has moved between teams.
A sound process normally includes the following stages:
- Role definition: standard roles are mapped to the systems, data and functions needed for particular responsibilities. Access is granted according to the role rather than personal preference.
- Change notification: a manager or authorised member of the business notifies the IT or virtual IT team before, or as part of, the employee’s transfer. The request should state the effective date, new responsibilities and any access that must be retained.
- Approval: the requested access is checked by the relevant manager, system owner or data owner. Sensitive systems may need an additional approval so that business necessity is considered separately from technical convenience.
- Permission adjustment: the employee is added to the groups or roles required for the new position, while access that is no longer relevant is removed. Where possible, group-based access is preferable to assigning individual permissions across many systems.
- Validation: the completed changes are checked against the approved request. This can include confirming that the employee can use the applications needed for the new role without retaining unrelated or excessive privileges.
- Record keeping: the request, approval, implementation details and review outcome are retained as an audit trail.
The principle of least privilege is central to this process. A user should have the minimum access needed to perform their duties, for only as long as it is needed. This includes considering permissions within applications, shared folders, cloud platforms, databases, remote access tools and administrative consoles. A role change should not automatically result in broad access merely because a standard group appears convenient.
Role changes also need to account for inherited access. A user may receive permissions through several group memberships, nested groups, shared mailboxes or application roles. Removing one visible permission may not remove the underlying access if another route still provides it. Effective reviews therefore examine the access the account actually has, not just the individual requests recorded in an IT ticket.
Higher-risk permissions require additional controls. Administrative rights, access to financial or personal data, security configuration, backup systems and remote management tools should be assigned separately from ordinary user access wherever practical. Privileged access may be time-limited, subject to stronger authentication, or restricted to a named administrative account. Separating everyday work from administration also makes unusual activity easier to investigate.
Temporary access should have an owner, a defined purpose and an expiry date. This applies to project work, cover arrangements, consultancy, investigations and emergency administration. Without an expiry mechanism, temporary permissions can become permanent by default. A review should confirm whether the access remains necessary before it is extended.
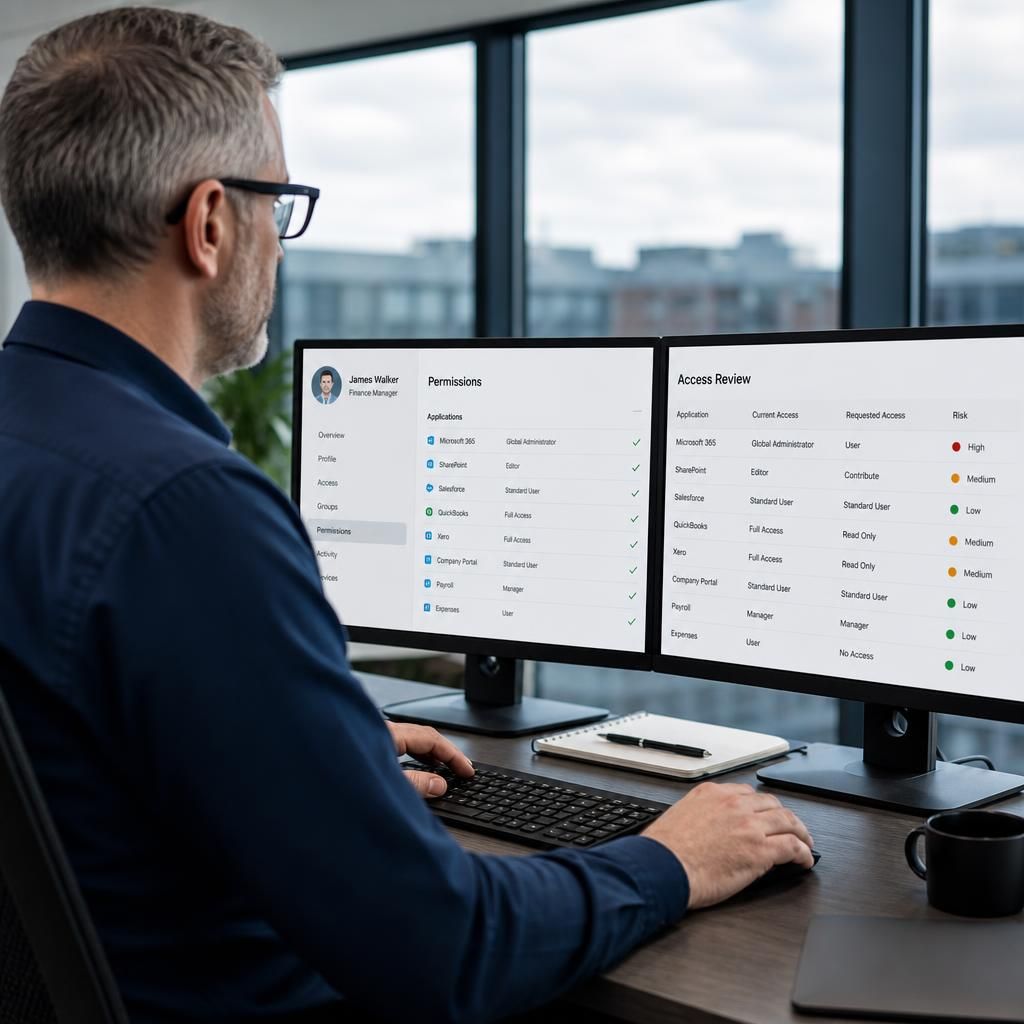
Access reviews should take place at planned intervals and after significant organisational changes. Managers and system owners can confirm that users still need their assigned roles, while technical checks identify dormant accounts, unexpected group memberships, duplicate identities and permissions that have not been used. Usage information can support a review, but lack of recent use should be investigated rather than treated as the only reason for removal.
The process should also address non-human accounts. Service accounts, application identities, scheduled tasks and integration accounts do not change jobs in the same way as employees, but their permissions can become excessive when systems or responsibilities change. Each should have a named owner, a documented purpose and an appropriate method for managing its credentials and privileges.
Automation can help apply consistent rules, particularly where an organisation uses a central directory connected to cloud and business applications. Automated workflows may create tasks when a personnel record changes, apply approved group memberships and flag access requiring human approval. Automation should not replace governance: exceptions, privileged access and ambiguous role changes still need review by an authorised person.
When an organisation uses virtual IT services, the access-control process should be documented in the service arrangements and aligned with the customer’s internal approval structure. The provider may administer directories, applications and security tools, but the customer remains responsible for confirming who should have access to business information. Clear responsibilities, named approvers and retained records reduce the risk of changes being made without appropriate authority.
A well-managed review should be able to answer four questions: what access does the user have, why do they need it, who approved it, and when should it next be reviewed? If those answers cannot be established, the permission should be treated as requiring investigation rather than being left in place indefinitely.
Role changes should also be checked for conflicts between permissions, not only for access that is missing or excessive. For example, combining the ability to create a supplier with the ability to approve payments may create a segregation-of-duties risk, even if each permission is appropriate in isolation. Similar conflicts can arise when one person moves between finance, procurement, administration or security responsibilities.
An access review should therefore consider how permissions work together across business systems. If overlapping access is necessary during a handover, the exception should have an authorised owner, a documented reason and a defined end date. A separate review or approval step may provide additional oversight until the transition is complete.
Discuss User Access Controls When Staff Roles Change
Discuss your user access process with S2 Technology Group to identify gaps in role-change reviews, approval records and permission removal. We can help you assess whether your virtual IT arrangements support controlled access throughout employee transitions.