
Cyber Security Services
Cyber security services protect business systems, accounts and data from threats such as phishing, malware and unauthorised access. S2 Technology Group helps organisations assess risk, strengthen controls and manage security across users, devices, networks and cloud environments.
Business Outcomes of Effective Cyber Security
Effective cyber security gives organisations a structured way to reduce avoidable disruption, control access, identify weaknesses and respond to incidents. It also supports informed technology decisions by showing where protective measures, staff practices and recovery planning need improvement.
Reduced Business Disruption
Stronger protection against phishing, malware and unauthorised access helps reduce the likelihood that security incidents will interrupt essential systems, applications and business processes.
Controlled Access to Business Data
Clearly defined permissions and access controls help ensure that users can reach the systems and information needed for their work without granting unnecessary access.
Earlier Identification of Weaknesses
Regular security assessment highlights weaknesses in devices, networks, cloud environments and user practices, allowing risks to be addressed before they develop into incidents.
Safer Remote and Cloud Working
Security controls applied across remote access and cloud services help protect accounts, data and business systems when employees work away from traditional office networks.
More Effective Incident Response
Documented security processes give organisations a clearer basis for identifying, containing and managing incidents, while supporting coordination with disaster recovery arrangements.
Better-Informed Technology Decisions
A clear view of security risks helps decision-makers prioritise improvements to protective controls, staff practices, infrastructure and recovery planning.
Practical Cyber Security, Delivered by People
Cyber security planning matches protective measures to how an organisation works. It considers staff access, hosted systems and activities that would be most disruptive if interrupted.
At S2, we discuss business priorities before recommending changes. We explain each control’s purpose, clarify responsibilities, and distinguish essential improvements from work that can be planned later. This helps decision-makers set priorities and budgets with a clearer understanding of the work involved.
Security also depends on what happens after controls are introduced. We help document procedures, review findings with responsible people and refine the approach as systems or working practices change. The result is a plan that can be understood and followed, not a technical document left unused.
Specialist Cyber Security Expertise for Growing Businesses
Cyber security requires more than installing individual protective tools. It involves understanding how identities, endpoints, infrastructure, applications and information interact, then assessing how weaknesses in one area could affect the wider business. S2 Technology Group applies this joined-up view when examining security requirements and shaping practical improvements.
Its specialist approach considers both technical configuration and the way technology is governed. This includes examining privilege levels, authentication practices, system exposure, software maintenance, network design and the quality of security evidence available to decision-makers. The aim is to distinguish isolated technical issues from underlying weaknesses that require a broader response.
Expert advice is also valuable when security measures need to be tested, explained or developed over time. S2 can help organisations interpret technical findings, compare remediation priorities and establish a more consistent basis for future decisions. This depth of analysis supports businesses that need informed cyber security guidance without maintaining every specialist capability in-house.
Questions to Ask Before Choosing Cyber Security Services
How should cyber security services handle third-party supplier access?
Assess whether proposed controls align with regulatory duties, contractual expectations, cyber insurance requirements and risk appetite. Document exceptions, assign ownership, and retain evidence demonstrating decisions and ongoing oversight over time.
What should cyber security services include in an incident response plan?
It should define reporting routes, decision authority, containment steps, evidence handling, communications, legal considerations, recovery priorities and post-incident review. Plans should be tested so responsibilities remain clear when incidents occur.
How should a business measure the effectiveness of cyber security services?
Use measures such as control coverage, unresolved findings, privileged-account reviews, patching trends, phishing-reporting behaviour, and recovery-test results. Compare evidence over time, investigate deterioration, and report exceptions to responsible business leaders.
How do cyber security services identify unknown devices on a business network?
Identify unknown devices by combining asset inventories, network discovery, authentication records, address-resolution data and endpoint telemetry. Reconcile findings regularly, investigate unmanaged equipment, then isolate unauthorised connections.
How should cyber security services secure remote access for business users?
Secure remote access combines strong authentication, least-privilege permissions, managed devices, encrypted connections and session monitoring. Policies should define approved access methods, review exceptions, and remove access promptly when circumstances change.
Security Clarity
S2 connects cyber security decisions with wider IT planning, helping businesses align protection across users, devices, networks and cloud systems.
Businesses We Support
Professional Services Organisations
Professional services firms handle confidential client information and depend on controlled access to documents, email and cloud applications. Cyber security measures can help them manage user permissions, reduce phishing risk and apply consistent security procedures across the organisation.
Manufacturing Businesses
Manufacturers often rely on connected workstations, production systems and shared operational data. A structured cyber security approach considers device protection, network controls and access rights while supporting the continuity of essential business processes.
Logistics and Distribution Teams
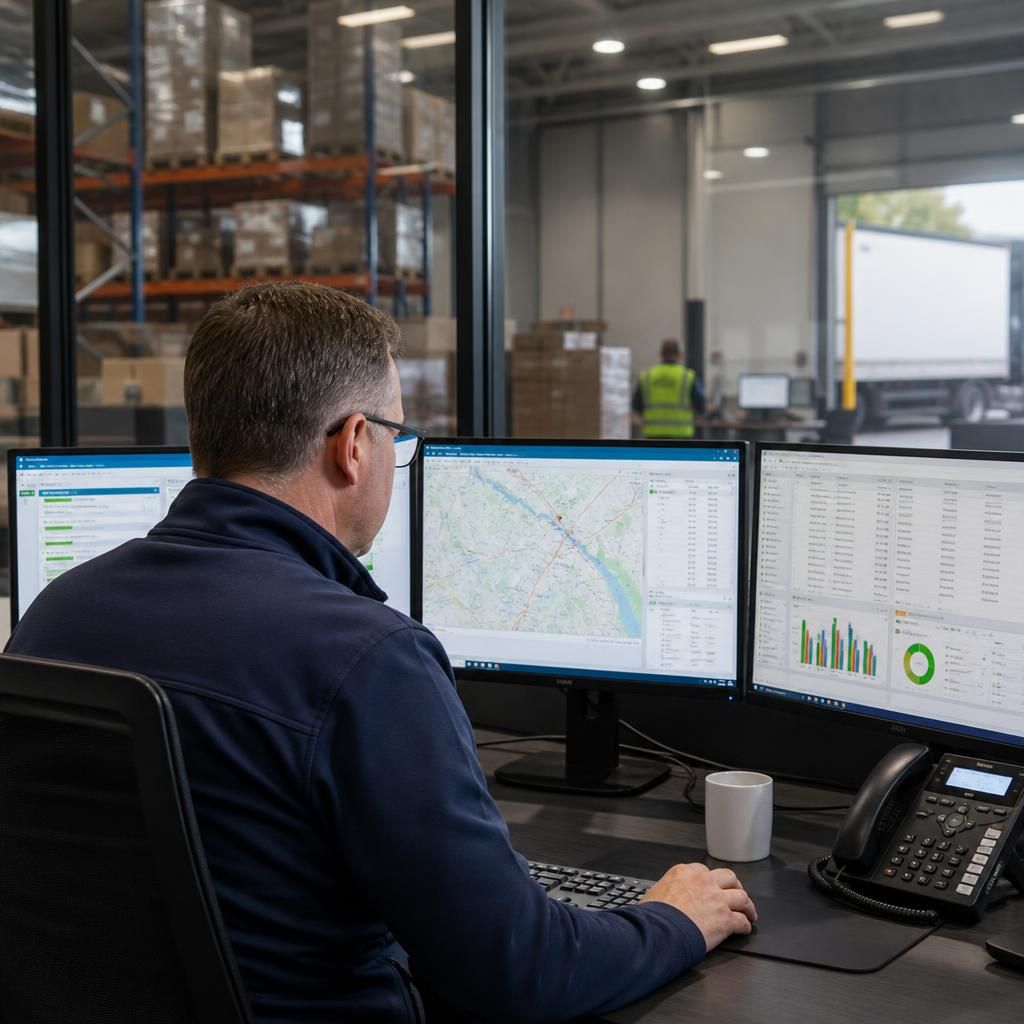
Logistics organisations use technology to coordinate people, sites, suppliers and delivery information. Security planning helps identify which accounts and systems require stronger controls, supporting safer access to operational data and reducing avoidable exposure.
Multi-Site Organisations
Businesses operating across multiple locations need security controls that can be applied consistently without overlooking local working practices. Cyber security reviews can examine user access, connectivity, devices and cloud services across the organisation.
Cyber Security for Different Business Needs
Different situations call for different cyber security measures: onboarding a growing workforce, integrating a new office, meeting contractual security requirements, or investigating suspicious activity. These examples help identify which areas deserve attention as your organisation and its technology change.
Onboarding New Staff
Adding employees, contractors or remote users requires careful control of accounts and permissions. Cyber security measures can help ensure access matches each person’s role, while reducing the risk of unused or excessive privileges.
Integrating a New Office
A new site introduces additional networks, devices and access points to protect. Reviewing connectivity, user permissions and security controls before systems are joined helps maintain a consistent approach across locations.
Meeting Contractual Requirements
Customers, partners and regulated supply chains may require evidence of specific security practices. We help identify relevant controls, document how they operate and highlight gaps that need to be addressed.
Investigating Suspicious Activity
Unusual sign-ins, unexpected messages or unexplained device behaviour should be assessed rather than dismissed. Reviewing available information can help establish what happened, identify affected accounts or systems, and guide the next security measures.
Cyber Security Services: Frequently Asked Questions
How often should a business review its cyber security controls?
Services may include vulnerability reviews, security policies, access management, endpoint protection, staff guidance, incident planning and compliance support, selected according to business risks, systems and regulatory requirements for each organisation.
What does a cyber security risk assessment cover?
A cyber security risk assessment examines threats, vulnerabilities, existing safeguards, access arrangements, data exposure, system dependencies and potential business impact, producing prioritised actions for the organisation to reduce identified risk.
How do cyber security services protect businesses from phishing attacks?
Protection combines email filtering, multi-factor authentication, secure links, user reporting and practical awareness guidance. These measures reduce malicious messages reaching inboxes and limit potential damage if credentials are accidentally disclosed.
How can cyber security services protect a business from ransomware?
Ransomware protection combines offline or isolated backups, restricted administrative privileges, application controls, network segmentation and tested recovery procedures, limiting encryption spread and supporting recovery when systems are compromised by ransomware.
What does cyber security monitoring involve?
Cyber security monitoring involves reviewing alerts, logs and system activity for signs of compromise or policy violations. Findings are assessed, prioritised and escalated for investigation or corrective action where necessary.
Discuss Your Cyber Security Requirements
Discuss your current security concerns with S2 Technology Group to identify practical next steps. An initial conversation can help clarify risks, priorities and responsibilities, giving your organisation a more informed basis for planning cyber security improvements.