
Cyber Security for Small Business
Cyber security for small business combines policies, controls and technical safeguards to protect systems, accounts and information from unauthorised access, disruption and fraud. S2 Technology Group provides practical business cyber security guidance and support suited to growing organisations.
Business Outcomes of Effective Cyber Security
Effective controls do more than block attacks: they help small organisations maintain operations, protect sensitive records, meet client expectations and make informed technology decisions. The following outcomes show how structured cyber security supports practical business continuity and risk management.
Reduced risk of unauthorised access
Strong account controls, multi-factor authentication and appropriate access permissions make it harder for attackers to compromise business systems and reach sensitive information.
More resilient business operations
Backups, recovery procedures and tested continuity measures help a small business restore important data and services following incidents such as ransomware, hardware failure or accidental deletion.
Better protection for business information
Security controls help safeguard customer records, financial information, intellectual property and employee data against theft, misuse and inappropriate access.
Safer use of cloud and remote access
Secure configuration, device controls and clear access rules reduce the risks associated with staff connecting to business systems from different locations or using cloud-based services.
Stronger client and supplier confidence
Documented security practices provide evidence that the business takes information protection seriously, which can support due diligence processes and contractual requirements.
Clearer priorities for technology investment
Regular risk assessment helps identify weaknesses, rank improvements by business impact and direct limited budgets towards controls that address the most important risks.
More informed staff security decisions
Practical policies and awareness guidance help employees recognise phishing, handle information correctly and report suspicious activity before it develops into a larger incident.
Practical Cyber Security Guidance for Growing Businesses
Effective cyber security for a small business begins with knowing which systems and accounts matter most, who can access them and where weaknesses could interrupt work or expose information. This understanding helps separate essential controls from unnecessary complexity, so security can be managed alongside everyday responsibilities.
S2 Technology Group takes a practical approach by considering users, devices, cloud services, connectivity and access permissions together. Recommendations are based on the organisation’s working practices and priorities, with technical decisions explained in clear business terms rather than presented as a fixed checklist.
Good security also depends on people. Clear guidance can help staff recognise suspicious activity, handle information appropriately and report concerns. As the business changes, its controls should be reviewed so that new users, systems and working arrangements are considered as part of an ongoing cyber security process.
Specialist Cyber Security Knowledge for Small Businesses
Specialist cyber security for a small business is the structured management of digital risk across technology, processes and governance. It covers more than antivirus software or firewall configuration: effective protection must address how information is stored, transmitted, accessed and recovered when business conditions change.
S2 Technology Group applies IT security knowledge to the practical constraints faced by growing organisations, where technology may span cloud platforms, office infrastructure, remote connections and specialist line-of-business systems. This broader view helps distinguish isolated technical issues from wider weaknesses in architecture, oversight or operational resilience, supporting proportionate decisions about risk treatment and investment.
As a managed IT services provider, S2 combines cyber security expertise with knowledge of the infrastructure that supports day-to-day operations. That perspective is valuable when reviewing proposed changes, assessing the security implications of new technology, and aligning protective measures with business requirements, client expectations and information security responsibilities.
Questions to Ask About Small Business Cyber Security
How should small businesses prioritise cyber security risks?
Ask whether recommendations are prioritised by business impact, supported by clear ownership, and tested through review. A useful provider explains residual risk, evidence, and decisions requiring management approval from stakeholders.
What should a cyber security assessment for a small business include?
It should examine assets, identities, vulnerabilities, exposure, regulatory obligations and likely attack paths, then document evidence, findings, ownership and review requirements in an auditable report for management, plus agreed next steps.
How can a small business verify that its cyber security controls work?
Verification should combine configuration reviews, access checks, vulnerability testing, alert validation, backup restoration exercises and documented remediation. Repeating tests after changes provides evidence that controls remain effective, not merely present.
How are cyber security alerts escalated when technical action could disrupt operations?
Escalation should define severity thresholds, authorised decision-makers, containment options and communication routes. Providers should distinguish confirmed compromise from false positives, preserving evidence while coordinating proportionate action with relevant operational owners.
What should small businesses check before choosing cyber security services?
Check the provider’s scope, security responsibilities, data-handling arrangements, reporting commitments, contractual terms, relevant experience and escalation process. Confirm recommendations fit your systems, regulatory duties and internal capability before committing resources.
Contextual Security
S2 Technology Group uniquely combines cyber security expertise with managed IT knowledge, aligning practical protection with each small business’s infrastructure.
Businesses We Support with Cyber Security
Professional Services Firms
Professional services businesses often manage sensitive client records, financial information and confidential correspondence across cloud applications and employee devices. Cyber security priorities can include strong account protection, appropriate access permissions, secure information handling and clear procedures for reporting suspicious activity. S2 Technology Group helps assess these controls in relation to the firm’s working practices and technology environment.
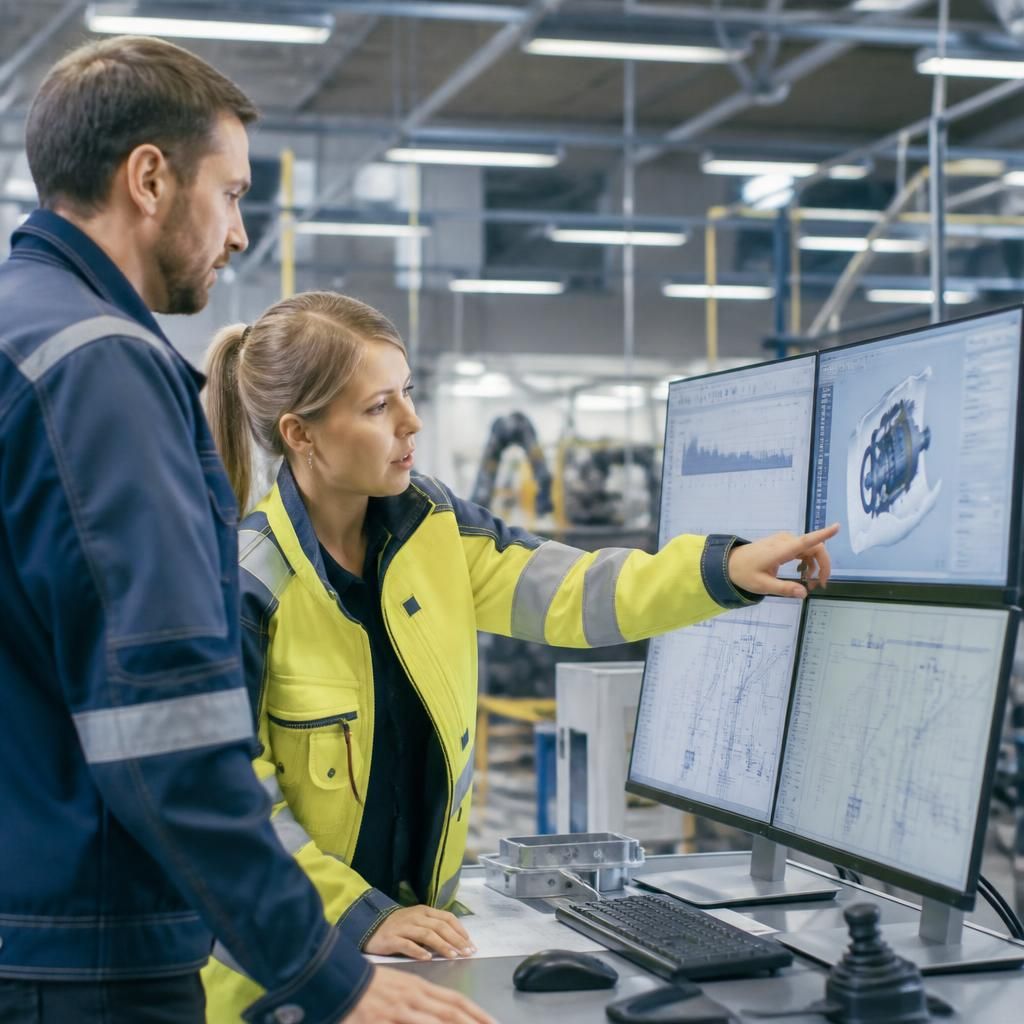
Manufacturing Businesses
Manufacturers may depend on connected workstations, production systems, shared files and supplier communications to maintain operations. A cyber security review can consider how users, devices and networks are separated, which accounts have elevated access and how important information is protected. S2 Technology Group applies managed IT knowledge to help align practical safeguards with the organisation’s operational requirements.
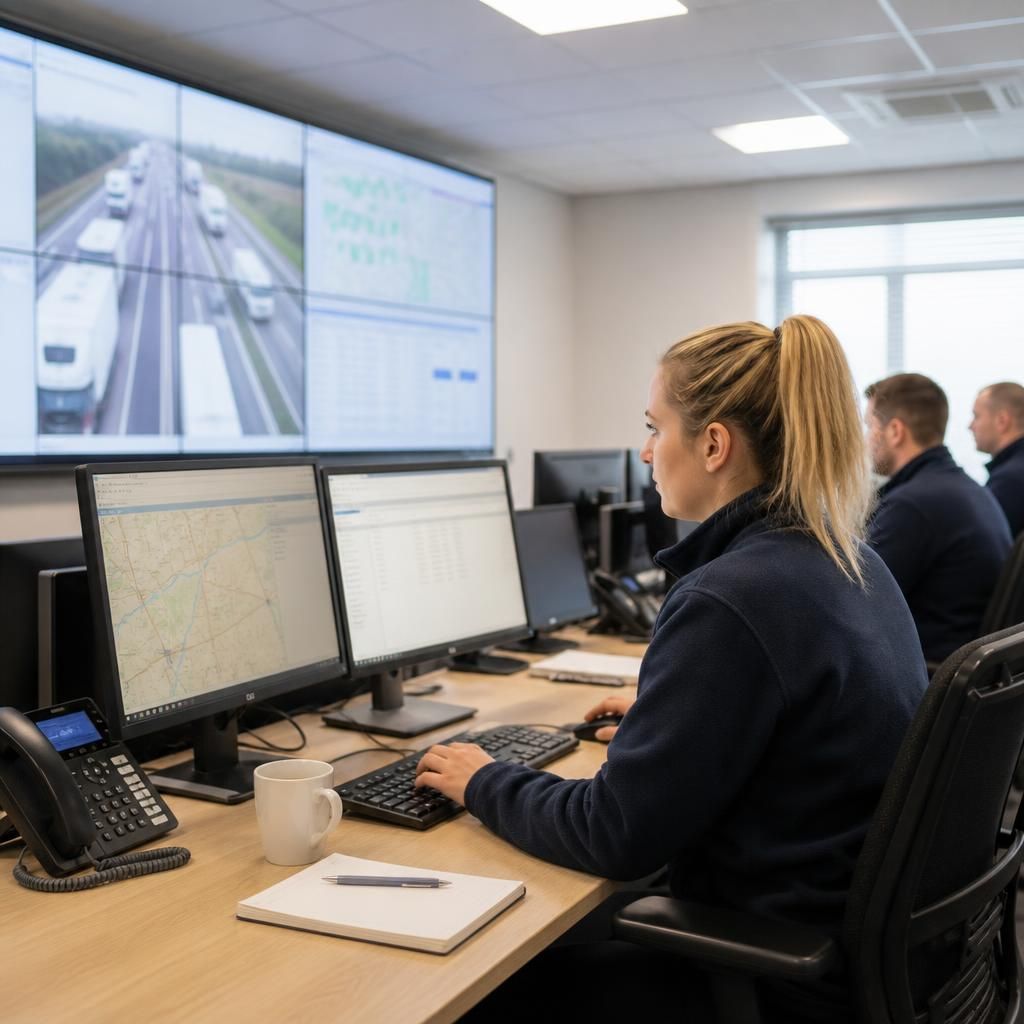
Logistics Providers
Logistics organisations rely on connected systems for scheduling, communication, records and coordination with customers or suppliers. Disruption or unauthorised access can affect several linked processes, so security planning should cover user accounts, devices, cloud services and connectivity together. S2 Technology Group provides guidance that relates cyber security controls to the way the logistics business operates.
Multi-Site Organisations
Businesses operating across multiple locations need consistent security practices without overlooking differences between sites, users and systems. Areas for consideration may include remote access, account permissions, device management, network arrangements and staff awareness. S2 Technology Group helps growing organisations review these dependencies and develop cyber security measures that reflect their technical complexity and business priorities.
Cyber Security for Different Small Business Needs
Small businesses can require cyber security support for different reasons, from reviewing weaknesses before a technology change to strengthening protection after growth, restructuring or new compliance expectations. The appropriate focus depends on risk, operational impact and available internal expertise.
No In-House IT Expertise
Small businesses without dedicated IT staff may need help identifying cyber risks, setting sensible policies and applying essential controls. This provides a structured approach without requiring the organisation to manage every security decision internally.
Business Growth And New Users
Growth can introduce new accounts, devices, applications and access permissions. Cyber security support can help review how these changes affect risk, remove unnecessary access and keep protection aligned with the way the business is developing.
Cloud And Remote Working
Businesses using cloud platforms or remote access need to consider identity protection, device security, authentication and how information is shared. Reviewing these areas helps ensure convenience does not create avoidable weaknesses.
Customer Or Compliance Requirements
Some organisations need to demonstrate that they manage information and access responsibly when working with customers, suppliers or regulated processes. Clear policies, documented controls and regular reviews can support a more consistent security position.
After A Security Concern
A suspected phishing message, unusual account activity or other security concern can highlight weaknesses in existing arrangements. A review can help establish what happened, check related controls and identify practical improvements for reducing repeat risks.
Cyber Security for Small Business: Frequently Asked Questions
What cyber security policies should a small business have?
Small businesses face phishing, ransomware, account compromise and data loss, often through ordinary email, devices or cloud services. Layered controls reduce exposure and support safer, more resilient operations and continuity.
Can small businesses outsource cyber security?
Yes—outsourcing cyber security gives small businesses access to specialist guidance, monitoring and support without maintaining a dedicated internal security team. Responsibilities, escalation arrangements and internal duties should be defined.
How can small businesses prepare for a cyber security incident?
Preparation involves documenting critical systems, assigning incident responsibilities, securing backups, recording contacts, and defining escalation steps. Regularly review the plan and test decision-making through realistic exercises to identify gaps early.
Does a small business need cyber security certification?
Certification can demonstrate that a small business has assessed security controls, but it does not remove risk. Select schemes relevant to customers, contracts, systems and regulatory obligations, and review periodically.
What cyber security training should small business staff receive?
Training should cover phishing recognition, password and authentication practices, safe data handling, device security, reporting procedures, and social engineering. Tailor exercises to staff roles, systems and likely business risks faced.
Discuss Your Small Business Cyber Security Needs
Discuss your small business cyber security requirements with S2 Technology Group to identify practical next steps for improving protection, clarifying priorities and aligning controls with your systems, users and business responsibilities. Contact the team to begin an informed review.