
Cyber Risk Assessment
A cyber risk assessment examines your organisation’s systems, data, users and controls to identify vulnerabilities and prioritise practical improvements. S2 Technology Group uses this assessment to inform proportionate cyber risk management and security decisions.
What a Cyber Risk Assessment Helps You Achieve
Following an assessment, the findings can guide decisions across your environment. Clear evidence helps you understand which weaknesses require attention, support proportionate investment, strengthen governance, and establish practical priorities for reducing exposure without treating every identified issue as equally urgent.
A ranked remediation plan
Findings can be organised by likelihood, potential business impact and the effectiveness of existing safeguards, creating a practical sequence for addressing the most significant risks first.
Clearer understanding of business exposure
The assessment connects technical weaknesses to systems, information and business activities, helping decision-makers understand what could be affected if a threat were successful.
Defined security responsibilities
Documented findings make it easier to assign ownership for actions across internal teams, suppliers and technology partners, reducing uncertainty about who must manage each risk.
More proportionate investment decisions
Evidence from the assessment supports decisions about security controls, infrastructure changes and user measures, helping direct resources towards areas with the greatest risk reduction potential.
Stronger governance evidence
A recorded assessment provides a structured basis for discussing cyber risk with leadership, reviewing controls and demonstrating that security decisions are being considered systematically.
A baseline for measuring progress
The findings establish a reference point against which completed actions, remaining weaknesses and changes in the organisation’s technology environment can be reviewed over time.
Straightforward Guidance from Your IT Partner
The human side of a cyber risk assessment is the interpretation applied to technical evidence. A scan may flag an outdated system or exposed account, but its significance depends on the information involved, how the system is used and what other safeguards are present.
That context comes from conversations with people who run your organisation. They explain operational constraints, supplier dependencies and the access staff need. Clear explanations help non-specialists understand why a control matters, what it changes and who owns it.
S2 Technology Group presents findings in plain language, separating confirmed issues from points needing further investigation. The aim is a useful discussion, not a document left unread: your organisation can question assumptions, consider workable options and relate cyber security to wider business priorities.
Specialist Cyber Risk Assessment and Management
A cyber risk assessment is most useful when it considers more than isolated technical weaknesses. S2 Technology Group examines how infrastructure, cloud services, endpoints, identities, data handling and business processes interact, creating a structured view of risk across the organisation rather than treating each system in isolation.
Its approach combines technical review with established risk management principles, including consideration of likelihood, business impact, existing controls and regulatory obligations. This supports a defensible assessment of cybersecurity risk and helps distinguish a genuine exposure from an issue that is already adequately managed by compensating safeguards.
Specialist cyber security assessment consulting also requires the experience to recognise dependencies that automated tools cannot establish alone. S2 Technology Group applies practical IT and security knowledge to assess the suitability of controls, the implications of business change and the maturity of governance, giving decision-makers a sound basis for managing cyber risk over time.
Questions to Ask About a Cyber Risk Assessment
What should trigger a new cyber risk assessment?
Ask whether findings are prioritised by business impact, likelihood and existing controls, then confirm how evidence is validated, documented and translated into owned, trackable remediation actions with clear review points.
Does a cyber risk assessment include third-party and supply-chain risks?
It should review suppliers, outsourced IT, cloud platforms and data-sharing arrangements, examining their access, assurance evidence, contractual responsibilities and incident dependencies. Residual third-party exposure then informs your organisation’s risk treatment.
What should a cyber risk assessment say about acceptable residual risk?
It should state which remaining risks the organisation accepts, why they are tolerable, who authorises that decision, any conditions attached, and when acceptance must be reconsidered after significant change.
How is assessment evidence protected during a cyber risk assessment?
Evidence should be collected through controlled methods, encrypted in transit and storage, restricted to authorised personnel, redacted where possible, and retained only as long as justified, with handling documented consistently.
What qualifications should a cyber risk assessor have?
A qualified assessor should combine recognised security knowledge with practical experience in governance, infrastructure and risk evaluation. Ask how they maintain competence, evidence independence and understand your sector context.
Contextual Assessment
S2 Technology Group combines technical evidence with business context, producing cyber risk assessments that translate complex findings into practical priorities.
Supporting Businesses Like Yours
Professional Services Organisations
Professional services organisations often manage confidential client information, shared documents and privileged user access. A cyber risk assessment can examine how these assets are protected, where access needs tightening and which security improvements should be prioritised.
Manufacturing Businesses
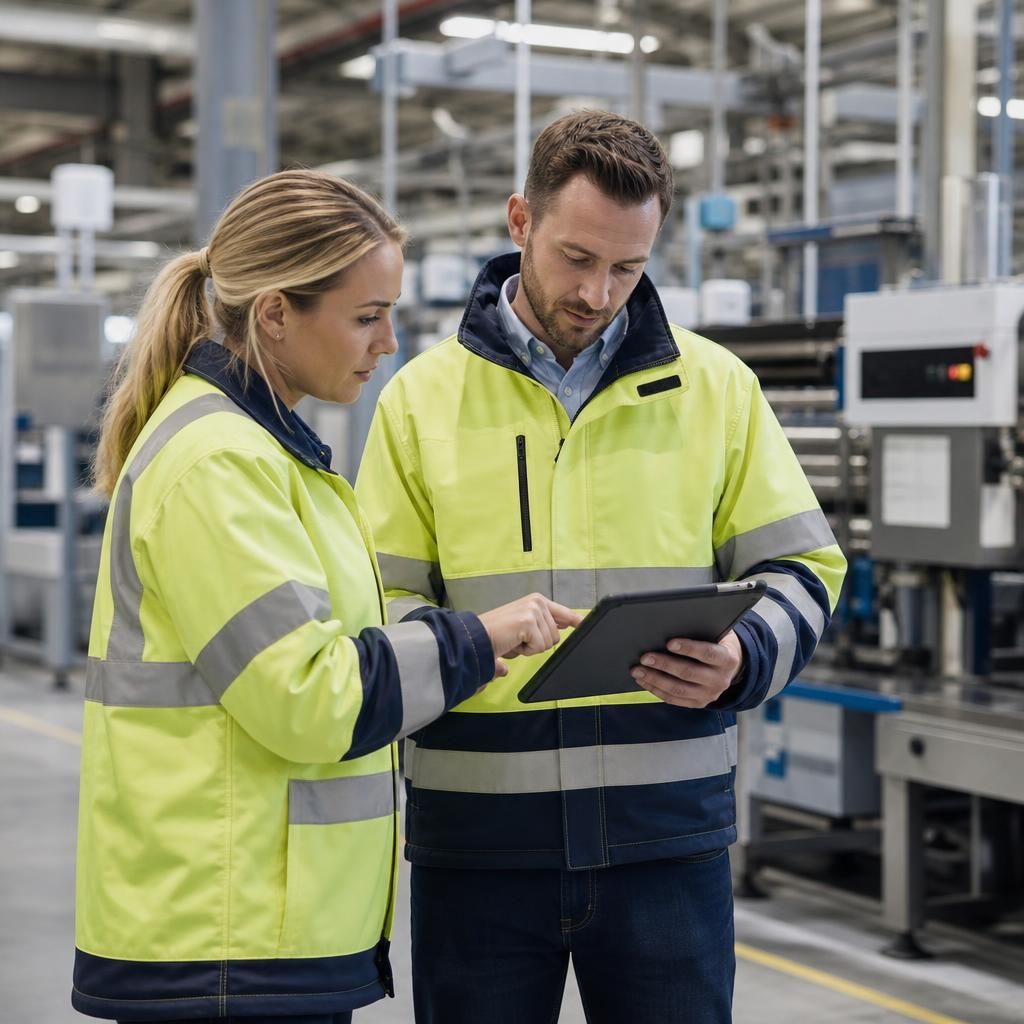
Manufacturers may depend on connected systems, specialist software and technology that supports production and administration. An assessment considers the security of these dependencies, including user permissions, network connections and the potential effect of disruption on operations.
Logistics Providers
Logistics businesses rely on systems that connect staff, suppliers, customers and operational information. Cyber risk assessment activity can identify weaknesses across accounts, devices, data flows and supplier access, helping clarify which controls require attention.
Multi-Site Organisations
Organisations operating across multiple premises must consider how locations, remote users and shared systems connect. A structured assessment can compare controls between sites, identify gaps in access management and support consistent cyber security priorities across the organisation.
When a Cyber Risk Assessment Is Useful
Cyber risk assessments can be shaped around specific changes or concerns, from preparing for a compliance review to evaluating a new cloud service. The following situations show when structured cyber security assessment and management may be useful.
During Business Growth
Adding staff, sites or business systems changes how people access information. A cyber risk assessment reviews those changes and helps identify which permissions, devices and controls need attention.
Before an Infrastructure Change
An assessment can provide a clear baseline before upgrading servers, moving workloads or changing network arrangements. It highlights weaknesses that should be addressed as part of the planned change.
When Suppliers Need Access
External providers may handle business data or connect to internal systems. Reviewing supplier access, dependencies and responsibilities helps clarify where third-party cyber risks sit.
After a Security Concern
A suspected phishing incident, unusual account activity or lost device may raise questions about wider exposure. A structured assessment helps examine relevant controls and separate known issues from areas requiring investigation.
To Prioritise Security Investment
When several security improvements are under consideration, an assessment links each issue to its likelihood, potential business impact and existing safeguards. This supports a more defensible order of work.
Cyber Risk Assessment: Frequently Asked Questions
How often should a cyber risk assessment be reviewed?
It reviews systems, data, users, access controls, vulnerabilities and business impact, then ranks findings by likelihood and consequence to guide proportionate remediation, governance and cyber risk management across your organisation.
What happens after a cyber risk assessment?
Findings are validated, documented and discussed with relevant stakeholders. An agreed action plan then assigns ownership, timescales and follow-up checks, while unresolved risks inform ongoing security governance and future reviews.
Can a cyber risk assessment cover remote workers?
Yes. It can examine remote endpoints, home-network connections, cloud applications and remote-access controls, including authentication, device protection and data handling, to identify risks outside the office and inform appropriate improvements.
How long does a cyber risk assessment take?
An assessment’s duration depends on its scope, system complexity, evidence availability and stakeholder access. S2 agrees the timescale beforehand, allowing focused reviews or broader assessments to be planned appropriately and realistically.
What is the difference between a cyber risk assessment and a penetration test?
A cyber risk assessment evaluates overall exposure, controls and business impact, whereas a penetration test actively simulates attacks against selected systems to verify whether specific vulnerabilities are exploitable in practice.