
How is outsourced IT introduced without disrupting existing business operations?
Outsourced IT is introduced without disruption by first assessing the existing environment, documenting dependencies and agreeing a staged transition plan with clear responsibilities. Changes can then be piloted, scheduled around operational needs, communicated to staff and supported by a rollback plan before wider implementation.
Outsourced IT is introduced with minimal disruption when the provider takes control of agreed responsibilities in a governed, traceable way rather than making unrestricted changes to the technology environment. The transition should preserve essential business services, establish clear authority for decisions and create reliable support processes before responsibility moves fully to the provider.
A practical introduction usually begins with a transition charter. This records what is being transferred, what remains with the organisation, who can approve changes and how disagreements or urgent decisions will be handled. It should identify business owners for key systems, technical contacts, suppliers and any internal staff whose responsibilities will change. Without this governance, an outsourced arrangement can create uncertainty even where the technical work is sound.
The provider should then establish controlled access to the systems needed to deliver the service. Access should be based on individual accounts, least-privilege permissions and multi-factor authentication where appropriate. Administrative credentials should not be shared casually or embedded in undocumented processes. A record of privileged access, approval routes and account removal procedures helps the organisation retain control during and after the transition.
Service management processes are equally important. Before the handover is complete, the organisation and provider should agree:
- how users report incidents and service requests;
- which issues are treated as security incidents or business-critical failures;
- who owns communication with staff, customers, suppliers and other affected parties;
- how requests requiring approval are identified;
- how recurring faults, root causes and unresolved risks are recorded; and
- how service performance and outstanding actions are reviewed.
These arrangements prevent employees from relying on informal contacts or sending technical problems to several teams at once. They also provide an auditable record of decisions, actions and ownership.
Special attention is needed for identity and access management. The provider should understand how employees join, change roles and leave the organisation, including how access to cloud services, remote access tools, shared files and line-of-business applications is granted or removed. A defined joiner, mover and leaver process reduces the risk of excessive permissions and avoids delays when responsibilities change.
Security controls should be confirmed as part of the operational handover, not treated as a separate exercise. This includes reviewing endpoint protection, patch management, backup arrangements, email security, logging, vulnerability handling and incident escalation. The organisation should know which controls are operated by the provider, which remain internal and which depend on another supplier. Where a control cannot be implemented immediately, it should be recorded with an owner and a planned treatment rather than being left as an informal assumption.
Data handling also requires explicit agreement. The parties should establish where business data is stored, who can access it, how it is transferred, how it is backed up and how it will be returned or deleted if the arrangement ends. These points may also affect contractual obligations, privacy requirements and sector-specific compliance. A provider should be able to explain its operating procedures in terms that the organisation’s management and compliance contacts can assess.
Operational continuity is best protected by separating essential services from lower-risk improvements. Core functions such as authentication, connectivity, file access, communications and critical applications should have known owners and documented recovery procedures. Non-essential upgrades or configuration changes should not be bundled into the transfer simply because they are technically convenient. Keeping the initial scope controlled makes it easier to identify whether an issue was caused by the handover or by a later improvement.
Users should receive practical guidance before the new support model becomes their normal route for assistance. This may include the service desk contact method, information to include in a request, approval rules and what to do if a device or account is suspected of being compromised. Managers should understand how business priorities are represented in support requests, while technical staff should know which decisions they can make without further authorisation.
After responsibility has moved, the arrangement should be reviewed against agreed service records rather than informal impressions. Useful evidence can include incident trends, unresolved problem records, change approvals, patch status, backup test results, access reviews and security events. Early reviews are an opportunity to correct unclear ownership and incomplete documentation before they become operational weaknesses.
For a small or medium-sized organisation, an outsourced IT provider such as S2 Technology Group can support this process by combining ongoing IT management with security, cloud, infrastructure and connectivity expertise. The important measure is not simply whether technical tasks have been transferred, but whether the organisation retains visibility, decision-making control and dependable operating procedures throughout the change.
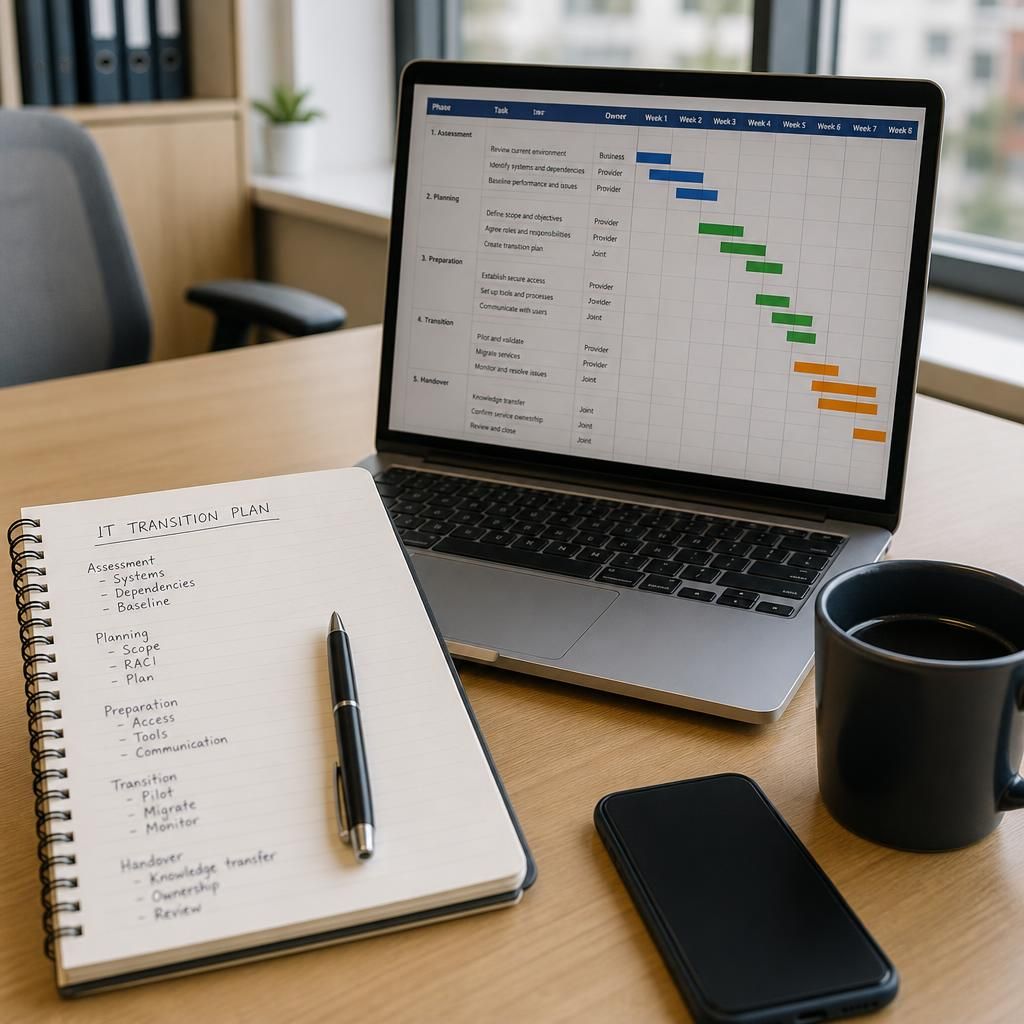
A reliable way to judge whether an outsourced IT transition is causing disruption is to establish a baseline before the handover begins. This should record normal service performance, recurring faults, open support requests, planned maintenance and any known limitations in the existing environment.
The baseline gives both parties a reference point for assessing the transition. For example, a rise in incidents can be examined against pre-existing problems rather than automatically attributed to the new provider. It also helps identify whether service quality has returned to normal after each transition stage.
Baseline information should be reviewed with the relevant business owners and retained with the transition records. Comparing it with post-handover trends supports objective decisions about outstanding work, additional investigation and whether the outsourced arrangement is operating as intended.