
How are security controls enforced across virtual IT environments?
Security controls in virtual IT environments are enforced through centrally managed access policies, network segmentation, encryption, secure configuration and continuous monitoring. These controls restrict who and what can access virtual resources, detect suspicious activity and help maintain consistent security across servers, applications and user devices.
Security controls in virtual IT environments are enforced through multiple technical and operational layers that govern how virtual machines, applications, identities and data are created, changed and used. Enforcement combines isolation within the virtualisation platform, hardened system builds, controlled administrative privileges, secure change processes, vulnerability remediation, endpoint protection and tested recovery procedures. No single control is sufficient on its own; the aim is to prevent unauthorised activity, limit the effect of a compromise and provide evidence that controls are operating as intended.
The virtualisation layer provides the first boundary. Each virtual machine is separated from others by the hypervisor, which controls access to allocated computing, memory, storage and virtual network resources. Permissions on the management plane determine who can create, delete, copy, resize or connect virtual machines. Administrative interfaces should not be exposed unnecessarily, and management access should be restricted to authorised personnel and approved administration devices. Separating management functions from ordinary user traffic reduces the risk that a compromised workload can be used to reach the platform that controls other workloads.
Isolation must also be checked for configuration weaknesses. Unused virtual hardware, legacy interfaces and unnecessary services can be removed from machine configurations. Snapshots, templates and cloned systems need the same protection as live workloads because they may contain credentials, business data or software configurations. When a virtual machine is decommissioned, its disks, snapshots and backup copies should be identified and handled according to the organisation’s retention and disposal requirements.
Identity controls determine whether a person or service is entitled to perform an action. Effective enforcement includes individual accounts rather than shared administrator credentials, multi-factor authentication for privileged operations, and separation between ordinary user rights and platform administration. Privileges should be assigned according to the tasks a role requires, with administrative rights granted for a defined purpose rather than as a permanent default. Service accounts also need named ownership, limited permissions, protected credentials and regular review.
Identity enforcement continues after an account is created. Joiners, movers and leavers processes should update permissions when responsibilities change, remove access when it is no longer required and identify dormant accounts. Privileged activity should be attributable to a specific person or service, so that changes to virtual infrastructure can be investigated accurately. Emergency accounts may be retained for recovery purposes, but they should be tightly controlled, monitored and tested rather than becoming an informal alternative to normal administration.
Standardised builds make security repeatable. Virtual machines can be deployed from approved templates containing supported operating systems, required security settings and only the software needed for their role. Templates should be maintained as controlled configuration items, not treated as permanent images. Before use, they should be updated, checked for unnecessary components and reviewed when the operating system, applications or security requirements change.
Configuration compliance tools can compare running workloads with the approved baseline. They may identify disabled protective features, open services, weak settings, unsupported software or changes made outside the normal process. Where appropriate, approved settings can be corrected automatically; higher-risk changes should be assessed before being applied to avoid disrupting a critical application. This approach prevents virtual machines gradually drifting away from their intended security state.
Patch and vulnerability management provide ongoing corrective enforcement. Operating systems, applications, hypervisors and management components all require a defined process for identifying weaknesses, assessing their relevance and applying fixes. The process should account for dependencies between virtual workloads, test updates where necessary and record exceptions when a patch cannot be applied immediately. An exception should have an owner, a reason, compensating safeguards and a review date rather than becoming an indefinite acceptance of risk.
Security controls also apply inside the virtual machine. Host-level separation does not protect an application from a vulnerable operating system, stolen credentials or malicious code running within that machine. Endpoint protection, application restrictions, secure administrative tools and controlled software installation can help enforce the intended behaviour of each workload. The appropriate controls depend on whether the machine hosts a database, a business application, a remote desktop service or another function.
Data controls govern how information is stored, moved and recovered. Permissions should be applied to virtual disks, shared storage, backup repositories and administrative exports as well as to the live application. Sensitive data may require additional safeguards, such as separate storage arrangements or stricter approval for copying and restoration. Backup copies should be protected from unauthorised alteration, and recovery access should not depend solely on the same credentials or systems that could be affected by an incident in the production environment.
Security enforcement also depends on controlled change management. Proposed changes to virtual networks, machine specifications, templates, privileged roles and security configurations should be documented, assessed and approved by an appropriate person. Automated deployment tools can improve consistency, but their code, credentials and execution permissions require protection themselves. A reliable process records what changed, who authorised it, when it was implemented and whether the resulting environment met the required baseline.
Logs and evidence support accountability and compliance. Events such as administrator sign-ins, privilege changes, virtual machine creation, configuration changes, failed authentication attempts and data restoration should be recorded in a form that is protected from unauthorised alteration. Records should use consistent time settings and be retained for a period appropriate to the organisation’s legal, contractual and investigative needs. Reviewing this evidence helps confirm that controls are functioning, while regular access and configuration reviews identify exceptions that automated tools may miss.
Incident response procedures define what happens when a control fails or suspicious activity is identified. Possible actions include isolating a workload, disabling a compromised account, preserving relevant evidence, restoring from a known-good backup and checking connected systems for related activity. These actions should be planned in advance because an incident may affect the management plane as well as individual virtual machines. Exercises and recovery tests can expose gaps in permissions, dependencies and administrative access before a real event occurs.
A practical control framework therefore uses three types of safeguard:
- Preventive controls: isolation, authentication, least-privilege administration, secure templates, patching and restrictions on unauthorised changes.
- Detective controls: configuration checks, vulnerability assessment, event records, access reviews and identification of unusual administrative activity.
- Corrective controls: account suspension, workload isolation, remediation of weaknesses, controlled restoration and changes to prevent recurrence.
For a business assessing a virtual IT environment, the key question is not simply whether security software is installed. It is whether each control has a defined owner, is applied consistently across relevant workloads, produces usable evidence and is tested when the environment changes. A managed IT provider can support this by documenting the virtual architecture, agreeing control requirements, reviewing exceptions and maintaining the operational processes that keep those controls effective as systems, users and business needs evolve.
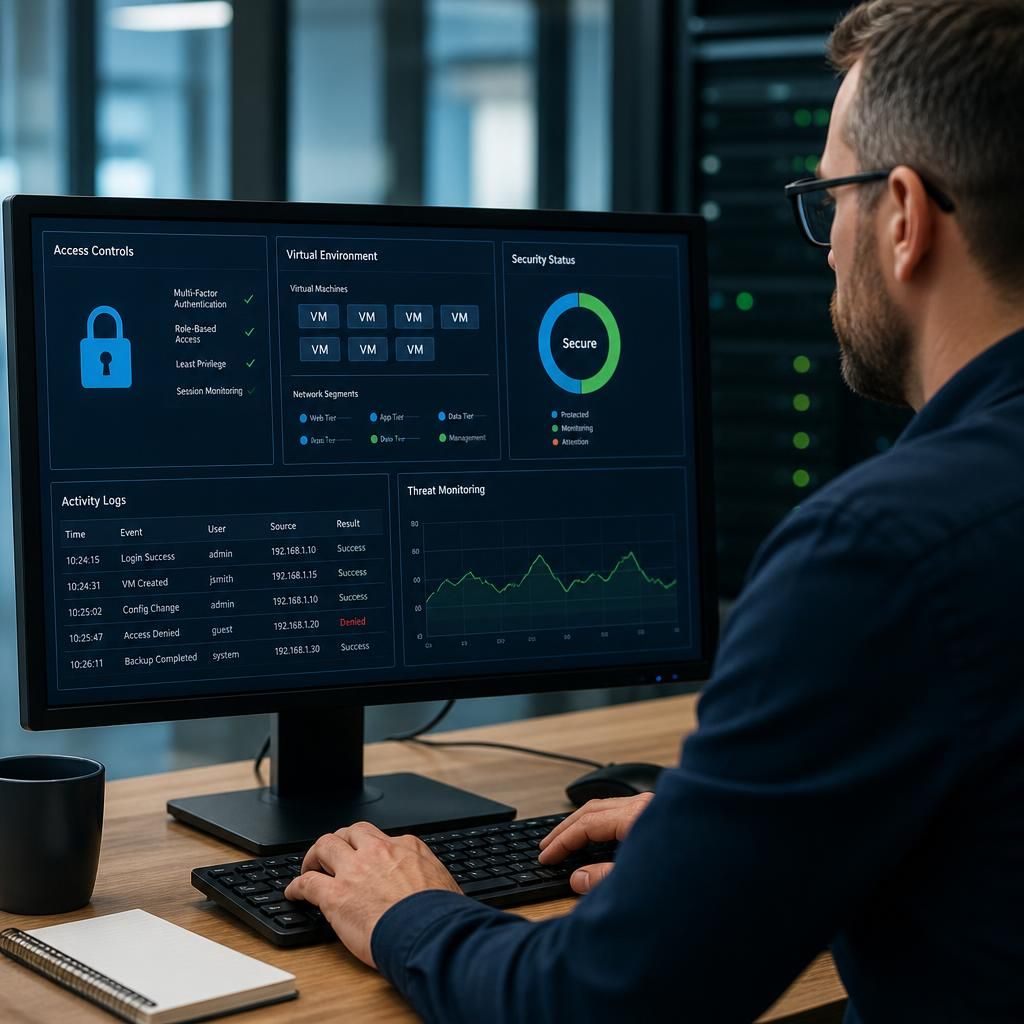
Security controls in a virtual IT environment are enforced through clearly assigned responsibilities as well as technical safeguards. A responsibility matrix should identify whether the organisation, its IT provider or the underlying hosting platform is accountable for each control, such as physical infrastructure protection, hypervisor security, virtual machine configuration, identity management, application security and data handling.
This distinction prevents gaps between service boundaries. For example, a hosting provider may secure the physical servers and virtualisation platform, while the organisation or its IT partner remains responsible for user permissions, operating system settings and application access. The matrix should state how each responsibility is performed, what evidence is produced and who reviews exceptions. It should also be updated when workloads move, suppliers change or the virtual architecture is redesigned.
Defined escalation routes reinforce enforcement. If monitoring identifies a control failure, the responsible party must be identifiable, with agreed procedures for investigation, corrective action and confirmation that the issue has been resolved. This makes security ownership visible across the environment instead of assuming that one party automatically protects every layer.