How is IT Infrastructure as a Service implemented?
IT Infrastructure as a Service is implemented through a structured process of assessing current systems, designing the required cloud-based infrastructure, and planning migration with minimal disruption. The provider then configures and tests the environment, moves agreed workloads and data, establishes access and security controls, and provides ongoing monitoring, maintenance and support.
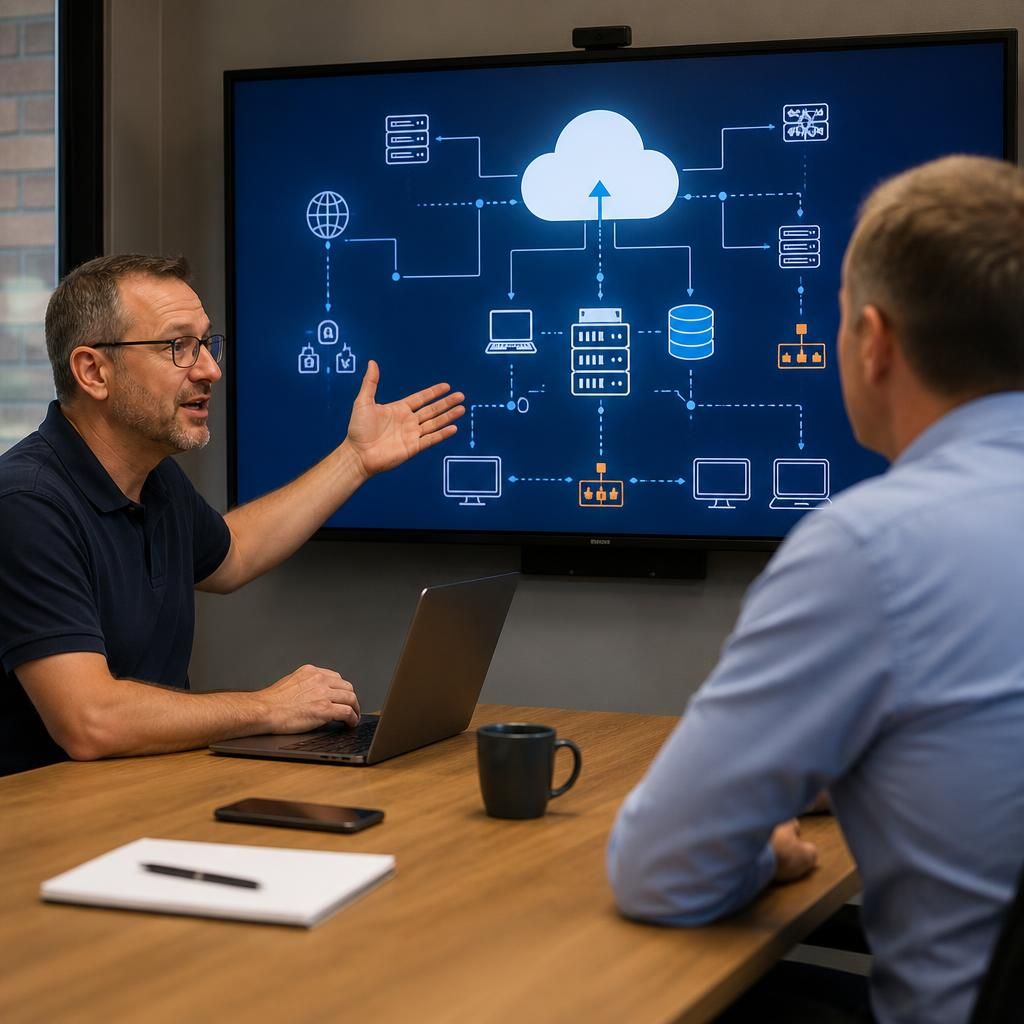
Implementing IT Infrastructure as a Service involves translating business requirements into a managed technology environment, assigning responsibilities between the provider and the customer, and introducing the new infrastructure in controlled stages. The technical deployment is only one part of the process; successful implementation also depends on governance, access design, workload dependencies, user requirements and clear operational procedures.
1. Establish the business and technical requirements
The starting point is to define what the infrastructure must support. This includes business applications, file storage, databases, communications systems, remote access, printing, user devices and any operational technology connected to the network. Requirements should also cover data location, regulatory obligations, performance expectations, resilience needs and the level of control the organisation wishes to retain.
It is useful to identify which systems are business-critical and which can tolerate planned maintenance or temporary reduced functionality. Documenting these priorities helps determine the appropriate architecture and provides a basis for deciding how workloads should be introduced.
2. Create the service design
The provider converts the requirements into a service design covering compute capacity, storage, networking, identity, backup dependencies and administrative access. The design should explain how environments will be separated, how systems will communicate, and how capacity can be adjusted as requirements change.
Identity and permissions require particular attention. Users, administrators, service accounts and third parties should receive only the access needed for their roles. The design should also define how accounts are created, changed and removed, and how privileged activity is controlled and recorded.
Connectivity is considered alongside the hosted infrastructure. Offices, remote users and site-to-site connections may require different access arrangements, particularly for organisations with multiple locations or users working from different networks. Addressing these dependencies before deployment reduces the risk of an environment that is technically available but difficult for people or applications to use.
3. Prepare the implementation plan
A practical plan sets out activities, dependencies, responsibilities, approval points and rollback options. It should identify which information must be supplied by the customer, which tasks are performed by the provider, and who authorises changes to production systems.
Workloads are commonly grouped into implementation waves according to their dependencies and business importance. A supporting service may need to be established before an application that relies on it. Where systems exchange data, integrations, authentication methods and scheduled tasks should be recorded so that moving one component does not unintentionally disrupt another.
The plan should include user communications and a route for dealing with issues discovered after each change. This makes implementation a controlled change programme rather than a single unstructured cutover.
4. Build and validate the environment
The infrastructure is created according to the approved design, with configuration applied consistently across the relevant environments. Technical validation should cover connectivity, authentication, permissions, storage access, application dependencies and administrative functions.
Testing should reflect real business use rather than checking only whether individual components start. For example, a user may need to authenticate, access a shared resource, use an application and connect from an approved remote location. Administrative testing should confirm that changes can be made safely and that important events are visible to the people responsible for managing the service.
Where appropriate, a separate test or staging environment can be used to validate updates before they affect production workloads. Acceptance criteria should be agreed in advance so that the organisation can make an informed decision about whether each implementation stage is ready to proceed.
5. Transfer workloads and users in controlled stages
Migration activities should account for data consistency, application configuration, permissions and the point at which users switch to the new environment. Data may need to be synchronised more than once so that the final transition contains the latest approved information.
After each workload is introduced, the provider and customer should check application behaviour, user access, integrations and business processes. Issues can then be isolated to a defined change rather than being mixed with several simultaneous alterations. A documented rollback approach is important where a failed transition could affect essential operations.
6. Complete operational handover
Implementation is not complete when the infrastructure is technically running. The handover should provide an accurate record of the environment, including network arrangements, system dependencies, user and administrator roles, support procedures, backup responsibilities, change controls and escalation routes.
Staff who administer or use the systems may need guidance on new login methods, remote access, file locations, security controls or request procedures. Any temporary implementation accounts, test data and unused access paths should be removed or reviewed before the service moves into normal operation.
7. Review the service after deployment
A post-implementation review checks whether the delivered environment meets the original requirements and whether any assumptions proved incorrect. Capacity, access rights, performance, costs, support requests and user feedback can be examined to identify adjustments.
IT Infrastructure as a Service is therefore implemented as an ongoing service lifecycle. Requirements and risks change as the organisation grows, adds applications, opens locations or changes working practices. Regular reviews allow the infrastructure design, permissions and operating procedures to remain aligned with the business rather than treating the initial deployment as a permanent final state.
The implementation method should match the organisation’s risk profile, workload dependencies and tolerance for change. A pilot can introduce the service to a limited group of users or a non-critical workload first, allowing configuration and support procedures to be evaluated before wider adoption.
A phased migration is suitable where applications or locations can be separated into logical groups. It limits the scope of each change and makes it easier to identify the source of any issue. A parallel arrangement may be appropriate for particularly important systems, with the existing and new environments operated together while results are compared. In contrast, a single cutover is only appropriate when dependencies are well understood and the transition can be completed and tested as one coordinated change.
The chosen approach should be documented in the implementation plan, including the decision criteria for progressing, pausing or reverting each stage. This connects the technical migration method with business risk rather than treating deployment as a purely infrastructure-led decision.