How does Intune manage Windows update policies?
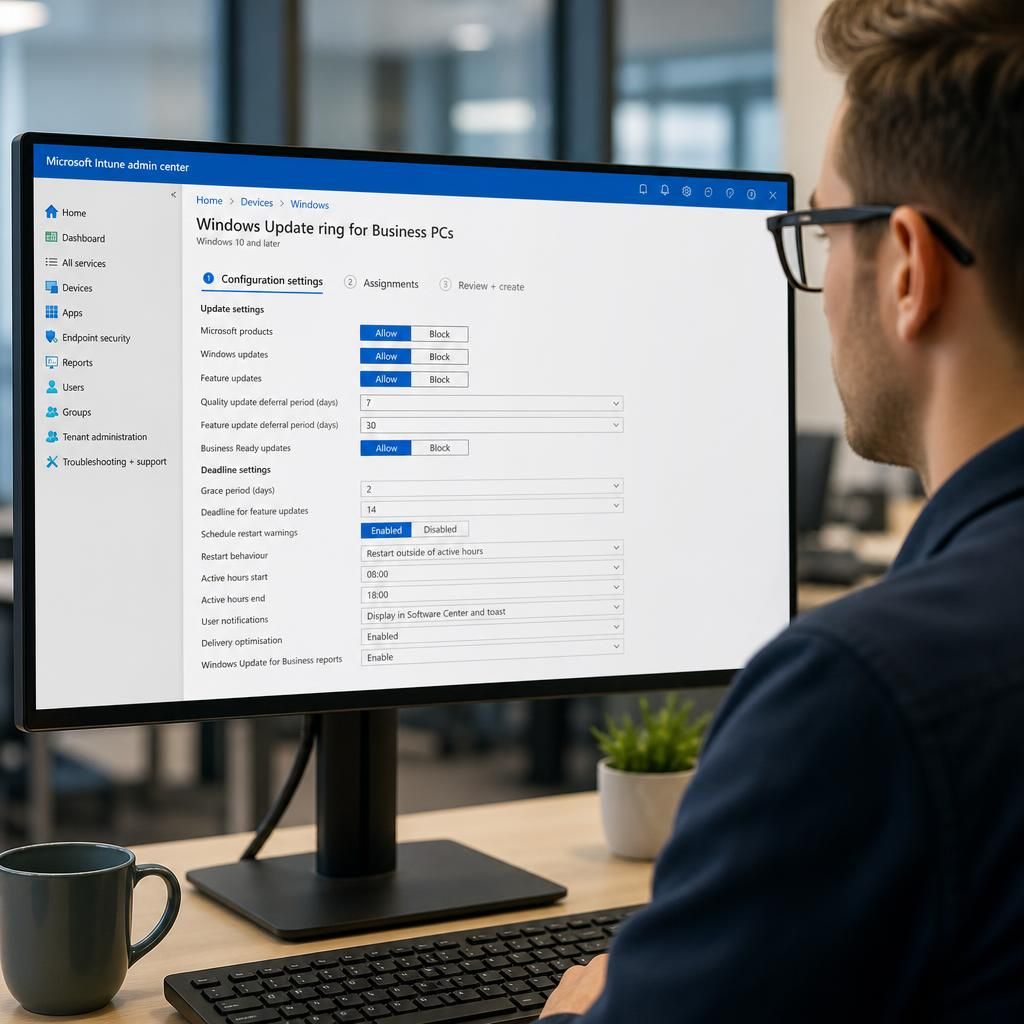
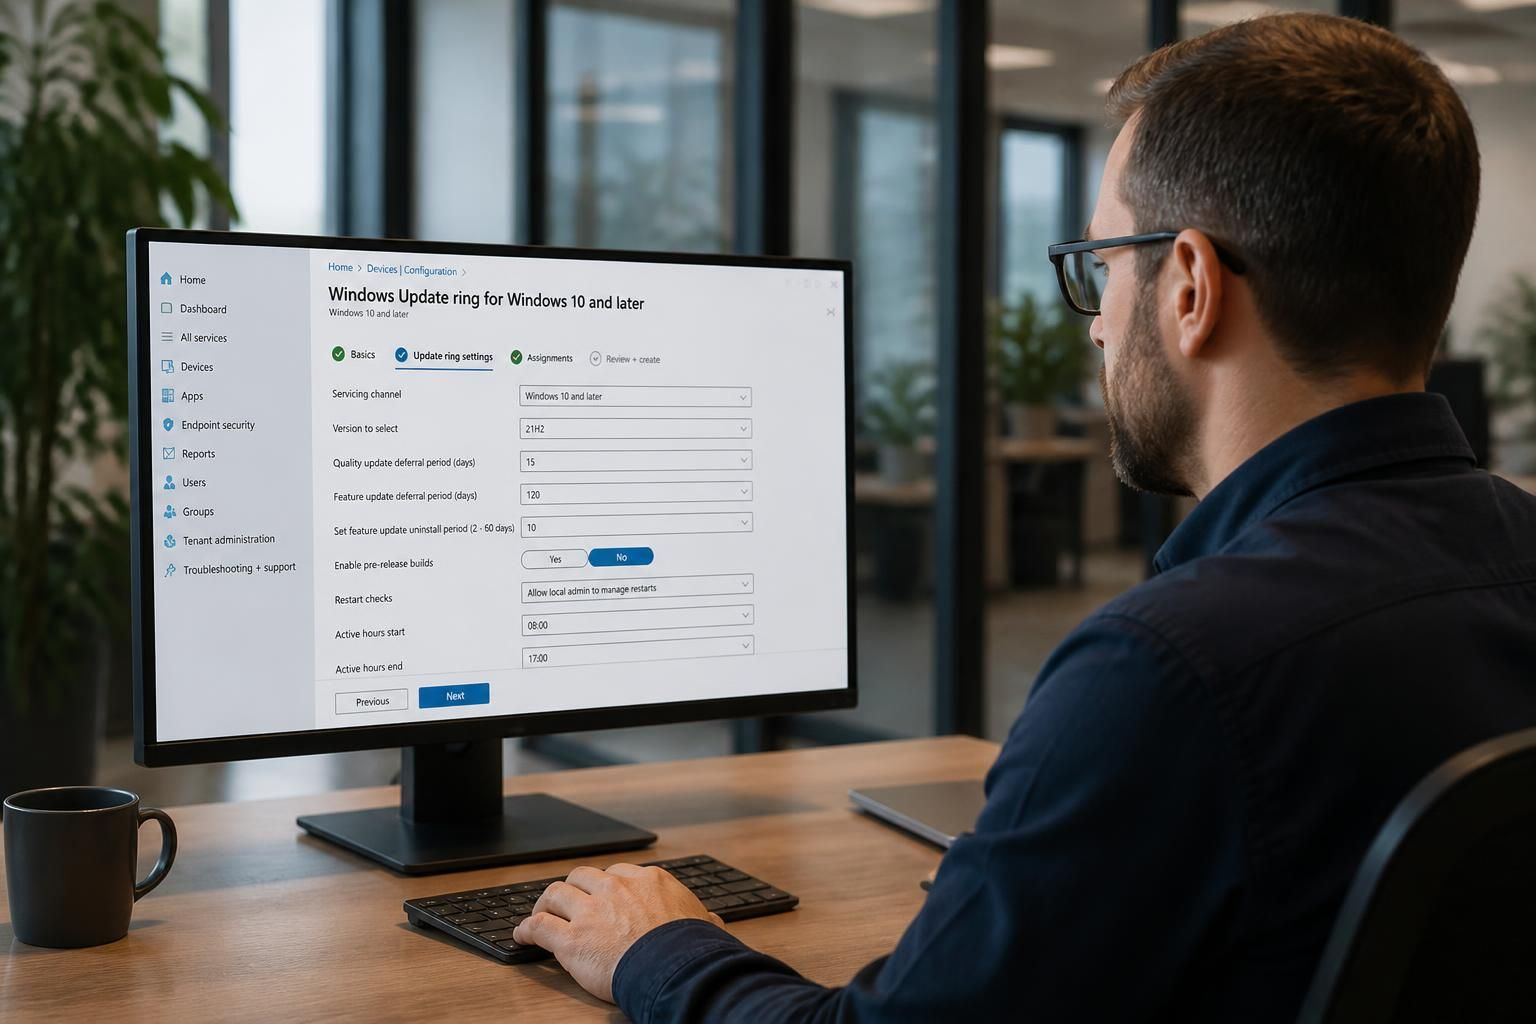
Microsoft Intune manages Windows update policies by configuring update rings and deployment settings for groups of devices. Administrators can control update types, deferrals, deadlines, restart behaviour and feature-version targeting, allowing updates to be tested and released in stages while maintaining device security.
Intune manages Windows update policies by acting as the central control layer for update configuration, targeting and monitoring. It sends policy settings to enrolled devices, while the Windows update service on each device evaluates applicability, downloads approved content and applies it according to the rules assigned to that device. Intune therefore governs how updates are handled rather than serving as the update file repository itself.
Effective management depends on using the right policy type for the decision being made. An update ring provides the device-level operating rules, such as how a device participates in servicing and what it should do when an update requires user action. Separate feature update policies can be used to keep compatible devices on a specified Windows release, which is useful where an application, driver or line-of-business system has not yet been validated against a newer release.
Quality update policies address the servicing cadence for cumulative security and reliability fixes. They can also support the controlled acceleration of an important update where delaying installation would create unnecessary risk. Driver update policies provide another layer of control, allowing organisations to decide whether drivers are managed through the same update process or handled through a separately governed approval approach.
- Update rings: establish the general servicing behaviour for a device group.
- Feature update policies: keep devices on an approved feature version until a planned change is authorised.
- Quality update policies: govern the treatment of cumulative servicing releases and urgent deployment requirements.
- Driver policies: provide additional oversight of driver updates where hardware compatibility needs specific testing.
Assignments are an important part of policy design. An administrator can assign a policy to groups of users or devices, use exclusions for exceptions, and apply filters where the available device attributes justify more precise targeting. The assignment model should reflect ownership and risk: a test population may have different rules from standard users, while specialist equipment may need its own policy because it supports software or hardware with stricter compatibility requirements.
Policy conflicts need to be considered before deployment. If multiple policies configure the same setting, the resulting behaviour may not be obvious from the individual policy pages. A clear baseline, limited overlapping assignments and documented exceptions make the outcome easier to predict. Device scope is also significant: a user-targeted policy can follow the user across devices, whereas a device-targeted policy remains tied to the hardware. Choosing the wrong scope can produce inconsistent results when people use shared or replacement devices.
Intune can also control how a device responds when Windows requires a restart. The policy can be designed to give users appropriate notice, define when a restart becomes compulsory and specify how restart prompts are handled. These settings should be assessed alongside the working pattern of the organisation. A policy that is technically secure but repeatedly interrupts production activity may lead users to postpone actions or seek workarounds, reducing the value of central management.
Feature version control is particularly useful for change management. Instead of allowing every compatible device to move to the newest release as soon as it becomes available, an organisation can validate the release against its applications, security tools, peripherals and business processes first. Once testing is complete, the feature update policy can be changed or removed in accordance with the organisation’s release plan. Version control should not become a reason to defer security servicing indefinitely; feature stability and security maintenance are separate decisions.
Intune also accounts for situations in which an update cannot safely be installed. Windows may place a safeguard hold on a device where a known compatibility issue exists. Administrators should investigate the underlying condition rather than attempting to force the update without assessment. Hardware readiness, disk space, connectivity, servicing health and application compatibility can all affect the result. A failed installation is therefore not always evidence that the Intune policy is incorrect.
Monitoring completes the policy cycle. Intune reporting can show whether devices have received the relevant configuration, whether an update is pending or installed, and which devices have reported an error or remain outside the expected state. These reports should be reviewed by release group and device type rather than only as a single organisation-wide total. A small number of failed devices may represent a common hardware or application issue that requires remediation before wider deployment.
- Define the Windows versions and servicing approach that the organisation supports.
- Build a baseline update ring and create separate policies only where a genuine operational requirement exists.
- Validate feature releases, cumulative updates and drivers on representative devices.
- Use assignments, exclusions and filters to keep specialist or exceptional devices within an appropriate policy scope.
- Review policy conflicts and confirm the resulting settings on test devices.
- Monitor installation status, errors, safeguard holds and non-compliant devices.
- Investigate recurring failures and update the deployment design when the device estate or business applications change.
In practice, Intune works best when Windows update policies are treated as part of an ongoing endpoint governance process rather than as a one-off configuration. The policies define the intended behaviour, assignments determine who receives it, and reporting provides the evidence needed to correct exceptions. This combination gives administrators a structured way to balance security maintenance, compatibility and operational control across managed Windows devices.
An Intune assignment does not mean that Windows has installed an update immediately. It means the device has received the intended rules; Windows still assesses whether the update applies and whether installation conditions are met. A device may therefore show as policy-compliant while an update remains pending because it has not yet completed its local evaluation, download or installation process.
This distinction is useful when reviewing update status. Check policy delivery separately from update state, then examine device conditions such as connectivity, available storage, power and servicing health. Treating these as separate stages helps identify whether a problem lies with Intune configuration, device eligibility or the Windows update process itself, rather than changing a policy without understanding the cause.