
Who retains responsibility for Microsoft 365 support decisions?
The business retains ultimate responsibility for Microsoft 365 support decisions, including risk acceptance, policy, budget and compliance. Its IT team or managed IT provider can assess issues, recommend actions and manage approved changes, while business leaders remain accountable for the decisions that affect users and operations.
Responsibility for Microsoft 365 support decisions should be assigned through a clear governance model rather than left to whoever receives a support request. Business leaders set the organisation’s acceptable level of risk and operational priorities; designated technology decision-makers translate those priorities into technical requirements; and internal IT staff or a managed IT provider investigate, advise and carry out authorised work.
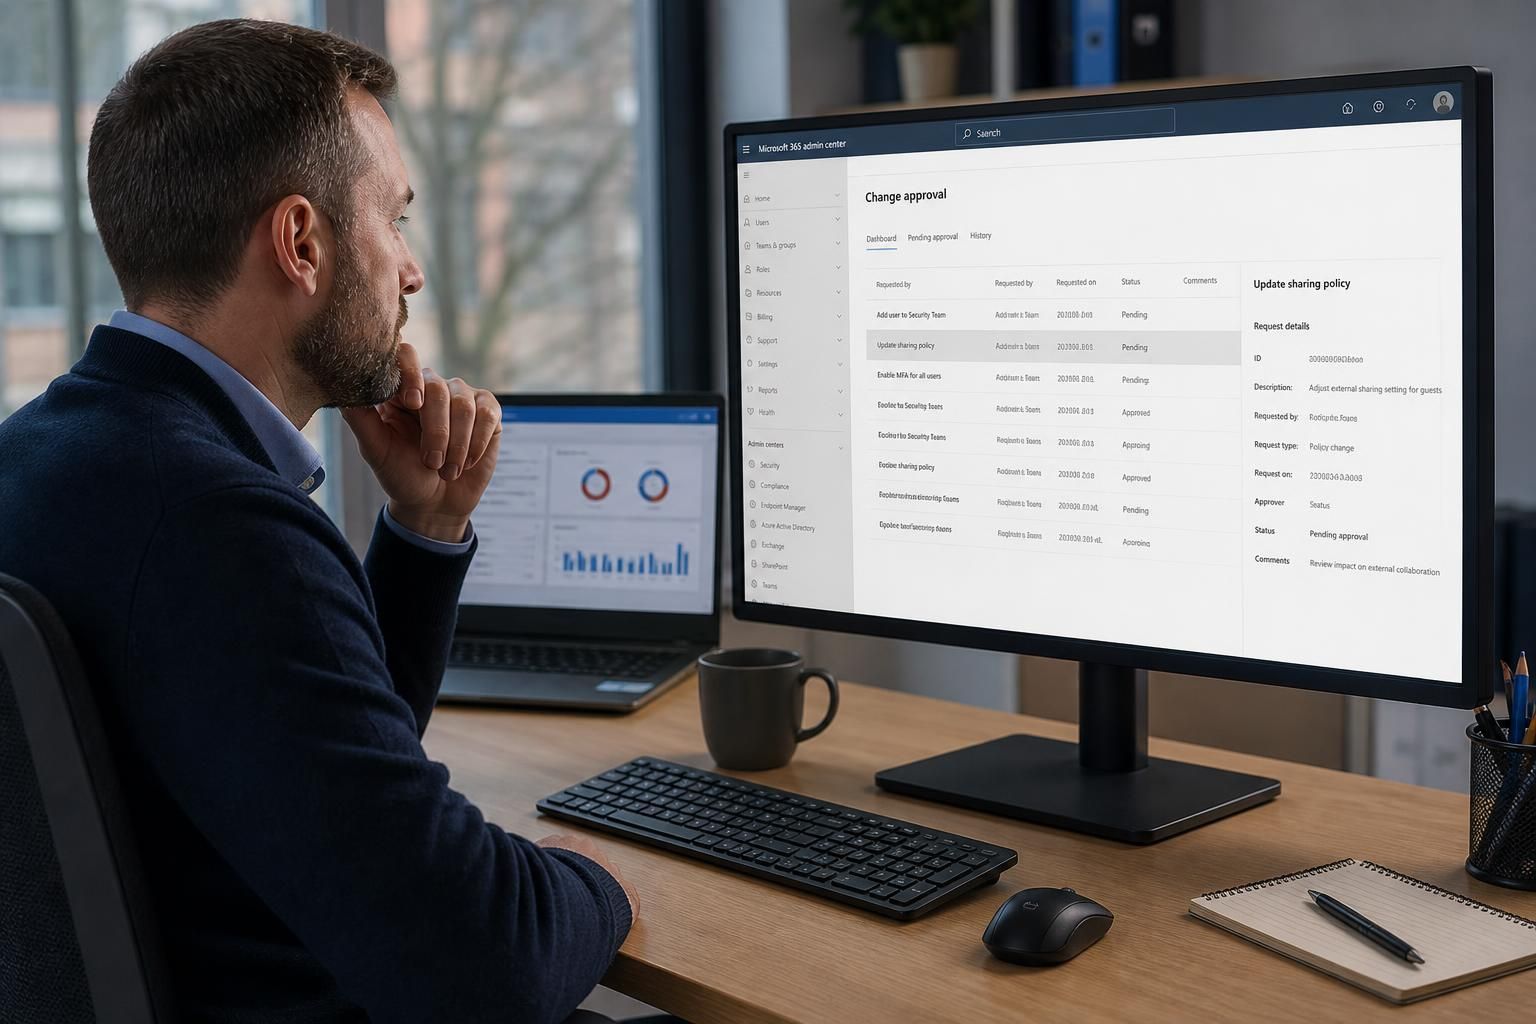
The person approving a change does not need to be the person who implements it. Separating these roles helps prevent informal changes to identity, security, email or collaboration settings. A practical decision structure normally identifies:
- Business owners: confirm how a service supports business processes, approve material risk and decide which operational disruption is acceptable.
- Data or process owners: define requirements for information handling, access, retention and collaboration within their area.
- IT decision-makers: assess technical dependencies, security implications, licensing requirements and compatibility with the existing environment.
- Microsoft 365 administrators or support providers: investigate incidents, propose solutions, document technical effects and apply approved changes.
- Users and department managers: report issues accurately and confirm whether a change has resolved a genuine business need.
Authority should match the potential impact of the decision. A routine adjustment to a user’s membership may follow an established procedure, whereas a change affecting authentication, administrator access, mail flow, external sharing or data governance should require documented approval from an appropriately authorised person. Delegated permissions should also have defined limits, so that technical access does not automatically become authority to accept business risk.
For each significant decision, the record should explain the issue, the options considered, the recommendation, the approver, the implementation owner and any review date. It should also note affected users, dependencies, expected service effects, security considerations and the method for reversing the change. This gives the business a reliable basis for checking whether a decision remains suitable as its workforce, applications or compliance obligations change.
Support teams should provide evidence rather than make unexamined assumptions. That may include audit information, configuration comparisons, sign-in details, service health information, licensing data and test results. Where the available evidence is incomplete, the recommendation should state the uncertainty and identify what needs to be verified before action is taken.
Escalation is appropriate when a request involves conflicting priorities, unusual security risk, uncertain ownership or a decision that affects several departments. The escalation route should be agreed in advance and should identify who can approve emergency action, who must be informed afterwards and how the change will be reviewed. An urgent technical problem does not remove the need to record who authorised the response.
A managed IT provider can improve the quality and consistency of these decisions by maintaining procedures, reviewing configurations, explaining consequences in business terms and keeping an auditable record of support activity. The provider should not silently make policy choices on the organisation’s behalf. The business must ensure that the right people are named, that delegated authority is current and that support recommendations are assessed against business requirements.
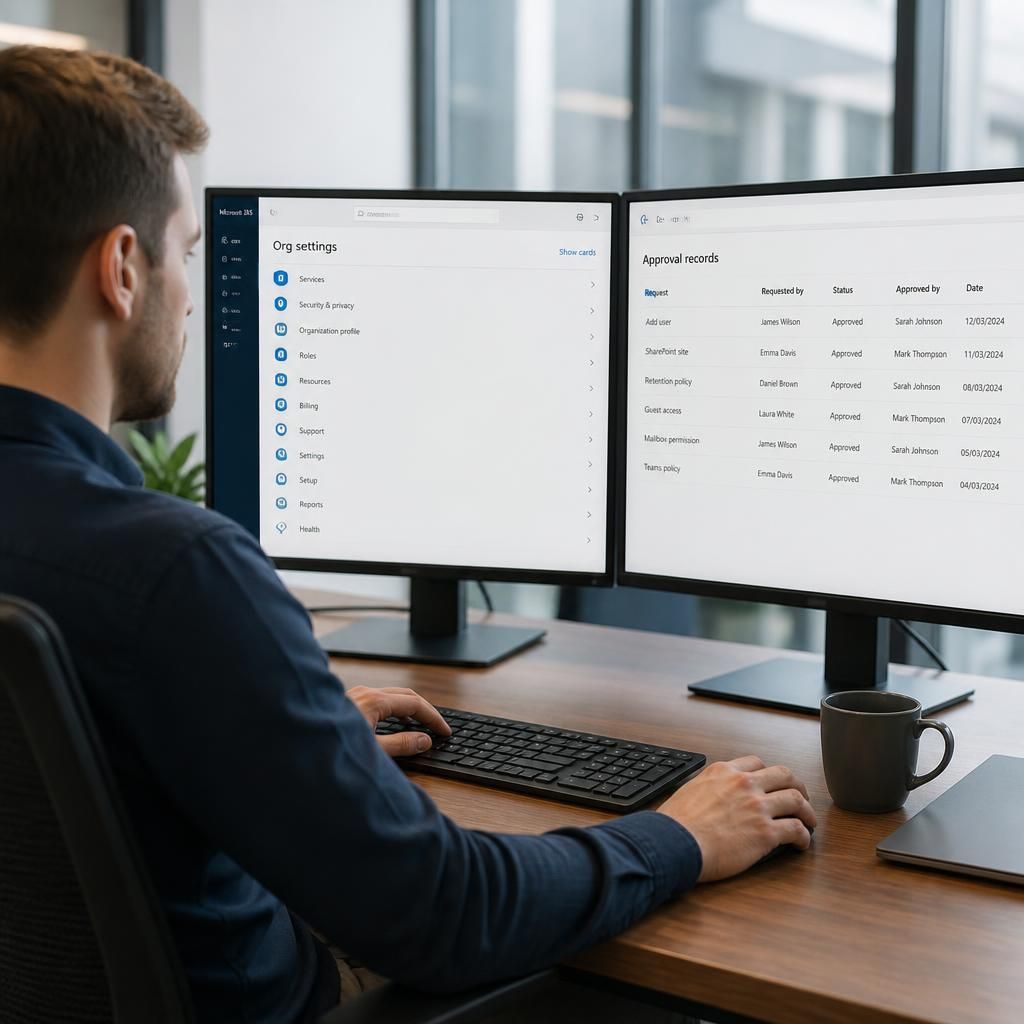
Microsoft 365 support decisions also depend on which part of the service is being changed. Microsoft is responsible for operating the underlying cloud service, while the customer organisation remains responsible for how its tenant is configured, how accounts and data are managed, and which business policies apply. A managed IT provider may administer those settings under an agreed delegation, but that delegation does not transfer the organisation’s accountability for its choices.
This distinction is important when reviewing a support recommendation. A service incident may need to be raised with Microsoft, whereas an access rule, retention setting or sharing decision requires the organisation to determine what is appropriate for its users and information. Support documentation should therefore identify whether an issue relates to the Microsoft service, the tenant configuration, a connected application or an internal business process. That classification makes it clearer who must investigate, who can approve the response and who remains responsible for the resulting decision.