
How can Microsoft 365 support improve email service reliability?
Microsoft 365 support improves email reliability by monitoring service health, reviewing configuration and security controls, and resolving delivery, access and synchronisation issues systematically. Regular checks can identify causes such as incorrect settings, account problems, compromised credentials or connectivity faults before they disrupt business communication.
Microsoft 365 support improves email reliability by maintaining the full mail system rather than treating each message problem as an isolated user fault. This includes mail-flow design, domain records, identity controls, mailbox configuration, client connectivity, change management and documented recovery procedures.
Reliable mail flow starts with the right technical foundations. Support should check that accepted domains, DNS records and mail-routing connectors reflect the organisation’s current structure. Records such as SPF, DKIM and DMARC need to be aligned with the systems authorised to send messages on the organisation’s behalf. Poorly maintained records can contribute to rejected messages, spam filtering or failed delivery when third-party applications send invoices, alerts or marketing communications.
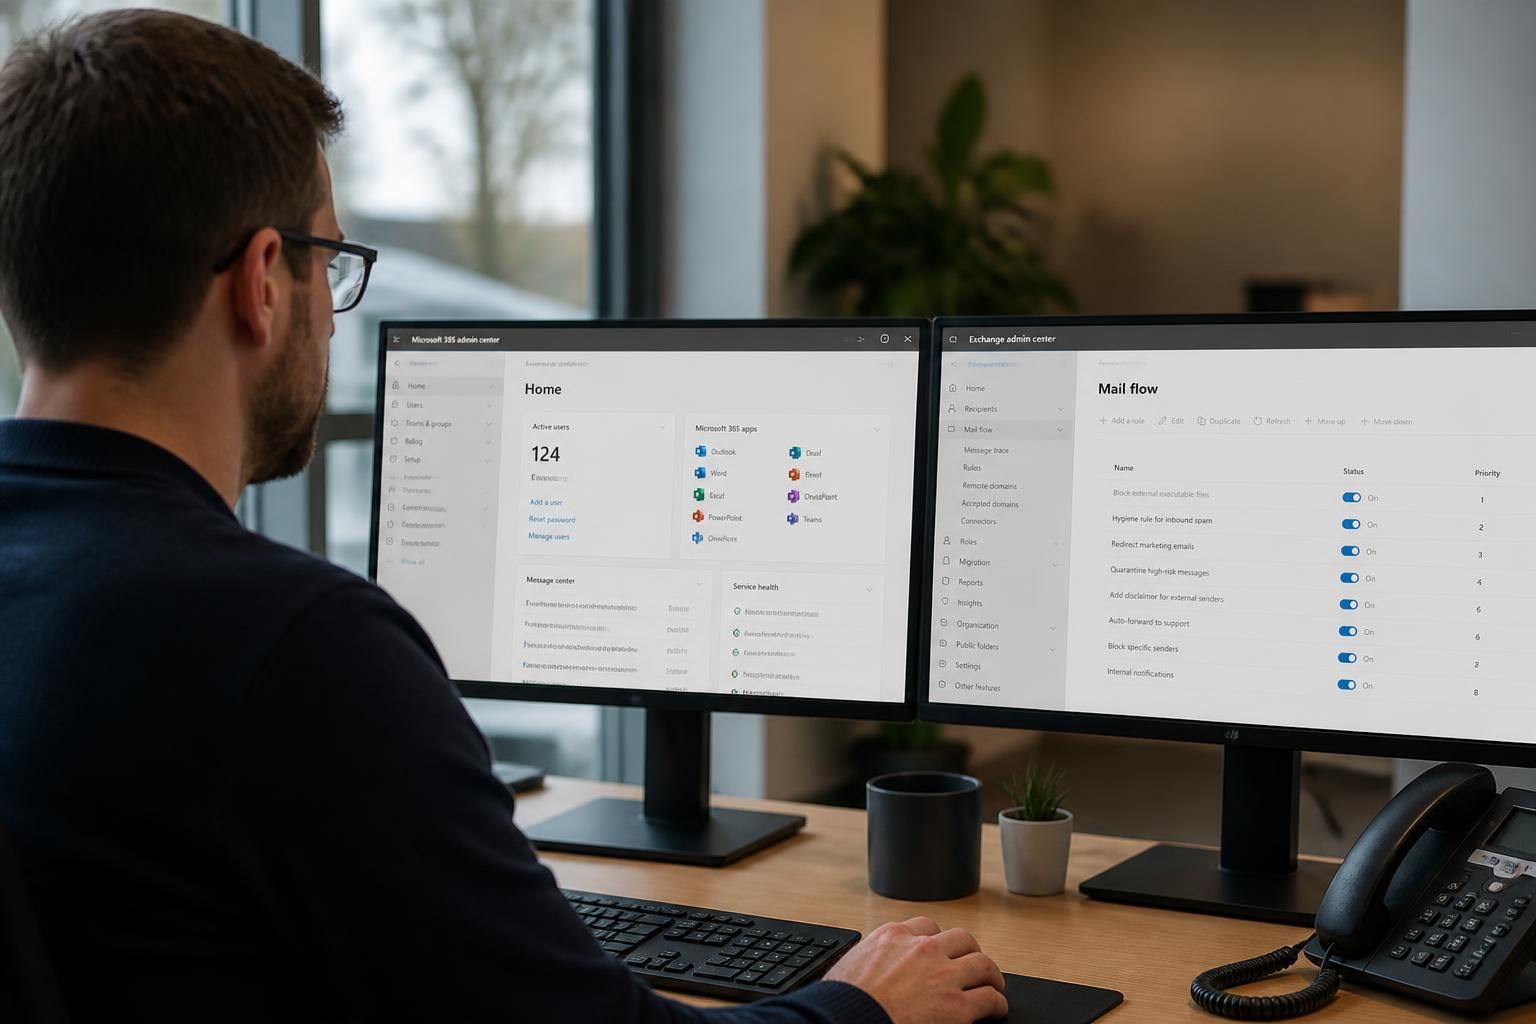
Mail-flow rules also require control. Rules that redirect, block, quarantine or modify messages should have a clear purpose and owner. Redundant or conflicting rules can create unexpected results, particularly after a department, domain or external service changes. A support process should keep an inventory of important rules and review whether they are still required before making amendments.
Identity management is another important part of email dependability. Sign-in failures, expired credentials, incorrect authentication methods and poorly managed shared mailboxes can prevent users from accessing otherwise healthy mailboxes. Support should apply consistent policies to user, shared and service accounts, while ensuring that former employees’ access, forwarding settings and delegated permissions are removed through a controlled offboarding process.
Mailbox permissions deserve particular attention. Full access, send-as and send-on-behalf permissions should be assigned to defined roles rather than left with individual users after responsibilities change. Reviewing these permissions reduces confusion over who can send from a shared address and makes delivery investigations easier to trace.
Support should separate Microsoft 365 service faults from local problems. A structured investigation can compare the scope and timing of the issue:
- whether one user, a department or the whole organisation is affected;
- whether messages fail when sending, receiving or both;
- whether the problem occurs in Outlook, webmail or a mobile client;
- whether messages are rejected, delayed, quarantined or simply absent; and
- whether the issue affects internal messages, external recipients or a particular domain.
This distinction prevents unnecessary changes to tenant settings when the underlying cause is a local profile, device, network path or recipient-side filtering policy. Message traces, non-delivery reports and audit information can then be used to establish what happened rather than relying only on a user’s description of the symptom.
Client and connectivity management also affects perceived reliability. Outlook profiles, cached mailbox data, mobile access and web browser sessions can each fail independently of the hosted mailbox. Support can use standard configuration guidance and repeatable troubleshooting steps to identify whether a client is synchronising correctly, whether an account is repeatedly prompting for authentication, or whether a damaged profile is creating duplicate or missing messages.
Change control helps prevent avoidable disruption. Before altering a mail-flow rule, authentication policy, domain setting or mailbox permission, support should record the proposed change, its reason, affected users and a reversal method. Changes should be tested against representative sending and receiving scenarios, including internal mail, external mail, shared addresses and messages from business applications. The outcome should be recorded so future investigations do not begin with an uncertain configuration.
Reliable email also depends on clear handling of incidents. A useful process records the initial symptoms, affected accounts, relevant message identifiers, actions taken and final cause. Recurring issues should be grouped and analysed rather than closed as separate tickets. For example, repeated delivery failures from one application may indicate a sender authentication or connector problem, while repeated access faults for one user may indicate an account or device issue.
Support should also define what can be recovered and how. This may include retaining relevant mail-flow evidence, documenting important mailbox and permission settings, and confirming how messages or access would be restored after an accidental deletion, configuration error or security event. Retention and recovery decisions need to reflect the organisation’s legal, operational and data-protection requirements rather than assuming that every deleted item is recoverable indefinitely.
For a business, the practical benefit is a more predictable email service: configuration is understood, faults are investigated consistently, changes are controlled and recurring causes are addressed. Microsoft 365 support therefore contributes to reliability through ongoing administration and sound operational processes, not simply by fixing Outlook when an individual user reports a problem.
Protecting outbound email activity is also part of reliability. A compromised Microsoft 365 account can send large volumes of unwanted mail, trigger delivery restrictions or damage the organisation’s sender reputation. Support should therefore review unusual sending patterns, unexpected forwarding activity and suspicious sign-ins as part of routine administration.
When abnormal activity is detected, the account can be contained while support investigates the cause, removes unauthorised access and checks that no malicious rules or applications remain. Reviewing the affected messages and confirming that normal sending has resumed helps distinguish a security incident from an ordinary delivery fault. This approach reduces the risk that one compromised mailbox disrupts communication for the wider organisation.