
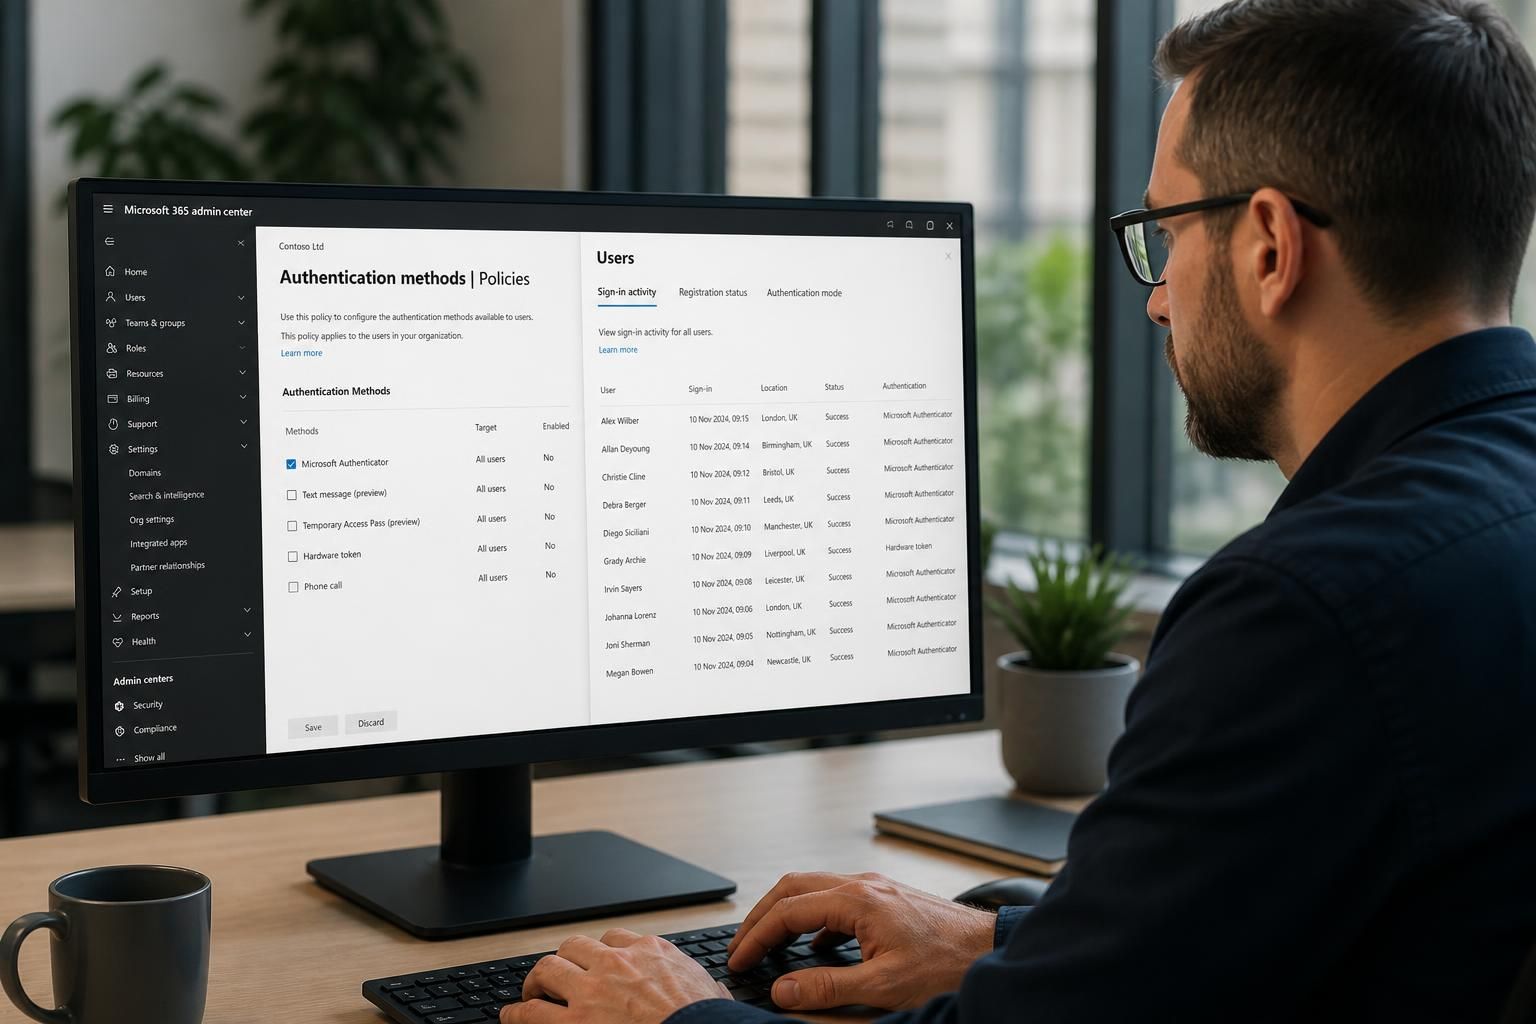
Does Microsoft 365 security training cover multi-factor authentication administration?
Yes. Microsoft 365 security training can cover multi-factor authentication administration, including configuring authentication methods, applying registration requirements, managing user enrolment and reviewing sign-in or authentication issues.
Yes. Effective Microsoft 365 security training should cover multi-factor authentication (MFA) administration as an identity security discipline, not simply as a user sign-in feature. Administrators need to understand how MFA is governed, how authentication controls interact, how exceptions are managed and how access is recovered without creating a route around security.
A comprehensive course should explain the difference between authentication methods, authentication requirements and enforcement. This helps administrators select controls appropriate to different users, applications and risk levels rather than enabling settings without understanding their effect. Training may also cover stronger authentication options, authentication strengths and the circumstances in which a particular method should not be accepted.
Administration training should include MFA governance, including:
- Defining who can manage authentication settings and separating administrative duties where appropriate
- Applying consistent standards to employees, contractors, privileged administrators and service accounts
- Recording policy changes, approvals and exceptions
- Reviewing unused, unsuitable or weak authentication methods
- Removing access and authentication options when a user changes role or leaves the organisation
- Maintaining a controlled process for temporary exclusions and emergency access
Emergency access accounts require particular attention. Training should show why these accounts must be protected differently from ordinary administrator accounts, how their credentials and authentication methods are controlled, and how their use is monitored. The aim is to preserve a recovery path if normal authentication controls fail without allowing that path to become an unmanaged permanent exception.
Good MFA administration training also addresses operational risk. Administrators should learn how to recognise repeated approval prompts, unexpected method changes, suspicious enrolment activity and attempts to persuade users to approve an unauthorised request. This links MFA management with broader identity protection and incident-handling procedures, while keeping the focus on the administrative decisions that prevent or contain abuse.
Policy interactions are another important part of the syllabus. MFA controls can be affected by Conditional Access, security defaults, application requirements, privileged identity controls and legacy authentication. A capable administrator should be able to assess the combined result of these settings, identify conflicting rules and test changes before applying them broadly. Training should make clear that adding another policy does not necessarily strengthen security if an older configuration creates an unintended exemption.
Assessment should go beyond theory. Suitable exercises might ask an administrator to:
- Review an authentication design and identify gaps or unnecessary exceptions
- Plan a controlled policy change for different user groups
- Protect emergency access arrangements
- Evaluate an authentication method against the organisation’s risk profile
- Document a change and define how it will be reviewed
- Respond to suspicious MFA activity using the organisation’s escalation process
The depth required depends on the learner’s responsibilities. A helpdesk employee may need to understand approved support procedures and escalation boundaries, while a security administrator needs stronger knowledge of policy design, privileged access, audit evidence and recovery planning. Training should therefore map MFA competencies to job roles instead of treating every administrator as having the same permissions.
When evaluating a course, check whether it includes practical administration, policy dependencies, emergency access, lifecycle governance and an assessment of decision-making. A course that only demonstrates how to turn MFA on may be useful as an introduction, but it does not provide the knowledge needed to operate MFA safely in a business environment. Organisations that need help translating these principles into a workable Microsoft 365 security model can seek guidance from an experienced managed IT provider.
Microsoft 365 security training should explain that MFA administration is not identical for every identity. Human users, privileged administrators, shared accounts and non-interactive service accounts may have different authentication requirements, so applying a single MFA procedure across the tenant can create operational problems or encourage unsafe workarounds.
A useful course should teach administrators how to identify these identity types, confirm which accounts genuinely require interactive sign-in and document an approved approach for exceptions. It should also explain how to review older accounts and workloads that rely on weaker authentication, so that MFA administration supports the wider identity design rather than treating user prompts as the only measure of protection.
Review Your Microsoft 365 MFA Administration Training Needs
Review your current Microsoft 365 MFA administration arrangements against the governance, recovery and assessment points outlined above. If you need help identifying training or administration gaps, speak to S2 Technology Group about guidance for your organisation.