Does Microsoft 365 security training cover application consent risks?
Yes. Microsoft 365 security training can cover application consent risks by teaching administrators how OAuth permissions work, how to assess requested access, and how to restrict or revoke consent that could expose organisational data.
Application consent risk is the possibility that a user or administrator grants an application access to Microsoft 365 data or functions beyond what the organisation intended. Effective security training addresses this as an identity and data-governance issue, not simply as a user-interface task.
The training should explain the difference between delegated permissions and application permissions. Delegated permissions allow an application to act within the signed-in user’s access, whereas application permissions can allow a service to operate without a user being present. The latter can create a wider exposure if the application is compromised, misconfigured or controlled by an untrusted party. Administrators need to understand that the name and apparent purpose of an application do not, by themselves, establish that its requested permissions are appropriate.
A practical course normally examines the following points:
- Permission scope: whether an application needs to read, create, modify or delete information, and whether the requested access extends across one user, selected sites, mailboxes or the wider tenant.
- Consent type: whether approval has been given by an individual user, an authorised administrator or a process that permits consent on behalf of others.
- Business justification: whether the application supports a documented business requirement and whether its access is proportionate to that requirement.
- Publisher and application identity: whether the publisher is known, the application details are consistent with the supplier’s documentation, and the request contains signs of impersonation or deception.
- Data destination: what information leaves the tenant, where it is processed, and whether the application’s handling arrangements meet the organisation’s contractual and regulatory requirements.
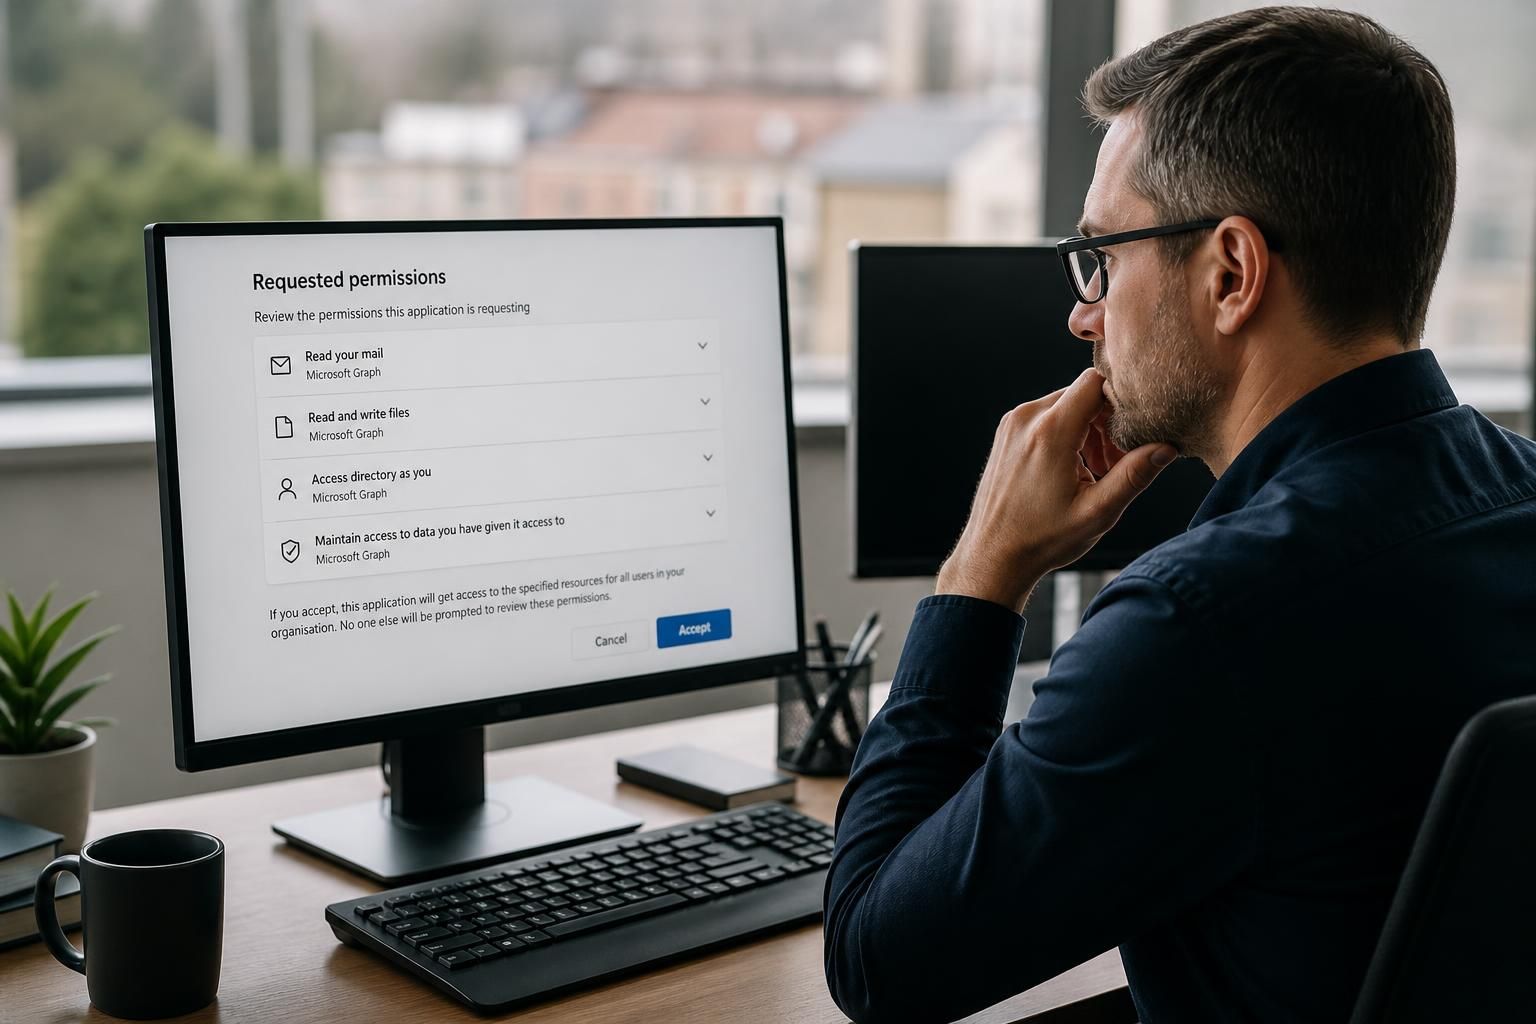
Training should also show how consent abuse appears in realistic scenarios. A malicious application may be presented through a convincing sign-in or collaboration message and request access to mail, files, contacts or directory information. If the user accepts the request, an attacker may gain a persistent route to data without needing the user’s password. A legitimate application can create a similar governance problem when it is granted broad permissions for convenience, retained after a project ends, or approved without reviewing a change in its access requirements.
Administrators should learn to apply a controlled consent model. This can include limiting who may approve applications, requiring administrative review for higher-risk permissions, maintaining a record of approved applications and preventing users from granting permissions that have not passed the organisation’s criteria. The course should distinguish between blocking consent completely and introducing a review process, since a blanket restriction may disrupt legitimate business applications while an unrestricted model increases exposure.
Application reviews should be repeatable rather than based on a one-off decision. A useful procedure records:
- The application’s name, publisher and requested permissions.
- The business owner and intended users.
- The data and services that the permissions can reach.
- The reason each permission is necessary.
- The approval decision, reviewer and review date.
- The conditions for renewal, removal or escalation.
Security administration training can then connect this process with monitoring. Administrators should know where to identify new service principals, consent grants, permission changes and unusual application activity in the tenant’s audit records. A new consent grant from an unexpected user, an unfamiliar publisher, or a sudden increase in access to mail and files may justify investigation. The relevant records should be correlated with sign-in activity, user reports and other indicators rather than assessed in isolation.
Revocation is another important part of competence. Removing an application from an approved list may not remove permissions that have already been granted, so administrators need to understand the separate steps involved in withdrawing consent, disabling or removing the application identity, and checking whether credentials or other access paths remain. Training should cover ownership and escalation as well: a suspected malicious grant may require the user account, application and affected data to be investigated together.
The strongest courses use exercises rather than relying solely on definitions. For example, a learner might compare a narrowly scoped file-management application with one requesting broad access to mail and directories, decide which approvals are required, document the rationale, and respond to a simulated suspicious consent grant. This tests judgement, evidence gathering and governance, not just the ability to locate an administrative setting.
For a small or growing organisation without a large in-house IT function, this knowledge helps turn application consent into a managed control. It supports more consistent decisions about third-party applications, reduces approval by assumption, and gives administrators a structured basis for reviewing access as business requirements change.
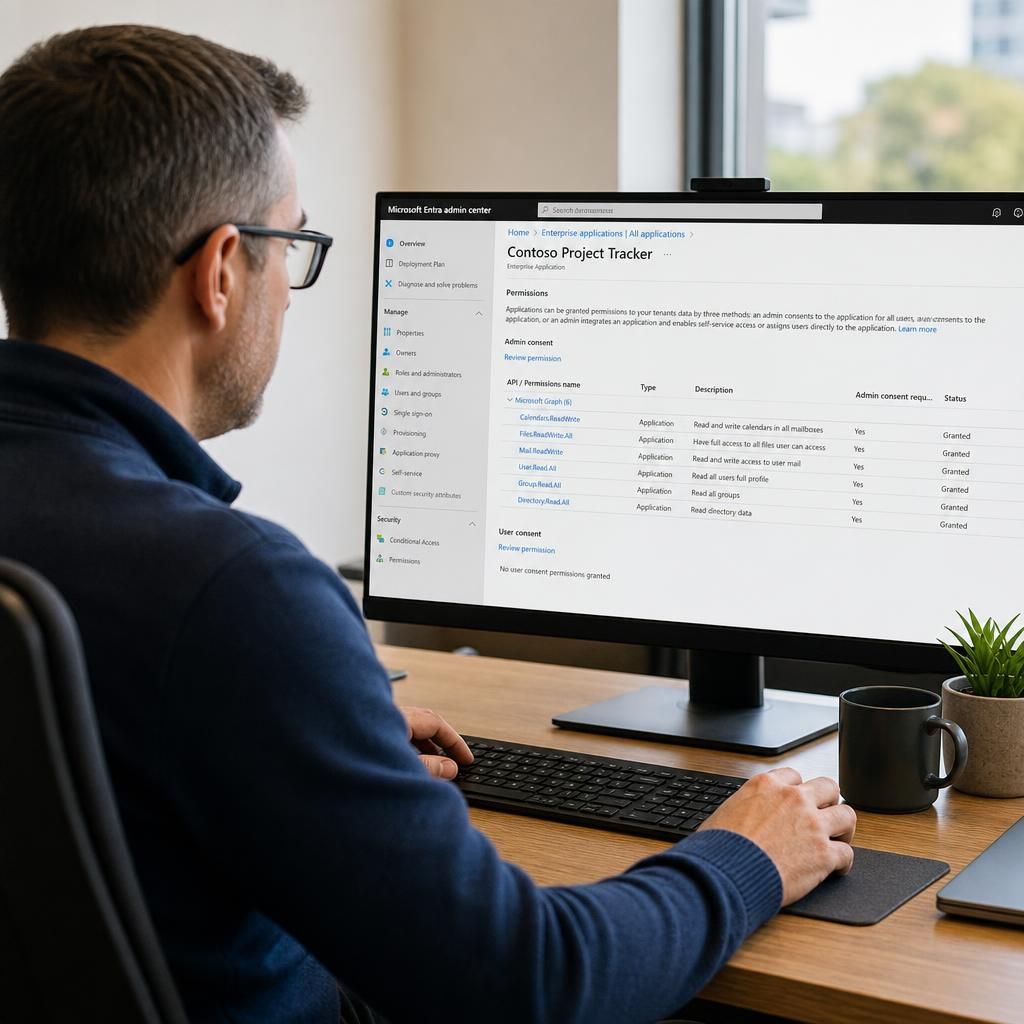
Application consent training should also explain the difference between an app registration and its service principal. An app registration describes the application’s identity and permissions, while the service principal is the tenant-specific representation through which that application operates. Reviewing the service principal helps an administrator determine how the application is configured within the organisation, rather than relying only on information supplied by the publisher.
Administrators should learn to examine the application’s assigned permissions, credentials, owners and tenant-specific configuration, then distinguish ordinary delegated consent from application-role assignments. This gives them a clearer view of how the application can act in the tenant and which internal account or team is responsible for it. Training that includes this distinction makes application consent reviews more accurate and helps prevent an apparently familiar application from receiving access that has not been properly governed.