
How are managed network services introduced into an existing network?
Managed network services are introduced through a planned discovery and transition process, beginning with an assessment of the existing infrastructure, devices, configurations and business requirements. The provider then documents the network, agrees responsibilities, establishes monitoring and security controls, and introduces any changes in controlled stages with testing and validation to minimise disruption.
Managed network services are introduced by integrating the provider’s management processes and technical tools with the organisation’s existing infrastructure, rather than replacing the network in one step. The transition normally separates information gathering, preparation, implementation and post-change review so that business-critical connections, applications and users remain accounted for throughout.
The first practical task is to establish how the network is currently operated. This includes identifying the internet connection, internal network segments, wireless infrastructure, firewalls, switches, routers, virtual networks, remote-access services and important links between sites. The provider also needs to understand which systems depend on particular addresses, ports, routes or security rules. These dependencies can include file services, hosted applications, telephony, manufacturing equipment, warehouse systems and cloud platforms.
Access is then arranged in a controlled manner. Depending on the service, this may involve privileged administrative accounts, read-only access, secure remote management tools, configuration backups or connections to existing alerting systems. Access should be limited to what is required, protected with appropriate authentication and recorded so that changes can be attributed to an authorised person or process. Shared administrator passwords and undocumented access paths create unnecessary risk during onboarding and should be replaced with controlled arrangements.
Before management begins, the provider will usually establish a technical baseline. This records the normal condition of key services, such as internet connectivity, site-to-site links, wireless coverage, device availability, routing, utilisation and recurring alerts. A baseline helps distinguish an existing fault from a new issue and provides context when assessing the effect of later configuration changes. It can also reveal unsupported equipment, inconsistent settings, obsolete rules or single points of failure that need to be considered in the service design.
The existing network does not always conform to a clean or modern design. Older switches may not support the required management features, firewall rules may have accumulated without clear ownership, and devices may use firmware or configurations that cannot be managed safely through the proposed tooling. These limitations should be recorded as transition constraints rather than hidden. In some cases, the right approach is to manage the compatible parts first while planning a separate replacement or redesign for the remainder.
Integration commonly involves several technical activities:
- Adding approved monitoring and management agents, collectors or probes to suitable network devices and servers.
- Configuring secure management protocols and restricting them to authorised administrative paths.
- Importing or recreating device information, naming conventions, network maps and configuration records in the provider’s management system.
- Connecting relevant security, backup, cloud or service-desk information where this is included in the agreed service.
- Reviewing alert thresholds so that genuine service-impacting conditions are distinguished from harmless background events.
- Confirming that monitoring traffic and management access do not conflict with firewall rules, bandwidth limitations or sensitive operational systems.
Network changes are normally introduced in an order that reflects dependency and risk. For example, management access may need to be established before a firewall can be reviewed, while a firewall change may need to precede the introduction of a new remote-access arrangement. A staged approach can begin with a lower-risk site, device group or monitoring-only period before extending the same controls across the wider environment.
Implementation planning should define the change window, the people authorised to approve and perform the work, the expected effect on users, the checks that will confirm success and the procedure for reversing the change. A rollback is not simply a copy of the previous configuration: it should also account for altered routes, authentication settings, access rules, DNS records, dependencies and any connected service that may have changed during the implementation.
Where the network serves multiple offices, remote workers or cloud resources, the transition may be carried out by service area rather than by device type alone. Internet edge equipment, inter-site connectivity, internal switching, wireless access and remote access can each have different dependencies. Treating them as separate workstreams makes it easier to identify which users and applications could be affected by a particular modification.
Business users should be told what they need to know before a change takes place, particularly where a new authentication method, remote-access client, wireless arrangement or network address is involved. Technical teams may also need a list of critical users, sites and applications for validation. Clear ownership of these checks avoids assuming that a network is working simply because its devices respond to management tools.
After implementation, validation should cover both infrastructure and business functions. Typical checks include:
- Connectivity between relevant sites, network segments and remote users.
- Access to essential applications, shared resources and cloud services.
- Voice, video and other services that are sensitive to latency, packet loss or routing changes.
- Firewall enforcement, remote-access permissions and separation between security zones.
- Device health, configuration collection, alert generation and the visibility of important links.
- Performance against the agreed technical baseline, with unusual results investigated rather than dismissed.
A transition is complete only when the new management arrangements are usable in practice. The final records should identify the devices and services under management, known exclusions, outstanding risks, approved administrative routes, escalation responsibilities and any work deferred to a later project. This gives the organisation a clear boundary between what the managed service covers and what remains a separate upgrade, supplier dependency or internal responsibility.
For a small or medium-sized organisation, the most important distinction is between onboarding management of the current network and redesigning that network. Managed network services can be introduced without an immediate wholesale replacement, but existing weaknesses may still need remediation to support secure and reliable operation. Keeping onboarding, remediation and future improvement as separate decisions makes costs, risks and priorities easier to evaluate.
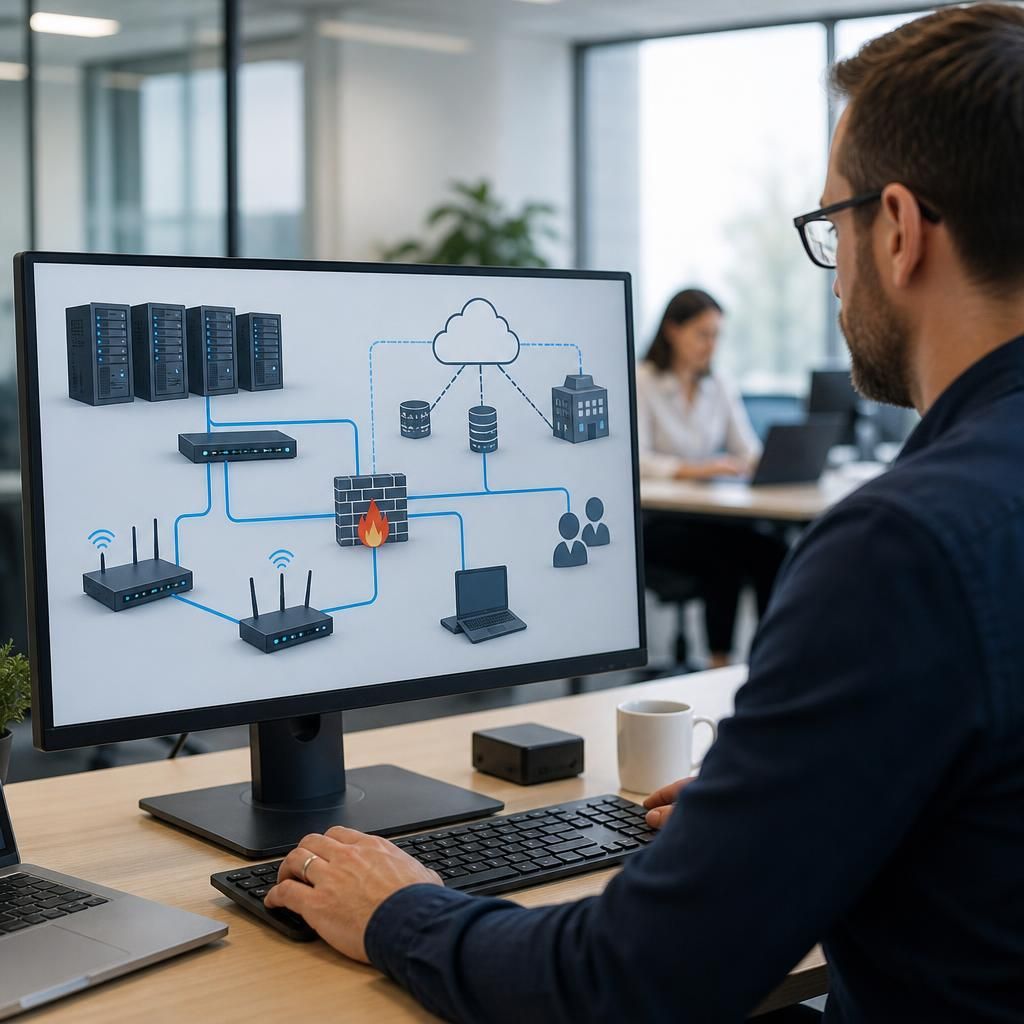
Managed network services can be introduced in stages, allowing an organisation to choose how much operational control transfers at each point. A monitoring-only phase provides visibility without changing device configurations. A co-managed arrangement allows the provider and internal team to share defined tasks, while a fully managed model transfers agreed network administration after the required access, documentation and controls are in place.
The appropriate starting point depends on the condition of the existing network, the organisation’s internal capability and the risk associated with changing critical services. Each stage should have clear entry and exit criteria, including which devices are included, which actions require approval, who handles incidents and what limitations remain. Moving to the next stage should be based on the provider’s ability to manage the environment safely and consistently, rather than on a fixed transition date.
Discuss introducing managed network services into your existing network
If you are considering managed network services, contact S2 Technology Group to review your current environment and discuss a suitable onboarding approach. A structured assessment can help clarify the information, access arrangements and responsibilities needed before implementation begins.