
How is accountability defined for managed IT infrastructure?
Accountability for managed IT infrastructure is defined by documenting who owns each system, task and decision, then measuring performance against agreed responsibilities. Clear reporting, monitoring and escalation procedures show whether infrastructure is being maintained, risks are being addressed and issues are being followed through.
Accountability for managed IT infrastructure means that each area of the technology environment has an identifiable owner with the authority, resources and obligation to keep it properly managed. It is broader than assigning technical tasks: it establishes who makes decisions, who carries out the work, who approves exceptions and who remains answerable when infrastructure creates operational, security or compliance risk.
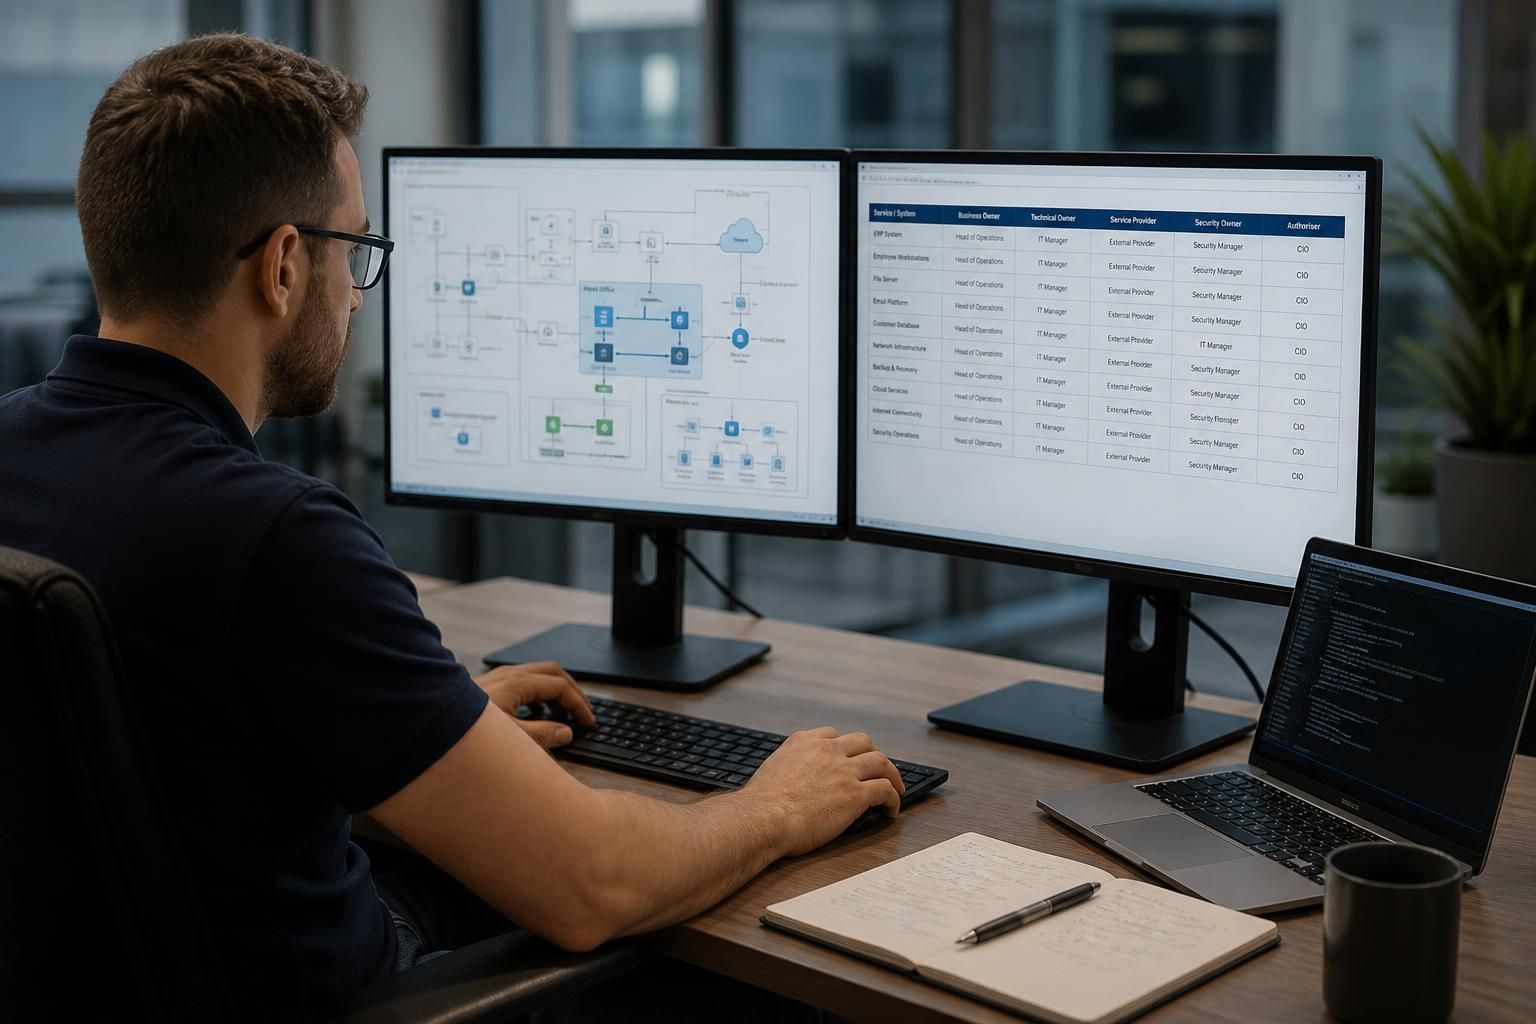
A well-defined accountability model normally separates several roles:
- Business owner: confirms how the system supports business operations, sets priorities and accepts the consequences of service or risk decisions.
- Technical owner: understands the system’s design, dependencies, configuration and lifecycle, and makes sure technical decisions are appropriate.
- Service provider: performs agreed operational activities, maintains relevant records and raises matters that require a business decision.
- Control or security owner: verifies that access, protection, continuity and other control requirements are addressed.
- Authoriser: approves material changes, exceptions, expenditure or risk acceptance where the decision exceeds the provider’s delegated authority.
These roles may be held by different people or combined in a smaller organisation, but the combination should be explicit. A managed IT provider can administer infrastructure without owning every business decision. For example, the provider may recommend a platform change and implement an approved configuration, while the client decides whether the operational impact and cost are acceptable.
Accountability should be set out in the managed service agreement and supporting operating documents. Useful documentation includes an infrastructure inventory, service ownership matrix, network and system diagrams, access responsibilities, maintenance procedures, change authorities, backup ownership and continuity arrangements. Each record should identify the scope covered, the person or role accountable, any delegated duties and the point at which an issue must be handed to another decision-maker.
Clear boundaries are particularly important where responsibility is shared. A cloud service, hosted application or connectivity service may involve the provider, a third-party supplier and the client’s own staff. The agreement should distinguish between the parts each party controls and the actions that remain with the client, such as approving user access, supplying accurate business information or deciding how long data must be retained. Without this distinction, a business may assume that a managed service includes controls that have never been assigned to anyone.
Accountability also depends on decision rights. The operating model should explain who can:
- approve standard and non-standard infrastructure changes;
- accept a known technical or security risk;
- authorise emergency action;
- approve privileged access;
- retire equipment, systems or accounts;
- commit the organisation to additional services or expenditure; and
- declare that a service has returned to an acceptable operating state after a disruption.
Delegation should have limits. Routine administration may be delegated to an IT team or managed provider, while changes affecting data protection, business continuity, regulatory obligations or critical operations may require approval from a senior business owner. The distinction prevents technical convenience from becoming an unapproved business decision.
Evidence is an important part of accountability. A record should show what was requested, who approved it, what was done, when it was completed and whether any follow-up remained outstanding. Depending on the activity, this may include access reviews, change records, configuration baselines, backup checks, vulnerability remediation records, asset disposal evidence and post-incident actions. Evidence makes it possible to distinguish between an issue that was identified and one that was actually resolved.
Accountability should apply across the infrastructure lifecycle, not only when faults occur. During planning, owners define requirements and risk tolerances. During implementation, authorised parties confirm that the design and configuration meet those requirements. During operation, responsible teams maintain the environment and address exceptions. During review, owners decide whether controls, capacity and support arrangements remain suitable. At retirement, someone must approve the removal of equipment, software, accounts and retained data.
Good governance also provides a route for unresolved matters. If a technical issue cannot be corrected within the agreed authority, it should be assigned to an owner who can choose between remediation, replacement, risk acceptance or temporary mitigation. The decision, its rationale and any review date should be recorded. This avoids risks remaining indefinitely in an informal queue with no one empowered to decide their outcome.
Accountability is strongest when it is reviewed after organisational, supplier or infrastructure changes. New sites, acquisitions, cloud migrations, changes in staffing and the introduction of critical applications can all alter ownership boundaries. Reviewing the responsibility model at these points helps ensure that documentation, access rights and approval routes still match the environment being operated.
For a small or medium-sized business without a complete internal IT function, a managed IT arrangement can provide operational expertise while retaining business control over priorities and risk decisions. The important question is not simply whether an external provider is involved, but whether the division of authority is documented, understood and supported by usable evidence. That is what turns a service relationship into accountable management of the infrastructure.
Accountability for managed IT infrastructure is meaningful only when ownership is linked to a defined outcome, not merely to a list of completed tasks. A provider may carry out maintenance, monitoring or administration, but the accountability model should also show what acceptable operation means and who evaluates whether that standard has been met.
This can be established by recording measurable acceptance criteria for important infrastructure services. These might cover configuration conformity, backup recoverability, security control status, capacity thresholds or the completion of agreed remediation work. Where a criterion is not met, the record should identify the business impact, the corrective action required and the point at which the matter is reconsidered if it remains unresolved.
This approach separates activity from performance. A maintenance task being marked complete does not, by itself, demonstrate that the underlying risk has been reduced or that the service is suitable for continued operation. Reviewing outcomes in this way gives business owners a practical basis for challenging assumptions, prioritising investment and confirming that managed infrastructure remains aligned with operational needs.