
How does zero trust apply to identity and access security?
Zero trust applies to identity and access security by assuming no user, device or connection is trusted automatically, whether inside or outside the organisation’s network. Access is granted only after verifying identity and context, then limited to the specific systems and actions required, with trust reassessed as circumstances change.
Zero trust applies to identity and access security by making an access decision for each request rather than treating successful sign-in as permanent permission. Authentication establishes who or what is requesting access; zero trust then evaluates whether that identity, device, session and requested action meet the organisation’s policy for the particular resource.
This changes identity security from a one-off login control into a set of decisions covering the whole access lifecycle. The central question is not simply whether a person has an account, but whether the account should be allowed to perform a specific action, against a specific system, under the current circumstances.
Identity becomes the main control point
In a traditional perimeter-based model, a user may receive broad access after connecting to the corporate network. A zero trust model places policy around applications, data and administrative functions instead. Network location alone does not establish legitimacy, and being connected through a recognised route does not remove the need for identity controls.
Policies can consider several signals before authorising access, including:
- the individual, group, role or workload requesting access;
- the strength and recent status of authentication;
- the security condition of the device, such as encryption, patching and endpoint protection;
- the application, data set or administrative function being requested;
- the sensitivity of the operation, including whether it changes configuration or accesses confidential information;
- the connection characteristics, such as network, location and unusual access patterns; and
- the duration and scope of the requested session.
These signals should be used proportionately. A low-risk business application may require a different control decision from a domain administration console or a system containing regulated information. Zero trust is therefore not a single product or setting; it is a policy model implemented through connected identity, device, application and monitoring controls.
Authentication is necessary but not sufficient
Strong authentication is an important part of zero trust, but it does not by itself create a zero trust environment. A valid password, token or authentication session can still be misused if an account has excessive permissions, a device is compromised or the request is directed at the wrong resource.
Identity security should therefore distinguish between proving an identity and authorising an action. Authentication methods can be selected according to risk, with stronger or additional checks applied to sensitive systems, unusual circumstances and privileged operations. Session policies can also require renewed verification where the user’s circumstances change or where a higher-risk action is attempted.
Access should be narrow and specific
Zero trust limits access by separating users, resources and actions. A person may be permitted to view records without being permitted to export them, or to use a finance application without being allowed to alter its configuration. Administrative rights should be assigned to defined functions rather than attached broadly to a general user account.
Effective policy design commonly includes:
- role-based access for standard responsibilities;
- attribute-based rules where access depends on factors such as department, device state or data classification;
- separate approval for sensitive or exceptional access;
- time-limited elevation for administrative tasks; and
- automatic removal of access when the business reason no longer exists.
Permissions should be reviewed against actual responsibilities rather than copied indefinitely from historic roles. This is particularly important when people change job function, work across several systems or retain access from previous projects.
Zero trust includes the identity lifecycle
The model must operate before, during and after a user’s access. During onboarding, an organisation should establish the person’s identity, employment relationship, role and required resources. When responsibilities change, permissions should be adjusted rather than simply supplemented. When the relationship ends, accounts, sessions, tokens, devices and connected application access should be revoked through a controlled process.
The same principle applies to non-human identities. Applications, scripts, integrations and devices may require access to services, but their credentials should be assigned to a defined purpose, protected appropriately, limited in scope and monitored for unexpected use. Treating these identities as permanent, highly privileged accounts creates a gap in an otherwise carefully designed user access model.
Privileged access requires additional separation
Administrator identities can affect security settings, create accounts and alter evidence, so they need stronger controls than ordinary business accounts. Zero trust can support separate administrative identities, approval-based elevation, restricted management paths and detailed recording of privileged activity. Administrative access should be granted for a defined task and removed or allowed to expire when that task is complete.
Separating ordinary work from administration also reduces the chance that a compromised email or browsing session immediately provides access to critical systems. It does not eliminate the need for secure administration practices, but it narrows the available routes to high-impact actions.
Monitoring is part of the access decision
Zero trust depends on reliable evidence. Identity providers, endpoint tools, cloud services, firewalls and business applications should produce records showing authentication events, permission changes, access decisions and significant actions. These records help identify patterns such as repeated authentication failures, access from an unmanaged device, unexpected use of a privileged account or activity outside an account’s normal function.
Monitoring should lead to an appropriate response. Depending on the policy, a request may be allowed, challenged with stronger authentication, limited to read-only activity, referred for approval or blocked. Alerts should be investigated in the context of the user’s role, device and recent activity rather than treated as isolated events.
A practical implementation approach
- Identify important applications, data stores, administrative interfaces and the identities that can reach them.
- Remove dormant accounts, shared credentials and unnecessary standing privileges.
- Establish a reliable source for user identity, role and employment status.
- Apply strong authentication and separate controls for privileged access.
- Introduce device and session conditions for higher-risk resources.
- Define access policies for common, sensitive and exceptional activities.
- Connect relevant logs so access decisions and changes can be reviewed.
- Test the policies, measure false positives and refine them without creating unmanaged exceptions.
Implementation should be staged around the systems and identities that would cause the greatest harm if misused. It should also account for legacy applications that cannot support modern authentication or detailed policy controls. Where replacement is not immediately practical, compensating measures may include tighter network restrictions, an access gateway, additional monitoring and reduced permissions.
Zero trust is working effectively when access is understandable, attributable and proportionate: the organisation can identify who or what requested access, why it was permitted, what it could do, which controls applied and whether the permission remains justified. In identity and access security, that combination of explicit policy, limited authority, lifecycle management and usable evidence is what turns the zero trust principle into an operational control framework.
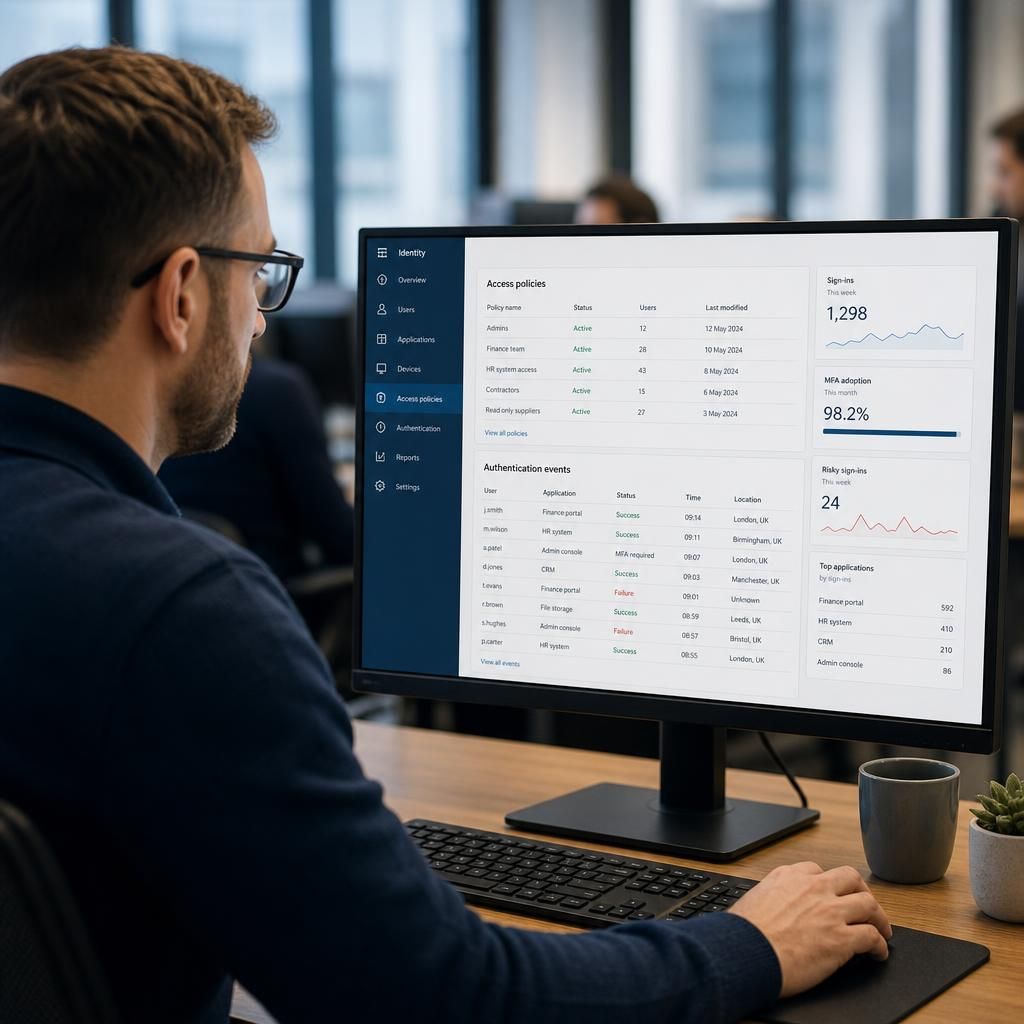
In zero trust identity and access security, a policy decision must be enforced at the point where access is requested. The identity provider may evaluate the request, but an enforcement point must apply the result by permitting, restricting or denying access to the relevant application, data or administrative function.
This separation helps prevent a policy from existing only as a rule in an identity platform while access remains uncontrolled elsewhere. Enforcement can be provided by an application, cloud service, privileged access gateway or access proxy. Each should receive a clear decision and apply it consistently, including when a session is revoked or its conditions no longer meet policy.
- Decision: assess the identity, requested resource and applicable conditions.
- Enforcement: allow only the approved application, operation or session scope.
- Change: apply updated decisions when permissions, device status or risk conditions change.
- Evidence: record the request, decision and resulting action for later review.
This arrangement makes zero trust more than an authentication method. It connects identity policy to the systems that handle business activity, so an approval has a defined technical effect and can be checked against what actually happened.