
How often should a cyber risk assessment be reviewed?
A cyber risk assessment should be reviewed at least annually, with the frequency increased where the organisation, its technology or its threat environment is changing rapidly. It should also be revisited after significant changes to systems, suppliers, processes or regulatory obligations.
The review interval for a cyber risk assessment should be proportionate to the organisation’s risk profile, rather than treated as a fixed administrative date. A lower-risk business with stable systems may need a scheduled review less frequently than an organisation with complex infrastructure, valuable data, remote access, multiple sites or significant reliance on suppliers. The key question is whether the assessment still accurately represents the organisation’s assets, threats, vulnerabilities and controls.
A review does not always require the entire assessment to be rewritten. It may involve checking whether the existing information remains accurate, validating risk ratings, confirming that agreed treatments have been completed and recording any new evidence. A full reassessment is more appropriate where the underlying assumptions have changed or where previous findings were incomplete.
A practical review programme usually includes:
- A planned formal review: senior management or the person responsible for information security should confirm that the assessment remains current and approve any changes to priorities or treatment plans.
- Interim monitoring: risk owners should track vulnerabilities, security incidents, audit findings, access changes, supplier issues and overdue control improvements between formal reviews.
- Focused reassessments: individual areas such as cloud services, privileged access, backups, endpoint security or business continuity can be reviewed separately when their risk profile warrants closer attention.
- Evidence checks: the organisation should verify that policies, technical configurations, training records, test results and remediation documents still support the conclusions in the assessment.
Risk-based frequency is particularly important where the consequences of compromise are high. An organisation processing sensitive personal data, operating critical production systems or depending on continuous access to technology may need more frequent scrutiny than a business with fewer systems and less sensitive information. The assessment should record why its review interval was selected so that the decision can be explained to directors, auditors, customers or regulators.
Reviews should also consider whether the organisation’s risk appetite has changed. A business may accept a risk while a system is temporary, for example, but require additional controls when that system becomes business-critical. Changes in insurance conditions, contractual requirements, recognised security standards or regulatory expectations can also make an otherwise accurate assessment unsuitable for current governance purposes.
Each review should produce a clear record of:
- the date, scope and people involved;
- the information and evidence examined;
- risks that have increased, decreased, been closed or newly identified;
- changes to risk owners, deadlines and treatment actions;
- accepted residual risks and the person authorised to accept them; and
- the next planned review and the conditions that would bring it forward.
Warning signs that a review is overdue include asset registers that no longer match the environment, controls recorded as complete without supporting evidence, unresolved high-priority findings, security policies that refer to former systems or suppliers, and risk ratings that have not changed despite substantial operational developments. A review can also be prompted by repeated failed tests, audit observations or an inability to explain how a particular risk is currently controlled.
S2 Technology Group can help small and medium-sized organisations establish a proportionate review cycle, maintain the supporting evidence and connect assessment findings with practical IT and cyber security improvements. The aim is to keep the assessment useful as a management tool, rather than allowing it to become a document that is accurate only on the day it was written.
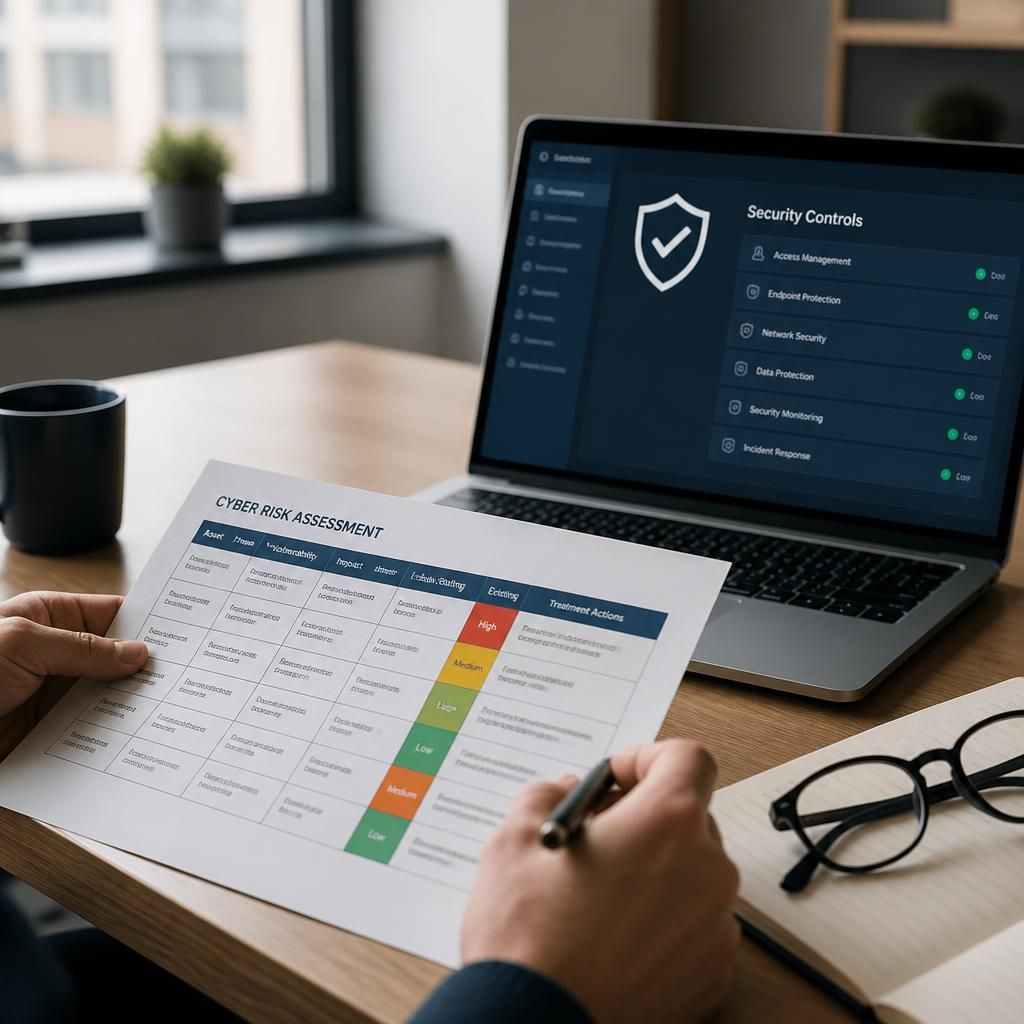
A meaningful cyber risk assessment review should challenge the assumptions behind each risk rating, not simply confirm that the document has been updated. The reviewer should ask whether the stated threat, business impact and control effectiveness still reflect how the organisation operates in practice.
This can be tested through structured discussions with system owners, senior managers and relevant operational teams. Their evidence may reveal changes that are not obvious from technical records, such as a process becoming dependent on one application, staff using an unapproved workaround, or a control being difficult to follow in day-to-day work.
The review should also examine whether risk scenarios remain plausible and whether the recorded consequences are still accurate. For example, the impact of losing access to a system may be substantially different once that system supports a larger part of a business process. Recording these findings separately from routine document amendments helps demonstrate that the assessment has been critically reviewed rather than mechanically renewed.