
What is the difference between cyber incident response and disaster recovery?
Cyber incident response is the process of identifying, containing and investigating a cyber attack or security breach. Disaster recovery focuses on restoring systems, data and business operations after disruption; the two processes often work together, with incident response addressing the threat and disaster recovery restoring affected services.
The distinction is primarily one of purpose and control: cyber incident response manages the security event itself, while disaster recovery manages the restoration of technology and services affected by a disruptive event. Cyber incident response asks what happened, whether the threat remains active and how it can be contained. Disaster recovery asks which systems must be brought back, from which recovery point and in what order.
Cyber incident response is investigative and defensive. It begins when suspicious activity or a confirmed compromise is identified. The response team establishes the scope of the incident, preserves relevant evidence, contains affected accounts or devices, removes the attacker’s access and checks for persistence or further compromise. It may also involve analysing malicious files, reviewing authentication records, identifying data exposure and meeting reporting or notification obligations.
The objective is not simply to make a device or service usable again. Restoring a compromised system before understanding the cause can reintroduce the attacker or overwrite evidence needed to determine what occurred. For that reason, response decisions often prioritise isolation, forensic preservation and confidence that the threat has been removed.
Disaster recovery is restoration-focused. It uses documented procedures, technical safeguards and recovery priorities to rebuild or resume systems after an outage or loss. Depending on the circumstances, this can include recovering data from backups, switching to a secondary environment, restoring virtual machines, rebuilding servers, re-establishing network services and validating applications before users return to them.
Disaster recovery is not limited to cyber attacks. It may be needed after hardware failure, accidental deletion, fire, flood, utility disruption or a serious software fault. Its planning normally considers the recovery point objective—the acceptable amount of data that could be lost—and the recovery time objective—the target period for restoring a service. These objectives should be set according to business impact rather than assumed to be identical for every system.
The two disciplines differ in their main questions:
- Incident response: How did the incident occur? Is unauthorised access still possible? Which users, devices, applications or data are affected? What evidence must be preserved?
- Disaster recovery: Which services are essential? What recovery copies or alternative environments are available? What order should systems be restored in? How will the business confirm that recovery is complete?
They also differ in their success criteria. Incident response is successful when the organisation has contained the threat, understood the compromise sufficiently, removed unauthorised access and taken appropriate follow-up action. Disaster recovery is successful when the required systems and data have been restored to an acceptable state and the business can operate its essential processes. A system being available does not necessarily mean it is secure, and a threat being contained does not necessarily mean the organisation’s services are operational.
In a ransomware scenario, for example, incident response would include isolating affected endpoints, disabling compromised accounts, determining how the attacker entered, identifying the systems touched and preserving evidence. Disaster recovery would then support the controlled restoration of clean systems and data. Recovery copies must be assessed carefully: a backup created after an attacker gained access may contain encrypted data, malicious changes or credentials that remain exposed.
The relationship can also work in the opposite direction. A failed server may initially appear to be a routine availability problem, but investigation could reveal malicious activity. In that situation, treating the event solely as a restoration exercise could destroy evidence or allow the same compromise to recur. Recovery procedures should therefore include a decision point for escalating suspected security events into the cyber incident response process.
A complete business resilience arrangement normally connects both plans. It should define who can declare an incident, who authorises system isolation or restoration, how technical teams communicate with management and how dependencies between systems are handled. It should also identify alternative communication methods in case normal email or collaboration platforms are unavailable, alongside arrangements for legal, regulatory, insurance and stakeholder communications where relevant.
Testing is important because a documented plan may not reflect the current environment. Organisations should periodically verify that backups can be restored, recovery credentials are available, critical dependencies are understood and restoration produces usable systems. Separate exercises should test decisions such as account containment, evidence handling and escalation. Combined exercises are useful for scenarios in which a security investigation and service restoration must happen at the same time.
In practice, businesses need both capabilities rather than choosing one over the other. Incident response reduces the risk of restoring a compromised environment, while disaster recovery provides the means to resume essential operations once the security position is understood. The plans should be linked, but their responsibilities, decision points and measures of success should remain clear.
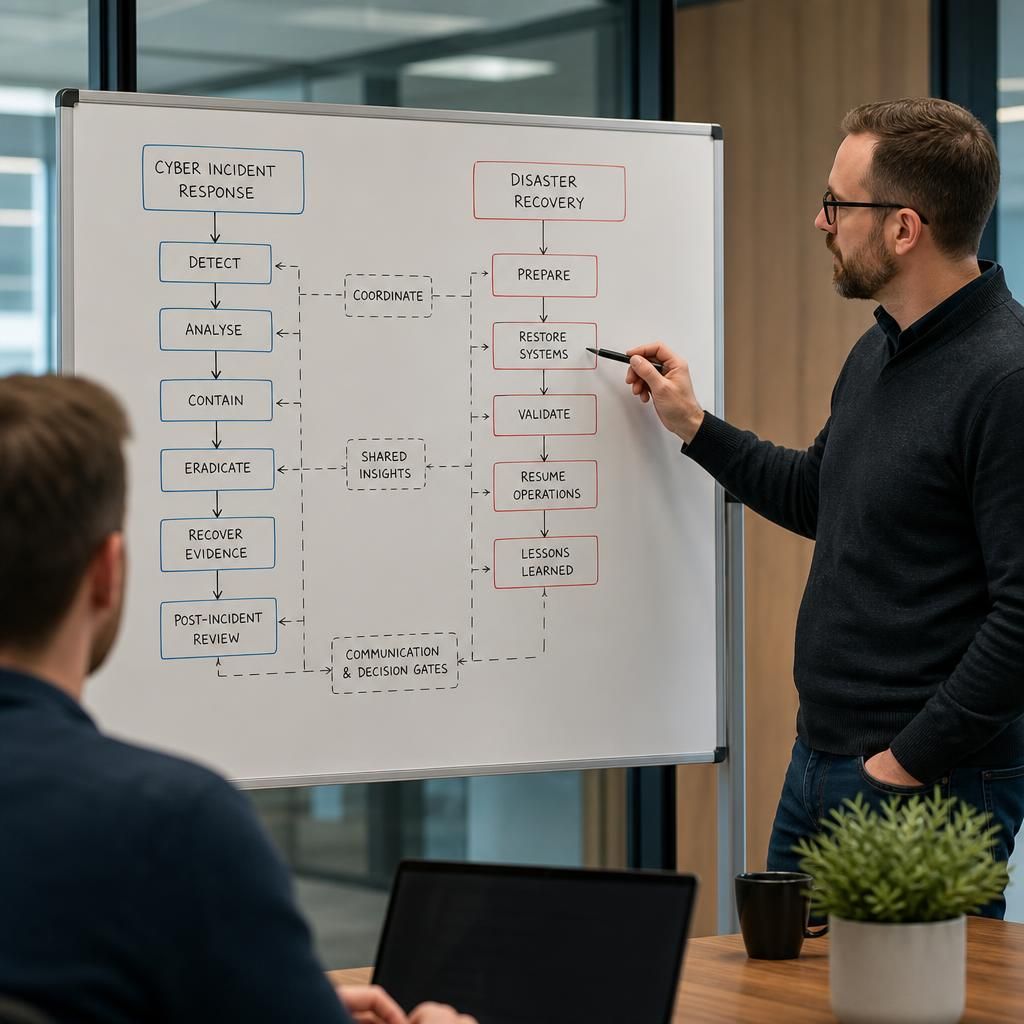
The relationship between cyber incident response and disaster recovery is best managed as two coordinated workstreams rather than one combined procedure. While investigators determine whether an environment is trustworthy, recovery teams can prepare unaffected services, verify restoration materials and map technical dependencies without reconnecting compromised assets.
Clear decision gates help prevent operational pressure from overriding security evidence. Before a system is returned to service, the organisation should record that:
- the affected asset has been examined or appropriately isolated;
- required access controls and credentials have been reviewed;
- the restoration source is suitable for use; and
- business and technical owners have approved the service’s return.
This approach allows essential operations to resume where it is safe to do so, while retaining control over systems that require further investigation. It also creates an auditable record of why each service was restored, deferred or rebuilt.
Review your cyber incident response and disaster recovery arrangements
Review your cyber incident response and disaster recovery arrangements to identify unclear responsibilities, recovery dependencies and gaps in testing. S2 Technology Group can help your business assess how these plans work together and where they need strengthening.