Does Cyber Essentials certification help organisations meet GDPR requirements?
Cyber Essentials certification supports GDPR compliance by helping organisations apply recognised technical controls to reduce common cyber security risks. However, it does not demonstrate full GDPR compliance: organisations must also address governance, data protection processes, lawful processing, data retention and individuals’ rights.
Cyber Essentials certification can support an organisation’s GDPR position by providing a structured baseline for the security of systems that process personal data. Its main relevance is to the UK GDPR requirement for appropriate technical and organisational measures, particularly where an organisation needs to show that common weaknesses have been identified and addressed. It is not a privacy certification and does not, by itself, establish compliance with every GDPR obligation.
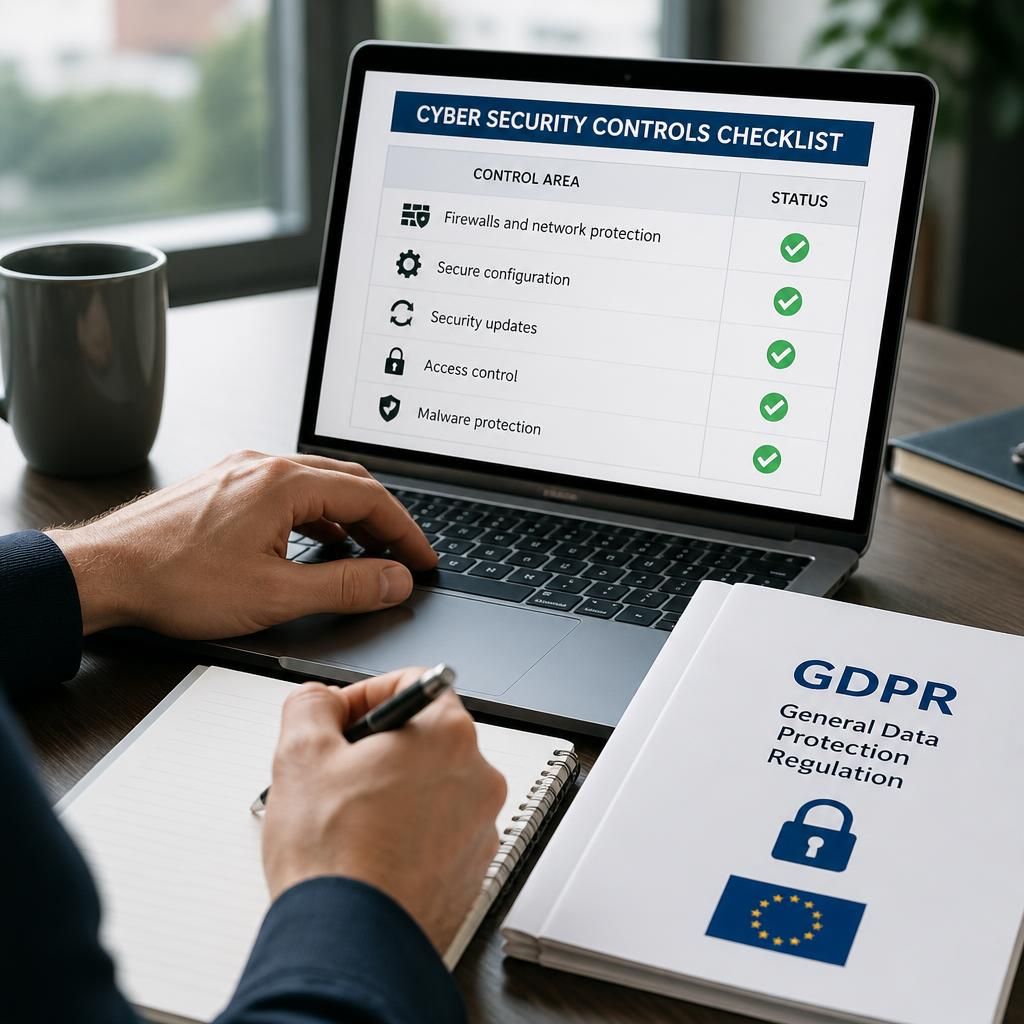
The connection between the two frameworks is strongest in the area of information security. Cyber Essentials examines whether an organisation has controls covering areas such as:
- firewalls and network boundary protection;
- secure configuration of computers, servers and network devices;
- security updates and the management of known vulnerabilities;
- user access controls, including the management of administrator privileges; and
- protection against malware.
These controls can reduce the likelihood that personal data will be exposed through an unpatched system, an unnecessarily privileged account, an insecure device or a preventable malware incident. They can also give an organisation a consistent starting point for reviewing the technical environment in which personal data is stored, accessed or transmitted.
Where Cyber Essentials can provide useful GDPR evidence
GDPR accountability requires an organisation to be able to demonstrate how it complies with its obligations. A current certificate, together with the assessment responses and supporting internal records, can contribute to that evidence. It may help show that the organisation has considered common cyber security risks and implemented a recognised set of baseline safeguards.
The certificate is more useful when it is supported by operational evidence, such as:
- asset registers identifying devices and systems within scope;
- records showing how security updates are monitored and applied;
- access reviews demonstrating that privileges are appropriate;
- configuration standards for workstations, servers and network equipment;
- records of security incidents, remedial actions and management review; and
- documented responsibilities for maintaining the controls after certification.
This supporting material helps connect the certification exercise to the organisation’s actual processing activities. It can also make it easier to explain the security arrangements to senior management, customers, auditors or other interested parties.
What Cyber Essentials does not cover on its own
GDPR applies to the way personal data is collected, used, shared, retained and deleted, not only to the devices and networks that support those activities. An organisation must therefore consider matters such as its lawful basis for processing, privacy information, data subject requests, records of processing activities, data protection impact assessments and arrangements with processors.
It must also decide whether the baseline represented by Cyber Essentials is sufficient for the risks involved. The appropriate level of security depends on factors including the type and sensitivity of the personal data, the scale and context of processing, the possible effect of a breach and the organisation’s use of cloud services, remote access, mobile devices or third parties. A higher-risk processing activity may require additional safeguards, testing or specialist assessment beyond the certification requirements.
Scope is particularly important
A Cyber Essentials certificate relates to the defined technical scope submitted for assessment. If a system containing personal data, a branch network, a home-working arrangement or a service provider falls outside that scope, the certificate does not demonstrate that the excluded environment has the same controls. Organisations should compare the certification boundary with their data flows and processing activities rather than assuming that every GDPR-relevant system is covered.
This comparison should include systems used by employees, infrastructure managed by suppliers and any route through which personal data can be accessed. Where a supplier processes personal data, the organisation remains responsible for selecting an appropriate processor, setting contractual requirements and checking that the supplier’s security arrangements are suitable for the processing involved.
A practical way to use the certification
- Map the systems and suppliers involved in processing personal data.
- Compare that map with the Cyber Essentials scope and identify exclusions.
- Use the certification controls as a baseline for reviewing technical risks.
- Record additional measures needed for higher-risk processing or specific threats.
- Link the technical controls to relevant policies, responsibilities and incident procedures.
- Review the arrangements regularly rather than treating certification as a permanent status.
Used in this way, Cyber Essentials can form one part of a defensible GDPR security and accountability programme. It is most valuable when the controls are maintained in day-to-day operations and considered alongside the organisation’s wider data protection documentation, risk assessments and governance arrangements.
Cyber Essentials certification can support GDPR compliance by giving an organisation a documented basis for judging whether its baseline cyber security controls are proportionate to the personal-data risks it has identified. The important question is not simply whether a certificate exists, but whether the organisation has considered what risks remain after those controls are applied.
For example, certification may address common weaknesses in the assessed environment while leaving additional concerns relating to sensitive information, unusual processing activities or dependencies on external services. Those residual risks should be recorded, assessed and assigned to an appropriate owner. The organisation can then document why further safeguards are, or are not, necessary and when the decision will be reviewed.
This approach helps prevent the certificate from being treated as a substitute for GDPR risk management. It shows that the organisation has used Cyber Essentials as one input into a wider, evidence-based security decision rather than relying on certification as automatic proof that its processing arrangements are compliant.