
How long should Microsoft 365 backup data be retained?
Microsoft 365 backup data should usually be retained for as long as the business needs to recover it, with the exact period determined by operational, legal, regulatory and contractual requirements. A documented retention policy should define how long different data types and backup versions are kept, rather than relying on Microsoft 365’s built-in retention alone.
There is no single correct retention period for Microsoft 365 backup data. A business should retain backup data for the length of time needed to recover from its realistic data-loss scenarios, while also meeting applicable legal, regulatory and contractual obligations. The retention period should be documented and reviewed rather than chosen solely because it is the default offered by a backup service.
The right period depends first on how far back the organisation may need to recover. A recent backup can address accidental deletion, unwanted changes and straightforward user errors. Longer retention becomes important where an issue may remain undiscovered for some time, such as malware that has altered files gradually, a compromised account or an unnoticed synchronisation problem. If every available restore point was created after the problem began, a short retention window may leave no clean copy to recover.
Businesses should assess the data and recovery scenarios that matter to them, including:
- Accidental deletion of emails, files, folders, mailboxes, SharePoint content or Teams-related data.
- Malware, ransomware or unauthorised access that is discovered after the initial incident.
- Incorrect edits or bulk changes that are not noticed immediately.
- The need to recover information belonging to a former employee or a closed project.
- Contractual requirements to preserve business records for a defined period.
- Regulatory, legal, audit or investigation requirements affecting particular records.
Retention is usually best designed in layers rather than as one identical rule for all Microsoft 365 data. Recent restore points may be kept at a practical frequency for day-to-day recovery, while older points are retained less frequently to provide historical coverage. Critical mailboxes, financial records, project information and operational documents may require different treatment from low-value or transient content. This approach can provide a useful recovery history without treating every item as if it has the same business value.
The policy should also define what “retained” means. It may refer to how long an individual backup version remains available, how long a deleted item can be recovered, or how long a complete historical copy of a workload is preserved. These are not always the same. A service may keep recent versions frequently but preserve older versions according to a separate schedule. The organisation should confirm whether the backup product applies retention per user, workload, site, mailbox, storage account or tenant, as this can affect how the policy operates in practice.
Backup retention should not be confused with records retention. A backup is primarily intended to support recovery from data loss or corruption. A records-management policy, retention label or legal hold may instead be intended to preserve specific information in an identifiable and controlled form. Those controls can be important, but they do not automatically provide a complete, independently restorable backup. Businesses with formal preservation duties should map their records requirements to both their Microsoft 365 governance controls and their backup design.
Legal and regulatory requirements should be assessed with the organisation’s legal or compliance adviser. The relevant period can vary by industry, record type, jurisdiction and contract. Some requirements concern preserving information, while others concern secure disposal once the required period has ended. Keeping everything indefinitely is not automatically safer: unnecessary copies can increase storage, discovery and data-protection risks. A sound policy defines both the retention period and the approved disposal process.
Privacy requirements also matter. Backup copies can contain personal data, including information that has been removed from the live Microsoft 365 environment. The business should know where backup data is stored, who can access it, how access is audited and how deletion requests or retention exceptions are handled. If data is replicated to another location, the organisation should check the relevant contractual, geographical and security implications.
Before setting a policy, document the following for each important workload:
- The types of data held and their business importance.
- The maximum acceptable age of a restore point for operational recovery.
- How long a clean historical copy may be needed after an incident is discovered.
- Any legal, regulatory, contractual or insurance conditions.
- Who can authorise restoration, retention exceptions and permanent deletion.
- How former users, deleted sites and closed projects are treated.
- How the organisation will verify that the configured policy is actually being applied.
A retention policy should be tested as part of the wider backup process. Reviewing configuration alone may not confirm that the required historical versions can be found and restored. Periodic recovery exercises should check different data types, older restore points, deleted workloads and the permissions required to complete a recovery. Testing can also reveal that a policy has been changed, a user or site has been excluded, or retention has been consumed differently from what the business expected.
Retention should be reviewed after significant changes, such as a new regulatory obligation, a merger, a change of backup platform, the introduction of a new Microsoft 365 workload or a serious security incident. It should also be reviewed when the organisation’s risk profile or data-storage arrangements change. The objective is a retention schedule that is long enough to provide meaningful recovery options, specific enough to support governance, and controlled enough to avoid keeping unnecessary copies indefinitely.
For many organisations, the practical answer is therefore a documented, workload-specific schedule supported by tested backups and clear disposal rules. The period should be justified by the business’s recovery needs and obligations, not selected as a universal number.
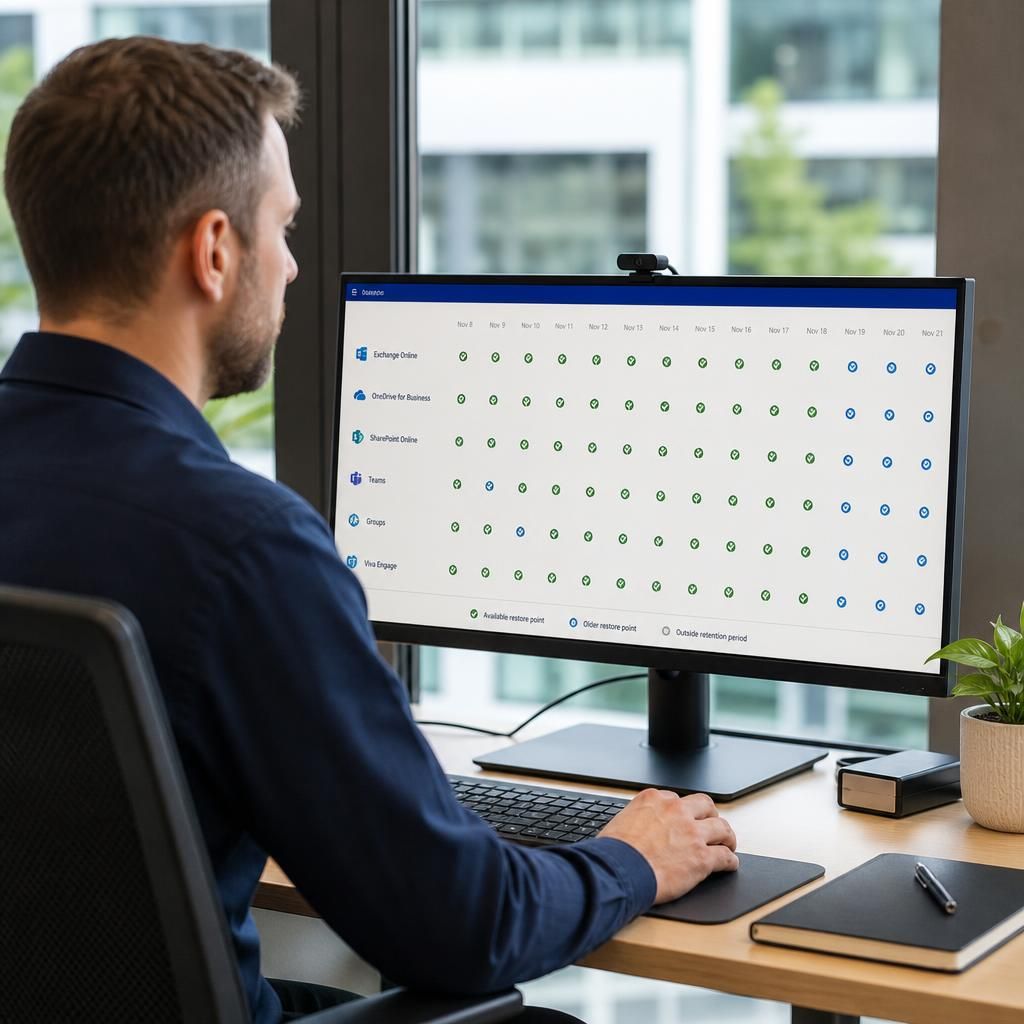
Changing a Microsoft 365 backup retention setting does not necessarily restore historical copies that have already expired. Extending the policy usually affects new backup versions, while older data may remain unavailable if it has already been deleted under the previous schedule. Reducing retention can also make existing restore points eligible for removal.
For that reason, retention changes should be treated as controlled transitions rather than simple configuration updates. Before applying a new policy, confirm how the backup service handles existing versions, whether different workloads follow separate rules, and whether any data must be preserved under the previous arrangement. Record the change, check the resulting restore points and perform a recovery test where the historical coverage is important.
Review your Microsoft 365 backup retention policy
If your organisation is unsure whether its Microsoft 365 backup retention matches its recovery, compliance and disposal requirements, contact S2 Technology Group to review the policy and restore coverage. A documented review can identify gaps before retention settings are changed.