
Can managed backup protect data from compromised administrator accounts?
Yes. Managed backup can protect data from compromised administrator accounts by keeping protected copies separate from production systems, limiting administrative access, and supporting recovery if an attacker deletes, encrypts or alters live data.
Managed backup can reduce the impact of a compromised administrator account, but its effectiveness depends on how the backup environment is designed and administered. Protection is strongest when an attacker who gains control of a production administrator account cannot use the same credentials or permissions to change backup policies, remove recovery points or access the backup management system.
A well-designed service separates the roles used to operate production systems from those used to manage backups. This may include dedicated backup administration accounts, least-privilege permissions, multi-factor authentication and approval controls for sensitive actions. These measures help prevent a stolen domain, server or cloud administrator identity from automatically becoming an all-access backup identity.
The backup platform should also provide safeguards against unauthorised changes to recovery points. Depending on the technology and service design, these can include immutable storage, retention locks, deletion protection and restrictions on shortening retention periods. Immutability means that data cannot be modified during a defined protection period, while deletion protection helps prevent an attacker from removing the copies needed for recovery. These controls should be configured deliberately rather than assumed to exist simply because a business has a backup product.
Security monitoring is another important part of the protection. A managed service can review events such as unexpected policy changes, unusual deletion requests, failed authentication attempts, disabled jobs and sudden changes in the volume or type of backed-up data. Alerts are more useful when they are linked to an agreed investigation process, since a warning that nobody reviews may not prevent damage.
Protection from a compromised administrator account should be considered across several layers:
- Identity controls: use separate administrative identities, multi-factor authentication and permissions limited to the tasks each person needs to perform.
- Management-plane security: restrict access to the backup console and protect its credentials independently from ordinary production administration.
- Recovery-point protection: apply immutability, retention controls or other mechanisms that prevent unauthorised alteration or removal.
- Audit records: retain logs showing who changed settings, accessed recovery data or initiated deletion activity.
- Independent review: check backup configurations and administrative access regularly, particularly after staff, systems or business requirements change.
Encryption is relevant but does not solve the account-compromise problem on its own. Encryption protects data from unauthorised disclosure when it is stored or transferred, but an attacker using a legitimate privileged account may still be able to alter settings or request access. Access control, key management, immutability and monitoring must therefore be considered alongside encryption.
Recovery procedures should account for the possibility that the production administrator account and some connected systems are no longer trustworthy. This can mean using a separate recovery identity, rebuilding clean administrative credentials, confirming the integrity and date of a recovery point, and restoring into an isolated environment before returning systems to normal operation. Recovery testing is important because it verifies not only that backup jobs complete, but also that protected data can be accessed and used without relying on the compromised account.
Managed backup does not make an organisation immune to ransomware or administrator compromise. Poorly separated credentials, excessive permissions, unprotected management consoles, misconfigured retention or untested recovery processes can leave gaps. The service should therefore be assessed as part of a wider cyber security plan that includes privileged-access management, endpoint protection, staff access reviews and an incident response procedure.
For a small or medium-sized organisation, the practical question is not simply whether a backup exists. It is whether a compromised administrator could control, alter or remove that backup, and whether authorised staff could recover critical systems using clean credentials and verified recovery points. A managed backup arrangement that addresses both questions provides a stronger defence against account compromise than a backup process administered through the same unrestricted accounts used for everyday IT management.
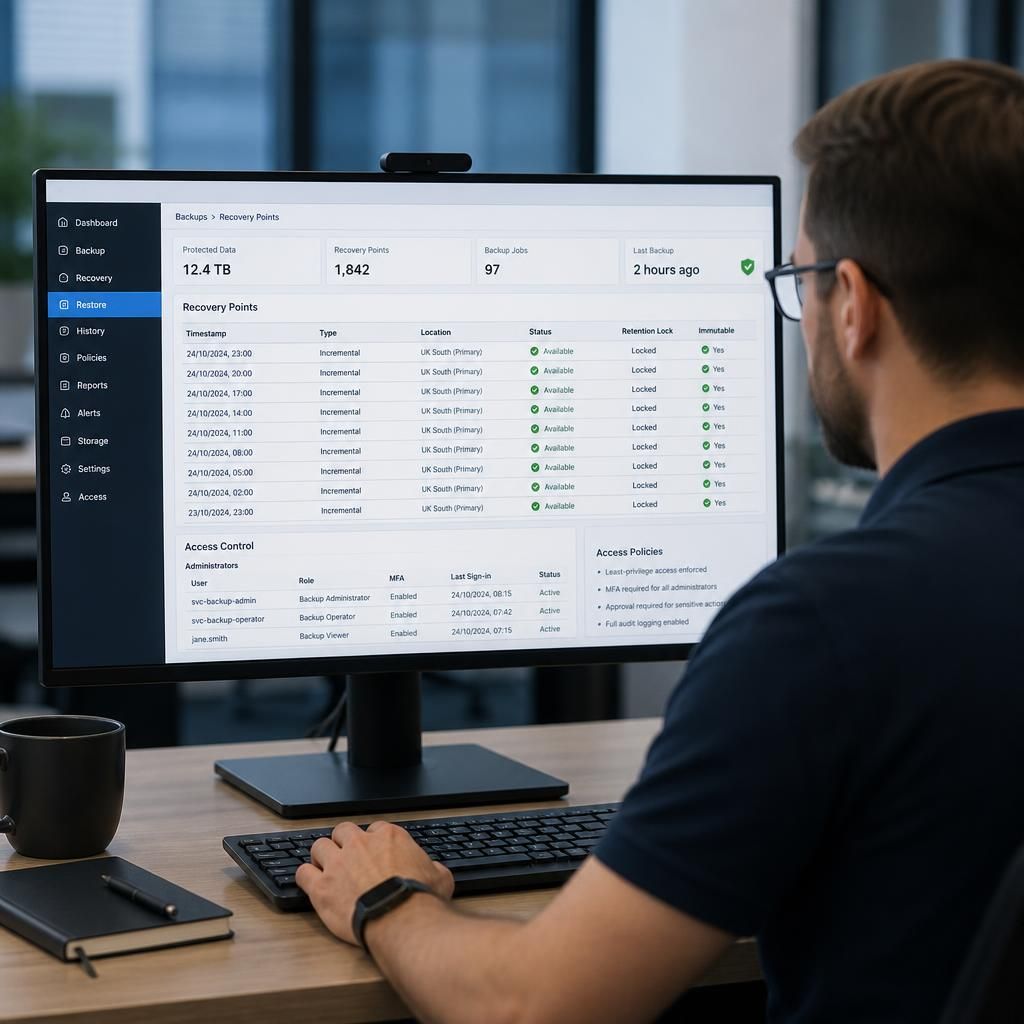
Managed backup protects against a compromised administrator account by preserving a history of recovery points, not just a single copy of current data. This allows an organisation to identify a point from before the account was misused, particularly where an attacker has altered files gradually or concealed changes rather than encrypting everything at once.
Recovery-point selection should therefore consider when suspicious activity began, which systems or data may have been affected, and whether the chosen version contains legitimate, usable information. Where compromise is uncertain, earlier recovery points can be compared with more recent versions and restored in a controlled environment for validation. This helps avoid reintroducing altered files or unsafe configurations when recovering from an administrator-account breach.