
Can cloud backup support compliance requirements?
Cloud backup can support compliance requirements by helping protect business data, control access to backup copies and provide records of backup activity and recovery testing. It does not make an organisation compliant on its own: the backup configuration, retention policy, encryption, user permissions and audit evidence must match the specific legal, regulatory or contractual requirements that apply.
Cloud backup supports compliance when it is designed as part of the organisation’s wider information governance, security and business continuity controls. It can help demonstrate that data is managed consistently, remains available when needed and is handled according to documented policies. However, the relevant regulation, contract or industry framework determines what the backup arrangement must achieve.
Start by mapping the backup service to the applicable requirements. A business should identify which categories of information are backed up, why they are retained, who may access them, where they are processed and when they should be deleted. This assessment should consider requirements arising from the UK GDPR and Data Protection Act 2018, sector-specific rules, customer contracts and internal governance policies. The result should be a written set of backup controls rather than a general assumption that all data needs the same treatment.
For personal data, backup planning may need to address the principles of security, storage limitation and data minimisation. Backups can contain historic copies of records that have since been amended or deleted from live systems, so the organisation should understand how correction, deletion and data subject requests are handled within the backup lifecycle. In some cases, immediate alteration of a protected backup is impractical; the organisation may instead need documented procedures governing restoration, expiry and access to older copies. These decisions should be agreed with the data protection lead or other responsible adviser.
Retention should be based on documented business and regulatory needs. Keeping every backup indefinitely can increase exposure, storage complexity and the quantity of personal information held. Retaining backups for too short a period may prevent the business from meeting contractual, operational or investigation requirements. A suitable policy normally defines retention periods by data type or system, explains exceptions such as legal holds, and specifies how expired copies are securely removed. Retention should also distinguish between operational recovery copies and records that must be preserved as part of a formal archive.
Cloud backup can provide useful evidence for audits when the service and its surrounding processes produce consistent records. Examples include:
- the systems, data sets and devices included within the backup scope;
- policy settings and approved changes, including documented exceptions;
- completed and failed jobs, with investigation notes where a protection task did not run as expected;
- restore exercises showing what was recovered, when it was tested and whether any corrective action followed;
- records of administrative activity and periodic reviews of privileged permissions;
- retention, deletion and legal-hold decisions; and
- supplier due diligence, contractual terms and service review records.
This evidence is most useful when it is understandable to someone who did not configure the service. A compliance reviewer should be able to connect the organisation’s policy to the technical settings, see who approved material changes and identify how exceptions are managed. Exporting reports without maintaining the underlying process may provide limited assurance.
Supplier governance is another important consideration. The organisation remains responsible for understanding how a cloud backup provider processes its information, even where technical operations are delegated. Due diligence may cover the provider’s security controls, subcontractors, data processing terms, incident procedures, data transfer arrangements, deletion process and ability to support audits or investigations. The contract should align with the organisation’s role as controller or processor and with any commitments made to customers or other data subjects.
Compliance planning should also account for the difference between recovery capability and regulatory reporting. Restoring a system may help investigate an incident or resume processing, but it does not replace the organisation’s obligations to assess, document and report a personal data breach where required. Similarly, a successful backup does not prove that the restored application is accurate, complete or fit for normal operation. Recovery tests should therefore include relevant applications, permissions, dependencies and data validation.
A practical review can ask:
- Which legal, contractual and sector requirements apply to each protected system?
- Does the backup scope include the information needed to meet those requirements?
- Are retention, deletion and exception rules documented and consistently applied?
- Can the organisation evidence that recovery procedures have been tested for important systems?
- Are supplier responsibilities, processing arrangements and data transfers understood?
- Can administrators’ actions be reviewed and can inappropriate access be withdrawn?
- Is there a process for investigating failed protection tasks and recording the outcome?
S2 Technology Group can help businesses review these questions as part of a wider cloud backup and IT governance assessment. The objective is to align the service configuration, operating procedures and supporting documentation with the requirements that actually apply, while leaving formal legal interpretation to the organisation’s data protection or compliance adviser.
Compliance evidence is more useful when it can be shown to be trustworthy, complete and protected from unauthorised alteration. Backup records should not be easy for the same account that manages backups to edit or remove without trace. Where appropriate, businesses should restrict administrative permissions, preserve relevant reports in a controlled location and record who reviewed or exported them.
This is particularly important when backup information may support an internal investigation, customer assurance exercise or regulatory review. The organisation should be able to explain the origin of a report, the period it covers and whether any gaps or changes have been identified. These measures do not create compliance by themselves, but they can make the organisation’s evidence more reliable when demonstrating how its backup controls operate.
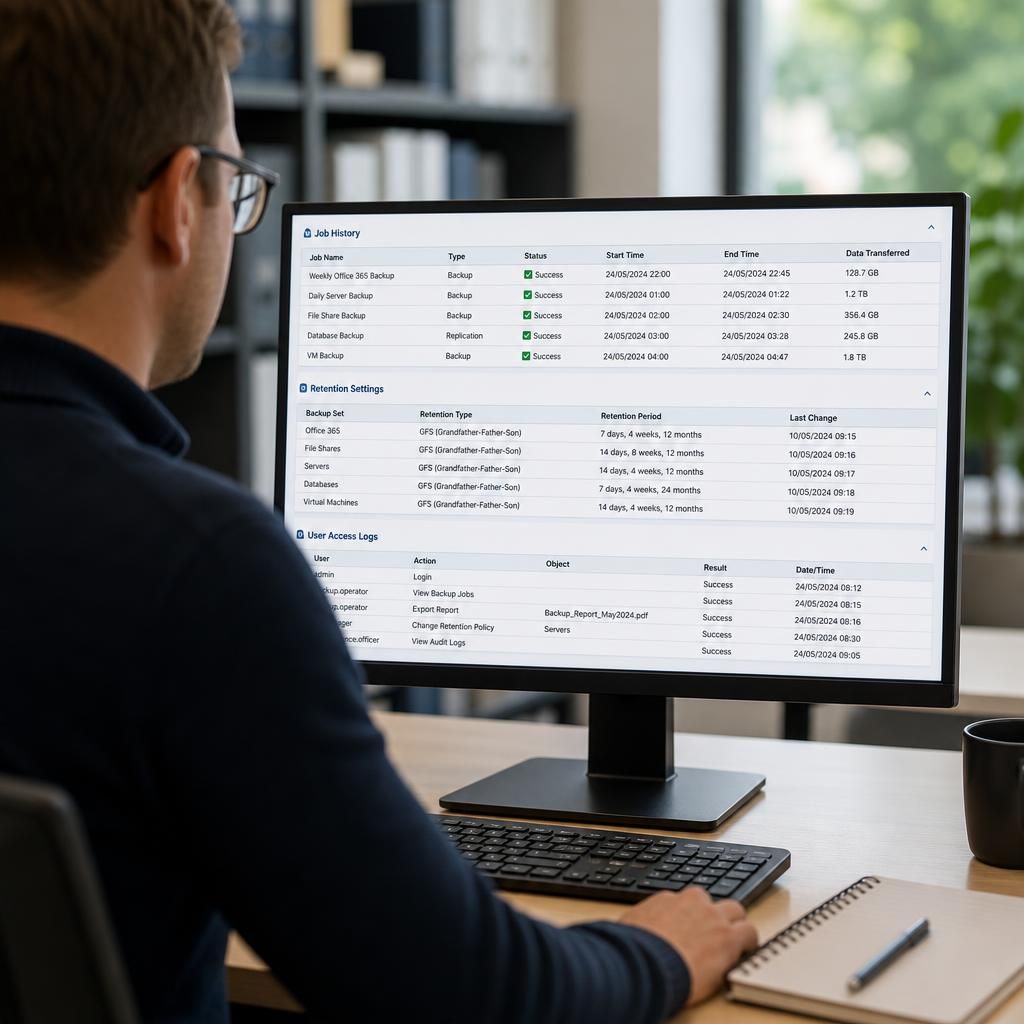
Review your cloud backup compliance requirements
If you are assessing cloud backup for a regulated or contract-sensitive environment, speak to S2 Technology Group about the controls and evidence your arrangement should support. This can help you identify practical questions for your IT, data protection or compliance advisers before making changes.